Keep Calm and Containerd On - Migrating Kubernetes Clusters from Docker to Containerd
Explore Intuit's journey migrating 200+ Kubernetes clusters to containerd, addressing challenges in logging, SELinux, GPU support, and cluster addons. Learn valuable lessons for a smooth transition.
Kubernetes Incidents: Making Logs Work for You in Real-World Troubleshooting
Optimize Kubernetes log analysis for effective incident troubleshooting. Learn to enrich logs with context, navigate observability challenges, and avoid common pitfalls in real-world scenarios.
Mastering Grafana Loki - Kubernetes Log Collection and Integration - Part 2
Learn to set up Loki and Promtail in Kubernetes for efficient log collection and integration. Explore deployment, Grafana connection, log viewing, and Promtail pipelines for enhanced monitoring.
Revamping Kubernetes with Contextual and Structured Logging - A Deep Dive
Explore Kubernetes' new structured logging system, enhancing monitoring with machine-readable, contextual logs. Learn about klog improvements and their impact on the Kubernetes ecosystem.
Build or Buy: Observability Data Pipelines 101
Explore efficient observability data pipeline management for cloud services. Learn to handle massive data volumes, reduce costs, and optimize processing across teams and tools.
Why Do My Logs Suck? A Practical Guide to Improving Your Logs
Practical guide to enhancing log quality for cloud-native systems. Learn strategies for standardizing formats, improving readability, and integrating diverse log sources without extensive code refactoring.
From FluentBit Operator to Fluent Operator - The Evolution of Kubernetes Log Management
Explore the evolution from FluentBit to Fluent Operator, addressing Kubernetes log collection challenges and enhancing dynamic configuration for efficient log management and processing.
Deep Dive: etcd and Raft Consensus Algorithm
Explore etcd's Raft consensus algorithm implementation, its critical role in Kubernetes, and its adoption in other distributed systems. Learn about design philosophy and future developments.
Expanding Into Observability: Modern Application Management
Explore enterprise observability for modern cloud-native applications, covering key concepts, architectural complexity, and strategies for effective management of dynamic, distributed environments.
Log Story Short: Chopping Through Forests of Data
Explore techniques for efficiently analyzing vast log data to enhance application security and incident response in this insightful presentation by security expert Moti Harmats.
Journey from Fluent Bit, Fluentd and Prometheus to OpenTelemetry Collector - Lessons Learned
Explore the transition from multiple telemetry tools to OpenTelemetry Collector, discussing challenges, performance improvements, and simplification of data collection in cloud-native environments.
Connecting Metrics, Logs, and Traces with eBPF - TTChat's Observability Journey
Explore TTChat's journey in building an observability platform using eBPF, connecting metrics, logs, and traces for microservices without code modification across diverse languages and frameworks.
Finding Needles in the Observability Haystack - Managing Kubernetes Monitoring Data
Explore advanced techniques for managing Kubernetes monitoring data, from alerts to AI/ML, with practical insights and tools for effective observability and situational awareness.
CloudSec Rules Everything Around Me - C.R.E.A.M.
Explore cloud security essentials, from shared responsibility to logging, compliance, and incident response. Learn best practices for AWS, Azure, and Office 365 environments.
Determining Normal - Baselining with Security Log and Event Data
Learn effective strategies for baselining security logs and event data to identify anomalies, establish normal patterns, and enhance threat detection capabilities in your organization.
Peel Back the Layers of Your Enterprise and Make Your Adversaries Cry
Explore enterprise security with Security Onion, an open-source platform offering comprehensive visibility. Learn about intrusion detection, network monitoring, and incident response techniques to detect and interrupt adversaries quickly.
Splunk for IR and Forensics
Explore Splunk's capabilities for incident response and forensics, including log analysis, dashboards, alerts, and statistical analysis for effective cybersecurity investigations.
Powershell and Windows Throw the Best Shell Parties
Explore Windows shell parties with PowerShell, learning combat techniques, configuration, and leveraging PowerShell for enhanced system interaction and security testing.
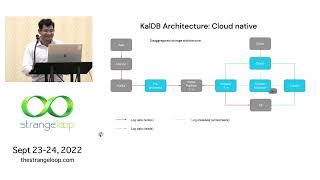
KalDB - A Cloud Native Log Search Platform
Explore KalDB, a cloud-native log search platform addressing Elasticsearch limitations. Learn about its architecture, real-time visibility, automatic field conflict handling, and cost-saving techniques.
Centralized Logging Patterns
Explore centralized logging patterns with demos for parsing, sending, structuring, containerizing, and orchestrating logs. Learn advantages and disadvantages to choose the best approach for your organization.
Running Docker in Production on AWS
Explore tools and strategies for deploying Docker containers in AWS production environments, covering host management, service integration, orchestration, updates, monitoring, and log management.