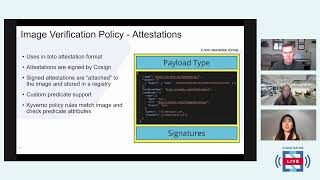
Cloud Native Live - What's New with Kyverno
Explore Kyverno's latest features for cloud-native policy management, including image verification, validation policies, and new operators for enhanced Kubernetes cluster control.
Cloud Native Live: What's New with Kyverno
Explore Kyverno's latest features for cloud-native policy management, including architecture updates, new policy structures, and critical enhancements for improved validation and organizational strategies.
Securing GitOps Supply Chain with Sigstore and Kyverno
Learn to secure GitOps supply chain by signing and verifying container images using Sigstore and Kyverno, eliminating security risks and ensuring only trusted images are deployed in Kubernetes clusters.
Policy Driven Approach to Secure CI/CD Workflow
Explore how Tekton, ArgoCD, and Kyverno can enhance CI/CD pipeline security, compliance, and reliability. Learn to automate policy enforcement and address supply chain vulnerabilities in Kubernetes environments.
Hands-on with Policy Reporter - Kyverno Visibility Tool
Explore Policy Reporter, an open-source tool enhancing Kyverno policy enforcement visibility in Kubernetes. Learn installation, UI features, and integration with monitoring tools.
Kyverno - Deep Dive - Tech Talks
Deep dive into Kyverno 1.9 features: mutation, generation, image verification, cleanup policies, and policy exceptions. Includes demos and best practices for secure software supply chain.
Securing Kubernetes Manifests with Sigstore and Kyverno
Learn to secure Kubernetes resources using Sigstore for signing YAML definitions and Kyverno for verification during admission controls, with real-world use cases for tamper-prevention and approval workflows.
Policy-Based GitOps: How Policies Can Help Secure and Automate GitOps Workflows
Explore how Kubernetes-native policies enhance GitOps workflows, addressing automation and security gaps. Learn to leverage Kyverno with GitOps for improved management across clusters and multi-tenant services.
DockerSlim and Kyverno - Enhancing Kubernetes Workload Security
Explore how DockerSlim and Kyverno enhance Kubernetes workload security through container image minification, automated AppArmor and SecComp profiles, and simplified cluster security management.
Avoiding IAC Potholes with Policy and Cloud Controllers
Discover how to secure self-serve cloud infrastructure for Kubernetes teams using policy engines and cloud controllers. Learn to enforce compliance while enabling application teams to provision resources efficiently.
Deploying Pod Security Policies Using Kyverno - A New Approach
Explore a new approach to deploying Pod Security Policies using Kyverno, addressing the challenges of Kubernetes security and offering a flexible solution for implementing robust pod security measures.
Spicing up Container Image Security with SLSA and GUAC
Explore SLSA and GUAC tools to enhance container image security, verify build provenance, and understand artifact composition for safer deployments in production environments.
Kubernetes Policy Management with Kyverno 1.9
Explore Kubernetes policy management using Kyverno 1.9, covering advanced features and best practices for enforcing security and compliance in cloud-native environments.
Scalable CI/CD Infrastructure with EKS and Karpenter
Explore Grammarly's CI/CD infrastructure management using EKS, Karpenter, and Kyverno. Learn about IAM, network management, and pod mutation for enhanced CI agility.
Navigating Disaster Recovery in Kubernetes and Crossplane - Strategies and Tools for Managing Stateful Workloads
Explore strategies for disaster recovery in Kubernetes and Crossplane, focusing on stateful workloads, GitOps, and tools like Velero and Kyverno for effective platform management.
Kubernetes Policy as Code with Kyverno - Cloud Native Live
Explore Kubernetes policy management with Kyverno, covering use cases, implementation, and features for effective cloud-native governance and security.
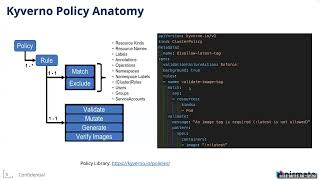
Managing Policy Exceptions in Kubernetes Using Kyverno
Learn to manage policy exceptions in Kubernetes using Kyverno, enhancing cluster security and compliance while maintaining operational flexibility.
Securing Kubernetes Manifests with Sigstore Cosign - Options and Best Practices
Explore options for verifying Kubernetes manifests with Sigstore Cosign. Learn about integrating security solutions, GitOps tools, and policy engines to enforce security policies and prevent unwanted changes in your cluster.
Automate Production-Ready Cluster Using Crossplane Compositions and Kyverno
Learn to automate production-ready Kubernetes environments using Crossplane and Kyverno. Discover how to create resilient, secure clusters with efficient resource management, compliance enforcement, and seamless add-on deployment.
Kubernetes Policy as Code with Kyverno
Explore Kyverno for implementing policy-as-code in Kubernetes, enhancing security and compliance in cloud-native environments.
Securing 900 Kubernetes Clusters - Journey to ValidatingAdmissionPolicies
Explore Mercedes-Benz's journey in securing 900+ Kubernetes clusters, transitioning from Pod Security Policies to ValidatingAdmissionPolicies, and learn about challenges and advantages of native solutions.