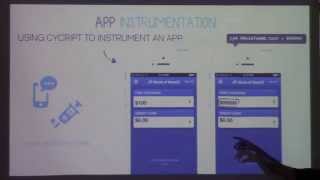
Uncovering OWASP's Mobile Risks in iOS Apps - AppSec California 2015
Explore iOS app vulnerabilities through reverse engineering techniques. Learn to extract, analyze, and identify common security risks in mobile applications using real-world examples.
Runtime Manipulation of Android and iOS Applications - Mobile Security Testing
Hands-on exploration of runtime manipulation and memory analysis techniques for Android and iOS apps, enhancing mobile security testing skills using tools like cycript and snoop-it.
Ten Secrets to Secure Mobile Applications
Discover key strategies for securing mobile apps, focusing on encryption, web service design, and user privacy. Learn to threat model and address top vulnerabilities using OWASP Mobile Top Ten framework.
iOS App Integrity: Enhancing Security with Encrypted Code Modules
Explore iOS app security vulnerabilities and learn advanced protection techniques like Encrypted Code Modules (ECM) to safeguard against static analysis, binary patching, and other common attacks.
Fixing Mobile Application Security - OWASP Mobile Security Testing Guide
Introduction to OWASP Mobile Security Testing Guide and Mobile Application Security Verification Standard, addressing challenges in mobile app security testing and best practices for secure development.
Fixing Mobile Application Security - The OWASP Mobile Project
Explore OWASP's Mobile Application Verification Standard and Security Testing Guide, addressing key mobile app security challenges and best practices for secure data storage, communication, and API usage.
Needle: Finding Issues within iOS Applications
Discover Needle, an open-source framework for streamlined iOS app security assessments. Learn about its modular architecture, capabilities, and how it simplifies vulnerability detection in iOS applications.
iGoat: A Self-Learning Tool for iOS App Security Testing
Learn iOS app security through hands-on exercises with iGoat, an open-source tool for developers and pentesters. Explore vulnerabilities, exploit techniques, and implement fixes in a safe environment.
Testing iOS Apps without Jailbreak - Penetration Testing Techniques
Learn techniques for penetration testing iOS apps without jailbreaking, including live demos on accessing protected resources on the latest iOS version. Ideal for pentesters facing jailbreak limitations.
Smart Storage Scanning for Mobile Apps - Attacks and Exploits
Explore mobile app security vulnerabilities, focusing on local storage attacks. Learn automated scanning techniques for Android and iOS, with live demonstrations and defense strategies.
Hacking Web Server Apps for iOS - Security Risks and Vulnerabilities
Explore iOS web server app vulnerabilities, from XSS to potential RCE. Learn risks, attack vectors, and implications for both jailbroken and non-jailbroken devices in this eye-opening security analysis.
BASHing iOS Applications - Command Line Tools for Mobile Auditors
Explore iOS application assessment using command-line tools. Learn mobile security fundamentals, binary analysis, data storage, and endpoint parsing while addressing OWASP Mobile Top 10 vulnerabilities.
Mobile Rules the World - Jump into Mobile AppSec with the OWASP MAS Project
Explore mobile app security fundamentals, OWASP MASVS V2 updates, and top 5 security issues. Learn testing techniques, prevention strategies, and latest iOS/Android security updates.
Operation Triangulation: Uncovering a Sophisticated Zero-Click Attack on iPhones
Unveiling a sophisticated zero-click iOS attack chain: discovery, analysis, and implications of Operation Triangulation, a highly advanced spyware targeting researchers' iPhones.
iOS URL Schemes: Security Implications and Vulnerabilities
Explore iOS URL schemes and their potential security implications in mobile app development and usage.
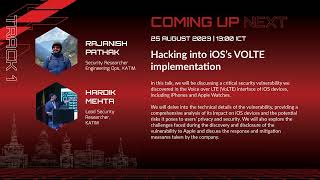
Hacking Into iOS's VoLTE Implementation
Unveiling a critical VoLTE vulnerability in iOS devices, exploring its technical details, impact on user privacy, and Apple's response to this long-standing security flaw in 4G implementation.
Malicious MDM: Exploiting iOS MobileConfigs for Device Control
Explore iOS MDM vulnerabilities, learn attack techniques, and discover preventive measures to protect against malicious mobile device management configurations.
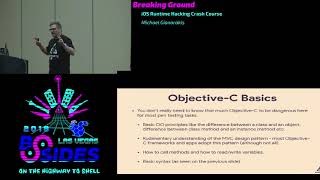
iOS Runtime Hacking Crash Course
Dive into iOS runtime hacking techniques, exploring methods to manipulate and analyze iOS applications for security testing and reverse engineering purposes.
Discovering the iOS Instruments Server
Reverse-engineering of iOS privileged server providing sensitive data to Apple's debugging tools. Explores techniques used to uncover and analyze this critical system component.
Exploiting Userland Vulnerabilities to Get Rogue App Installed Remotely on iOS 11
Exploiting iOS11 vulnerabilities to remotely install rogue apps, bypassing security enhancements and code signing requirements without kernel exploits. Techniques for sandbox escape and persistent installation demonstrated.
Mobile Hacking - OWASP Mobile Project and How to Use It for White Hat Hacking
Explora los proyectos OWASP para seguridad móvil: MASVS para verificación y MSTG para pruebas e ingeniería inversa. Aprende a evaluar y mejorar la seguridad de aplicaciones iOS y Android.