Introduction to Smartphone Malware Forensics
Überblick über Techniken und Open-Source-Tools zur Erkennung von Malware auf iOS- und Android-Smartphones, mit Fokus auf Stalkerware und Staatstrojaner. Praktische Einführung in einvernehmliche Smartphone-Forensik.
Fun with Frida on Mobile - Leveraging Dynamic Analysis Tools
Explore Frida for mobile app analysis: trace functions, examine memory, bypass security. Practical examples for iOS and Android, including SSL pinning bypass and custom tool creation.
BadXNU - Exploiting Vulnerabilities in Apple's XNU Kernel
Explore vulnerabilities in Apple's XNU kernel, uncovering security flaws and potential exploits in iOS and macOS systems.
OWASP Distinguished Lifetime Member Award - Jeff Williams' Contributions
Explore Jeff Williams' contributions to OWASP, including foundational projects, non-profit creation, and innovative security concepts, in this insightful 20th anniversary recognition.
SSL Traffic Interception on Mobile Devices - Analysis and Protection
Análisis detallado de incidentes SSL en aplicaciones móviles, revelando patrones globales, casos notables y soluciones para desarrolladores contra la interceptación de tráfico.
Bugs Ruin Everything - Keynote on Vulnerability Analysis and Exploitation
Explore vulnerability analysis techniques, their strengths and weaknesses, and real-world case studies with security expert Charlie Miller in this engaging keynote from AppSecEU 2016.
OWASP Mobile Top Ten 2014 - The New Lack of Binary Protection Category
Explore the new OWASP Mobile Top Ten category: lack of binary protections. Learn about risks to mobile apps, their impact on the app economy, and strategies to mitigate these threats on iOS and Android platforms.
Mobile Security Track - AppSec Europe 2014
Explore cutting-edge mobile security topics at AppSecEU 2014, covering iOS and Android vulnerabilities, OWASP Mobile Top Ten, smart storage scanning, and practical defense strategies for app developers.
Mobile App Analysis with Santoku Linux
Explore mobile app analysis using Santoku Linux, covering forensics, security testing, and malware analysis for Android and iOS platforms. Live demos showcase practical applications of preinstalled tools.
Mobile Security Attacks - A Glimpse from the Trenches
Explore emerging mobile security threats, from physical to network and application levels, with real-world attack examples and insights from experts who uncovered iOS vulnerabilities.
AppSecUSA 2014 - Breakers Track Sessions
Explore cutting-edge web and mobile security topics, including mobile attacks, use-after-free exploitation, static analysis, runtime manipulation, and top hacking techniques from AppSecUSA 2014.
OWASP Top 10 Mobile Risks: 2014 Reboot
Explore the updated 2014 OWASP Top 10 Mobile Risks, comparing changes since 2011, understanding new threats, and learning recommended fixes for iOS, Android, and Windows Phone platforms.
Escaping the Safari Sandbox: A Tour of Webkit IPC
Explore Webkit IPC vulnerabilities and techniques for escaping the Safari sandbox, gaining insights into browser security and exploitation.
NSPredicate Exploitation on macOS and iOS - Understanding Security Vulnerabilities and Bypasses
Delve into NSPredicate exploitation techniques on Apple devices, exploring security vulnerabilities, bypass methods, and practical demonstrations for executing arbitrary code in privileged iOS processes.
Sexy Mobile App Attacks by Example - 2019
Comprehensive review of security flaws in Android and iOS apps, covering anonymized findings, vulnerabilities in open-source apps, and issues in government-mandated applications. Practical insights for mobile security enthusiasts.
Machswap - Stephen Parkinson
Explore iOS jailbreaking through machswap vulnerability, gaining insights into kernel access techniques and the iOS 12 jailbreak development process.
iOS Hacking - Inter-App Communication Vulnerabilities
Explore iOS inter-app communication vulnerabilities, focusing on pasteboard sharing, URL schemes, and universal links. Learn to use Frida for tracing and testing these mechanisms.
iOS Hacking - Filesystem Basics
Explore iOS app filesystem interactions, data storage methods, and file protection attributes. Learn to analyze artifacts and use runtime instrumentation for comprehensive iOS application security assessment.
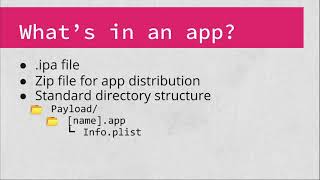
iOS Application Hacking - Understanding IPA Structure and Mach-O Binaries
Explore iOS app structure, IPA files, Mach-O binaries, and techniques to uncover hidden interfaces, API keys, and sensitive data. Learn to analyze and reconstruct app functionality.
OWASP AppSecUSA 2014 - Builders Track Sessions
Explore cutting-edge web security topics including OWASP tools, .NET hacking, iOS integrity, password complexity, and client-side security in this comprehensive AppSecUSA conference session.
Automated Mobile Application Security Assessment with MobSF - AppSec EU 2016
Discover automated mobile app security assessment using MobSF. Learn techniques for identifying vulnerabilities and enhancing protection in mobile applications.