How to Hack OWASP Juice Shop - A Guided Walkthrough Showing All Solutions
Comprehensive guide to mastering OWASP Juice Shop's vulnerabilities, covering all challenges from basic to advanced levels with detailed solutions and explanations.

Beginner Web Application Hacking
Comprehensive introduction to web application hacking, covering enumeration, XSS, SQL injection, broken access control, and more. Includes live bug bounty hunting demonstration.

How to Build a REST API With Node JS & Express
Learn to build a RESTful API using Node.js and Express. Covers server setup, HTTP methods, route parameters, input validation, and using Postman for API testing. Ideal for web developers seeking practical skills.

Saving PHP Website from a Potential XSS Attack - Tutorial 64
Learn to protect your PHP website from XSS attacks. Discover techniques to sanitize user input, validate data, and implement security measures to prevent cross-site scripting vulnerabilities.
API Security 101 by Sadako
Explore API security fundamentals, common vulnerabilities, and real-world examples. Learn testing methodologies, fuzzing techniques, and gain insights from notable bug discoveries in this beginner-friendly introduction.
Web App Testing - XXE, Input Validation, Broken Access Control, and More XSS
Explore advanced web app testing techniques including XXE, input validation, broken access control, and XSS. Enhance your ethical hacking skills and learn to identify critical vulnerabilities.
Error Handling and Security Management in AI Powered Apps - Web Development With AI Episode 7
Learn to handle errors and manage security in AI-powered web apps. Covers bug fixing, input validation, protection against bad actors, and AI-specific attack prevention.
New Methods in Automated XSS Detection - Dynamic Testing Without Static Payloads
Explore innovative dynamic methods for automated XSS detection without static payloads, including techniques for Stored XSS and custom exploit generation. Learn to overcome limitations of traditional approaches.
Unlocking Threat Modeling - Participatory Session on Security Architecture Assessment
Participatory session demystifying threat modeling for security assessment. Learn risk evaluation, architectural decomposition, and appropriate views to enhance system security from the start.
Fixing XSS with Content Security Policy
Learn how Content Security Policy (CSP) can prevent XSS attacks, understand its versions, browser support, and implementation strategies for web applications. Gain insights on balancing CSP with traditional security measures.
Web Application Security: The Secret to Hack-Proof Apps - SQL Injection - Part 2
Discover step-by-step methods to secure web applications from SQL injection threats. Learn to identify vulnerabilities, exploit techniques, and implement effective prevention strategies for robust security.
From ASCII to UTF-16: Leveraging Encodings to Break Software
Explore how character encodings can be exploited to compromise software security, from basic ASCII to complex UTF-16, in this technical IT security talk.
SQL Injection Explained - Understanding Attacks and Prevention
Comprehensive guide to SQL injection attacks: types, vulnerabilities, and prevention techniques. Learn to identify, exploit, and protect against database security threats through practical examples and best practices.
API Security Best Practices - Preventing Vulnerabilities and Hacks
Learn API security best practices, including BOLA vulnerability prevention, testing techniques, and strategies to protect against hacking through a demo-oriented session.
Dumb-Proofing Data Pipelines: Techniques for Configurable and Maintainable ETL - Databricks
Techniques to create configurable, maintainable data pipelines. Learn to externalize configurations, validate inputs, and leverage Scala features for robust, easily deployable ETL processes.
REGEX - How to Match and Search Any Pattern or Validate Input
Comprehensive guide to regular expressions, covering key concepts like matching, searching, and input validation. Learn to solve common pattern-matching problems efficiently.
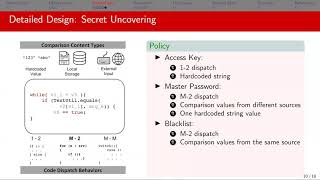
Automatic Uncovering of Hidden Behaviors from Input Validation in Mobile Apps
Uncovers hidden behaviors in mobile apps through input validation analysis, revealing backdoors and blacklists. Presents INPUTSCOPE tool for automatic detection of execution context and content in user input validation.
Advanced Android Studio Hacking - Part 3
Explore Android device hacking using Android Studio with Nick Godshall. Learn emulation techniques, tackle DIVA challenges, and understand responsible disclosure in this comprehensive tutorial.
iOS Hacking - Inter-App Communication Vulnerabilities
Explore iOS inter-app communication vulnerabilities, focusing on pasteboard sharing, URL schemes, and universal links. Learn to use Frida for tracing and testing these mechanisms.
OWASP Top Ten Proactive Controls for Secure Web Development
Learn essential secure coding techniques for web development, covering validation, authentication, access control, encoding, data protection, and secure architecture to build robust and protected applications.
How to Build a REST API With Laravel - PHP Full Course
Learn to build, version, and secure RESTful APIs with Laravel. Master database design, data transformation, filtering, resource manipulation, and authentication using Sanctum for robust back-end development.