Keep You Data Safe in a Containerized Application
Explore challenges and solutions for persisting data in containerized applications, focusing on Docker runtime and proven techniques for modern, scalable systems.
Don't Worry, Your Credit Card Details Are Safe. BTW Your Kid Is Missing!
Exploring security vulnerabilities in a Norwegian parenting app, demonstrating how simple techniques can expose sensitive data and compromise user privacy. Emphasizes ethical testing and responsible disclosure.
Everything You Always Wanted to Know About Azure Security But Were Afraid to Ask
Comprehensive guide to Azure security features, covering administrative control, data protection, perimeter security, application-level hardening, and monitoring. Includes practical examples and a security checklist for Azure solutions.
Emerging Web Security Standards
Explore cutting-edge web security standards like CAA, CT, SameSite Cookies, and OCSP Expect-Staple. Learn how these innovations enhance encryption, monitoring, and threat mitigation for secure websites.
What's New in ASP.NET Core 2.0
Explore major features like Razor Pages and .NET Standard 2.0, along with smaller improvements across the ASP.NET Core 2.0 stack. Learn about new templates, authentication, configuration, and hosting enhancements.
Building a Global App With Azure PaaS
Learn to design and create a global ASP.NET Core app using Azure PaaS services, including traffic routing, caching, scripted deployment, and security features for efficient and scalable development.
Web Application Security Risks - A Look at OWASP Top Ten 2017
Explore the latest OWASP Top Ten 2017 security risks for web applications. Learn about changes, updates, and best practices for creating secure web applications in this comprehensive overview.

Keynote - Are There Any Questions?
Exploring the evolution of human inquiry and its intersection with technology, from mechanical calculators to AI, and the implications for our future relationship with machines.
Hacking Humans - Social Engineering Techniques and How to Protect Against Them
Explore social engineering tactics, their impact on organizations, and learn effective strategies to protect yourself and your company from manipulation and security breaches.
Continuous Security
Explore integrating security into Agile development, focusing on tools, techniques, and processes for building secure software without compromising velocity or innovation.
Security in ASP.NET Core 2.0
Explore new security features in ASP.NET Core 2.0, including authentication, authorization, and cryptographic key management. Learn to build flexible, secure web applications.

Running a Bug Bounty Program at SEEK
Discover how SEEK successfully implemented a bug bounty program, inviting hackers to test their web applications. Learn about the benefits, challenges, and lessons learned from this innovative security approach.
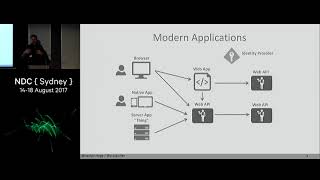
Implementing Authorization in Web Applications and APIs
Learn strategies for implementing robust authorization in web applications and APIs, exploring various approaches, pitfalls, and the ASP.NET Core authorization API to create clean and effective authorization systems.
Reverse Engineering a Bluetooth Lightbulb
Reverse engineer a Bluetooth lightbulb's protocol to create build lights integrating with TeamCity. Learn low-level Bluetooth communication, protocol analysis, and packet sniffing for practical IoT applications.
Where's My Free Lunch?
Explore the hidden costs of "free" digital services and open-source software, examining their impact on privacy, data, and societal implications in the modern tech landscape.
The Code Behind The Vulnerability
Explore advanced web security vulnerabilities beyond SQL injection, focusing on issues in dictionaries, compression, and encryption to enhance your code's resilience against sophisticated attacks.
Security and Microservices
Explore microservices security: defense in depth, distributed architecture protection, and strategies to enhance data safety while minimizing attack surfaces.
.NET Data Security - Hope is Not a Strategy
Learn essential .NET data security techniques including encryption, hashing, and digital signatures to protect sensitive information and ensure data integrity in your applications.

Threat Modeling
Analyze system design to identify security weaknesses and missing controls. Learn techniques to uncover threats in your systems through threat modeling.
.NET Data Security - Hope is Not a Strategy
Learn essential .NET data security techniques including encryption, hashing, and digital signatures to protect sensitive information and ensure data integrity in your applications.
Hack Back - Bug Hunting on the Dark Side
Explore hilarious bugs in real-world malware, from typos to overlooked dependencies, in this entertaining and eye-opening talk on exploiting attacker mistakes.