Security Framework Challenges & Solutions
Explores physical layer security challenges and solutions for embedded devices, focusing on authentication schemes, feature extraction from wireless modules, and practical implementation methodologies.
Animated Bugs - The New Remote Attack Surface in Telegram
Exploring Telegram's animated stickers implementation in E2EE chats, uncovering 13 zero-day vulnerabilities through advanced fuzzing techniques and binary exploitation.
Hunting for Malicious Infrastructure Using Big Data
Explore innovative machine learning techniques for detecting malicious infrastructure in HTTP responses, focusing on uniqueness and header order features to identify command and control servers.
Reversing GO Binaries With Ghidra
Exploring techniques for reverse engineering Golang binaries using Ghidra, focusing on IoT malware analysis, overcoming Go-specific challenges, and addressing recent obfuscation trends.
Alt-Payments and Crypto - The Future Is Now
Exploring key trends in alternative payments and cryptocurrencies, including industry perspectives, future directions, and challenges for investors in this rapidly evolving financial landscape.
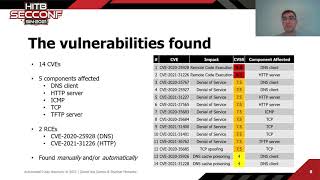
Squashing Low-hanging Fruit in Embedded Software
Discover advanced techniques for identifying and mitigating critical vulnerabilities in embedded systems, focusing on NicheStack TCP/IP stack vulnerabilities and automated vulnerability detection methods.
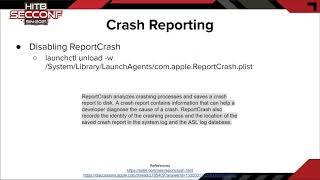
Summer of Fuzz - MacOS
Explore overlooked attack surfaces on macOS through fuzzing techniques. Learn to bypass security protections, debug effectively, and use new tools for crash triage in Apple core apps and services.
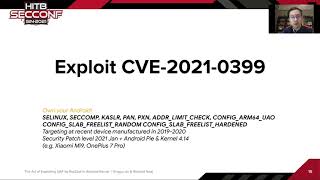
Exploiting UAF by Ret2bpf in Android Kernel
Exploiting a 10-year-old Use-After-Free vulnerability in Android's xt_qtaguid kernel module, demonstrating local privilege escalation on Mi9 device using ret2bpf technique to bypass protections.
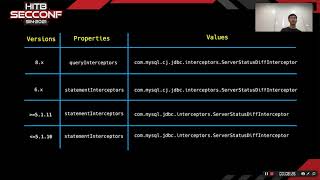
Make JDBC Attacks Brilliant Again
Explore advanced JDBC attack techniques, including 0day vulnerabilities in popular systems. Learn about XXE and RCE issues, and gain insights from experienced security researchers.
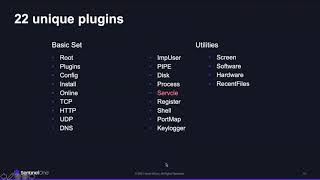
SHADOWPAD - Chinese Espionage Malware-as-a-Service
Comprehensive analysis of SHADOWPAD malware: its origin, usage patterns, and business model. Explores its impact on Chinese cyber espionage and the evolving threat landscape.
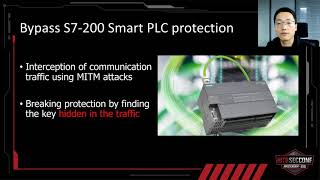
Breaking Siemens SIMATIC S7 PLC Protection Mechanism
Detailed analysis of vulnerabilities in Siemens SIMATIC PLC protection mechanisms, including hacking methods and security recommendations for various models. Essential for industrial control system security professionals.
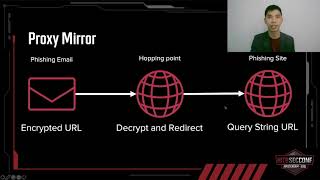
Dissecting Phishing Techniques of CloudDragon APT
Análisis detallado de las sofisticadas técnicas de phishing del grupo APT norcoreano CloudDragon, incluyendo casos reales, métodos para evadir la autenticación de dos factores y propagación a sistemas Android.
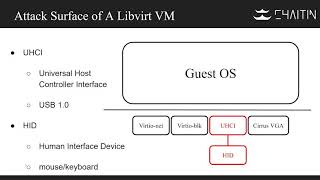
A QEMU Black Box Escape Via USB Device
Exploring a QEMU virtual machine escape technique using USB device vulnerabilities, focusing on black box scenarios without prior system information for enhanced cloud security.
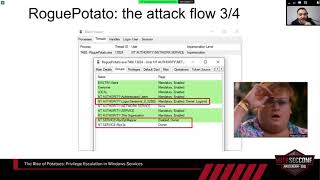
The Rise of Potatoes - Privilege Escalation in Windows Services
Exploring advanced privilege escalation techniques in Windows services, including a new 0day NTLM relay attack. Covers recent methods, Windows Service Hardening, and the RemotePotato0 attack vector.
Hack Out of the Box - Discovering 10+ Vulnerabilities in VirtualBox
Discover 10+ VirtualBox vulnerabilities through custom fuzzing techniques. Learn about attack surfaces, exploit primitives, and see a live box escape demonstration.
A Hipster History of CORS
Explore the evolution of CORS, its historical context, and modern cross-origin standards. Gain insights into web security and learn how to design secure web applications effectively.
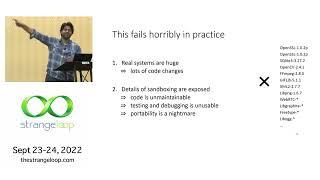
Don't Get Owned by Your Dependencies
Explore innovative techniques for mitigating memory safety vulnerabilities in third-party C libraries, focusing on Firefox's lightweight in-memory sandboxing approach and the RLBox framework for efficient, secure application development.
SIEM There, Done That - Rising Up in the SecOps Revolution
Explore the future of cybersecurity through automation and intelligence, moving beyond traditional SIEM solutions to address modern SecOps challenges and usher in a new era of protection.
The New Ground Truth for Security
Explore how infrastructure can establish a new ground truth for cybersecurity professionals, addressing misinformation and advanced threats in today's complex digital landscape.
Threat Response Needs New Thinking - Don't Ignore This Key Resource
Discover innovative approaches to threat response, focusing on leveraging your network as a crucial asset for real-time attack detection and enhanced resilience against cybersecurity challenges.
The Looming Identity Crisis
Explore the challenges of securing identity in the AI era and discover innovative solutions to prevent an impending crisis in cybersecurity.