E'rybody Gettin' TIPC - Demystifying Remote Linux Kernel Exploitation
Demystifying remote Linux kernel exploitation through a stack overflow vulnerability in a network module, offering insights into the exploit development process and low-level kernel internals.
Attacking WPA3 - New Vulnerabilities And Exploit Framework
Uncovers critical vulnerabilities in WPA3, including DoS attacks and traffic interception. Presents a new Wi-Fi testing framework for researchers to identify and exploit these weaknesses in various devices.
Random Walk Through A Few Million Things
Explore IoT security challenges in enterprises, examining millions of devices to reveal vulnerabilities, default credentials, and outdated firmware. Gain insights into the current state of IoT security.
Exploiting Race Condition Vulnerabilities in Web Applications
Explore race condition vulnerabilities in web apps, their impact, and exploitation techniques. Learn about detection challenges, real-world scenarios, and a new penetration testing tool for identifying these elusive security flaws.
Getting Clear Text Passwords From An IdP & More
Explore privilege escalation in Okta, including methods to obtain clear text passwords and impersonate super-admins. Learn about knowledge graphs for trust analysis in vulnerability discovery and research collaboration.
Advanced Code Obfuscation With MBA Expressions
Explore advanced code obfuscation techniques using Mixed Boolean-Arithmetic expressions to increase data-flow complexity and conceal sensitive data, with practical applications in building robust obfuscation primitives.

Cracking Kyocera Printers
Explore vulnerabilities in Kyocera printers, including remote DoS, file reading, password leakage, and pre-auth RCE. Learn how these security flaws can be exploited to access office networks and monitor confidential documents.
Web3 + Scams = It's A Match
Explore 35+ types of cryptocurrency scams, from traditional replicas to novel Web3-specific schemes. Learn about pump and dump, rug pull, and unique scams like proof of weak hands and NFT airdrops.
Building an Army of Bots by Hijacking a Twitter Handle
Revealing security vulnerabilities in mobile apps that expose Twitter API keys, allowing potential account takeovers and unauthorized actions. Explores causes, impacts, and prevention techniques.
Faking at Level 1 - How Digital Twins Save Your PLCs
Explore digital twin technology for safely testing and identifying vulnerabilities in industrial control systems without risking operational infrastructure.
API Security Through External Attack Surface Management
Integrating APIs into External Attack Surface Management to improve security posture. Discover and assess exposed assets, including APIs, for better protection and risk mitigation.
Hack In The Studio - Fireside Chat
Fireside chat with security experts Cristofaro Mune and Adam Laurie, discussing their extensive experience in hardware hacking, embedded systems security, and reverse engineering techniques.
Hack In The Studio - Fireside Chat
Fireside chat with cybersecurity experts Stefano Zanero and Marco Balduzzi, discussing their research, experiences, and insights in malware analysis, cyberphysical security, and emerging threats in the digital landscape.
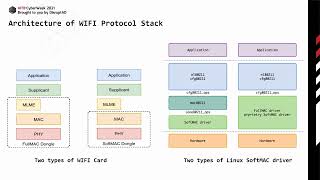
WIFI Security - From 0 To 1
Comprehensive guide to WiFi vulnerabilities, covering protocol basics, attack surfaces, and auditing techniques. Includes real-world examples and introduces a custom WiFi protocol stack fuzzer.
Military Bioweapons Development and Information Warfare
Explores coordinated military efforts in the GCC region, focusing on biological weapons development and information warfare strategies for national defense. Insights from field experience shared.
ARM IoT Firmware Extraction and Emulation Using ARMX
Hands-on workshop on extracting and emulating ARM IoT firmware using ARMX. Covers firmware extraction, unpacking, file system analysis, and device emulation. Practical experience with real IoT devices and tools.
EXPLIoT Framework - An Introduction to IoT Security Testing
Explore IoT security with EXPLIoT framework. Learn key concepts, tools, and protocols for penetration testing and exploit development in IoT environments. Hands-on workshop for security researchers and pentesters.
How to Defeat EDRs in Usermode
Explore advanced techniques to bypass Endpoint Detection and Response (EDR) systems, including PID spoofing, DLL blocking, and syscalls. Learn from experts and get inspired to innovate in cybersecurity.
Attacking Automated Manufacturing Systems
Explores attack surfaces and vulnerabilities in automated manufacturing systems, discussing potential impacts on product quality, plant safety, and industrial espionage in Industry 4.0 environments.
Hacking the Planet With Knowledge Graphs
Explore innovative approaches to cybersecurity for complex systems using knowledge graphs, graph theory, and machine learning. Learn to plan and execute effective engagements across diverse technological landscapes.
Gremlin Apps and Gremlin Botnets
Exploring the risks of BYOD policies and the potential for malicious apps to create targeted attacks on corporate devices, highlighting covert channels and opportunistic permissions.