Browsers Gone Wild
Unveiling creative browser vulnerabilities and attacks, including confidentiality breaches, login detection, and exploiting HTML5 features, with live demonstrations challenging Same Origin Policy understanding.
Exploiting Social Navigation
Discover techniques to compromise social navigation systems through fake GPS reports and bot drivers, exploring privacy risks and traffic manipulation in applications like Waze.
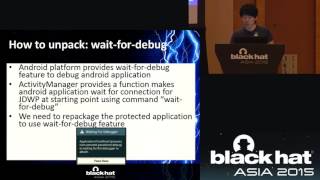
We Can Still Crack You - General Unpacking Method for Android Packer - No Root
Discover a novel method for unpacking protected Android applications without root access. Learn to bypass anti-analysis techniques and reveal hidden code in packed apps.
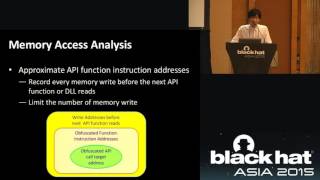
API Deobfuscator - Identifying Runtime-Obfuscated API Calls Via Memory Access Analysis
Unveils a resilient API deobfuscation technique using memory access analysis, overcoming limitations of pattern-based approaches to identify runtime-obfuscated API calls in malware and obfuscated code.
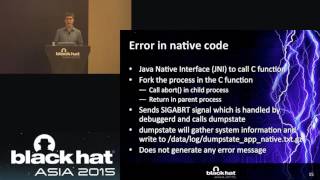
Resurrecting the Read Logs Permission on Samsung Devices
Exploit allowing non-privileged apps to access sensitive log data on Samsung devices, bypassing Android's READ_LOGS permission restrictions. Reveals private information from notifications and system logs.
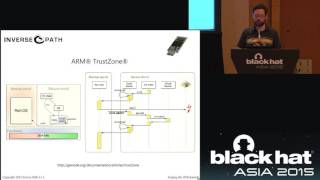
Forging the USB Armory
Explore the development of an open-source USB-sized computer for security applications, featuring advanced SoC technology, secure boot, and ARM TrustZone implementation.
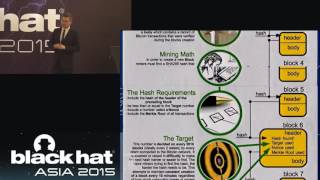
Decentralized Malware on the Blockchain
Explore the potential threat of embedding malware in blockchain transactions, its implications for cybersecurity, and possible solutions to mitigate risks in decentralized systems.
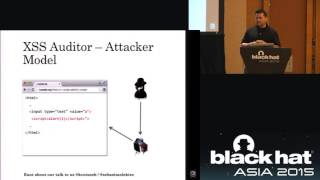
Client-Side Protection Against DOM-Based XSS Done Right
Comprehensive analysis of Chrome's XSS Auditor, revealing vulnerabilities and proposing an improved filter design using client-side taint tracking for robust DOM-XSS protection.
AndroBugs Framework - An Android Application Security Vulnerability Scanner
Explore AndroBugs Framework, a free Android vulnerability analysis system. Learn to identify and mitigate security risks in Android apps before release, enhancing app safety and user protection.
A Peek Under the Blue Coat
Detailed analysis of Blue Coat ProxySG systems, exploring OS mechanisms, file system internals, and security features. Insights for IT professionals managing web traffic proxying and filtering.
Silently Breaking ASLR in the Cloud
Exploit memory deduplication to defeat ASLR in cloud environments, leaking randomized base addresses of libraries and executables in neighboring VMs using a side-channel attack.
Even The LastPass Will Be Stolen, Deal With It!
Uncover vulnerabilities in LastPass password manager, including methods to steal master passwords, bypass 2FA, and access encrypted vaults, highlighting the importance of robust security measures.
Attacking the XNU Kernel in El Capitan
Explore new techniques to bypass XNU kernel exploit mitigations in El Capitan, including KASLR and SMEP, and learn how to overcome System Integrity Protection through a real kernel exploit demonstration.
Cybersecurity for Oil and Gas Industries - How Hackers Can Manipulate Oil Stocks
Explore critical cybersecurity vulnerabilities in oil and gas industries, focusing on SAP and Oracle systems. Learn about potential attacks, their impacts, and strategies for protecting vital infrastructure and operations.

Bypassing Self-Encrypting Drives in Enterprise Environments
Explore SED vulnerabilities, their impact on data protection, and strategies for safeguarding against new threats in enterprise environments.
What Got Us Here Won't Get Us There
Explore InfoSec challenges, industry distractions, and harmful practices. Learn to tackle real problems, avoid security antipatterns, and embrace simplicity for effective cybersecurity strategies.
PWNIE Awards
Celebrating excellence in information security with humor and recognition for groundbreaking achievements and epic fails in the cybersecurity industry.
Information Access and Information Sharing - Where We Are and Where We Are Going
Exploring DHS's vision for rapid, widespread cybersecurity information sharing across sectors. Discusses challenges and the goal of making threat indicators a public good for enhanced network defense.
Untangling the DOM for More Easy-Juicy Bugs
Explore dynamic JavaScript analysis with Hookish!, an open-source Chrome extension for penetration testing. Learn to uncover DOM-based vulnerabilities and enhance web app security assessments.
Breaking Payloads With Runtime Code Stripping and Image Freezing
Innovative defensive strategy to break attack payloads by removing unused code and APIs from application processes, enhancing security without runtime overhead or file modifications.
Review and Exploit Neglected Attack Surfaces in iOS 8
Explores overlooked iOS 8 vulnerabilities through fuzzing and code auditing, revealing system daemon crashes and memory corruption errors triggerable via XPC, plus an iOS kernel 0day.