Breaking FIDO - Are Exploits in There?
Explore FIDO authentication's vulnerabilities, potential exploits, and protective measures for enterprises in this comprehensive analysis of the protocol's security landscape.
Iran's Soft-War for Internet Dominance
Análisis detallado de las campañas de intrusión cibernética de Irán contra disidentes, críticos y organizaciones internacionales, revelando patrones y objetivos de vigilancia y control.
Weaponizing Data Science for Social Engineering - Automated E2E Spear Phishing on Twitter
Automated spear phishing on Twitter using machine learning and social engineering techniques. Explores target profiling, content generation, and high-value target identification for more effective phishing campaigns.
Attacking BYOD Enterprise Mobile Security Solutions
Exposé des failles de sécurité des solutions BYOD et EMS, avec démonstration d'attaques et présentation d'un nouvel outil, Swizzler, pour contourner les protections sur appareils jailbreakés ou non.
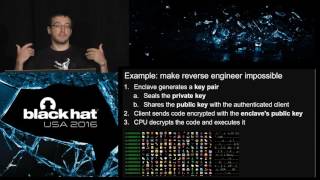
SGX Secure Enclaves in Practice - Security and Crypto Review
Explore Intel's SGX technology for secure remote computation, including its implementation, development environment, cryptographic aspects, and potential applications in secure storage and delegation.
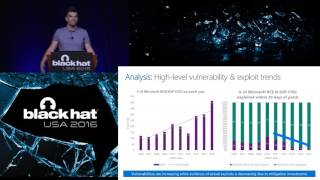
Windows 10 Mitigation Improvements
Explore Microsoft's data-driven approach to software security, including proactive monitoring, analysis of exploits, and mitigation improvements in Windows 10 to enhance protection against vulnerabilities.
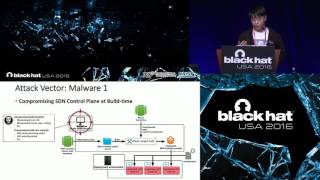
Attacking SDN Infrastructure - Are We Ready for the Next-Gen Networking?
Exploring SDN vulnerabilities through attacks on control plane, channel, and data plane. Demonstrates critical exploits affecting network availability and confidentiality, and introduces SDN security projects.
An Inconvenient Trust - User Attitudes Toward Security and Usability Tradeoffs
Exploring user perspectives on encryption methods, balancing security and usability in digital communications. Insights from a study on key-exchange vs. key-directory models for everyday messaging.
Over the Edge - Silently Owning Windows 10's Secure Browser
Exploiting Windows 10's memory deduplication feature to silently compromise Microsoft Edge, bypassing security measures and gaining arbitrary memory access through JavaScript-based attacks.
Pay No Attention to That Hacker Behind the Curtain - A Look Inside the Black Hat Network
Insider look at the notorious Black Hat network, revealing infrastructure, traffic patterns, and security challenges faced by one of the most hostile networks on the planet.
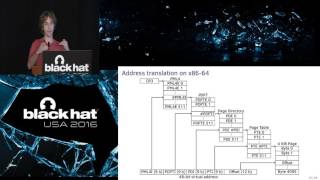
Using Undocumented CPU Behavior to See Into Kernel Mode and Break KASLR in the Process
Explore undocumented CPU behavior to breach kernel security, map memory, and bypass KASLR. Learn techniques for kernel introspection and physical-to-virtual address conversion without special privileges.
Gathering Threat Intelligence on Telephony Scams to Detect Fraud
Explore techniques for gathering threat intelligence on telephony scams, including robocalling and voice phishing. Learn to detect and fingerprint bad actors using audio features and data analysis.
Defense at Hyperscale - Technologies and Policies for a Defensible Cyberspace
Explore strategies for achieving defensible cyberspace through innovative technologies, operational improvements, and policies that prioritize defense over offense in the digital realm.
Hacking the Wireless World with Software Defined Radio 2.0
Explore diverse wireless systems using software-defined radio. Learn to analyze, reverse engineer, and exploit RF signals for applications ranging from space probes to aircraft tracking and RFID systems.
Slime - Automated Anti-Sandboxing Disarmament System
Automated system to disarm malware with anti-sandbox techniques, focusing on host-fingerprinting and general anti-sandboxing. Analyzes exit reasons and suggests suitable environments for dynamic analysis of evasive malware.
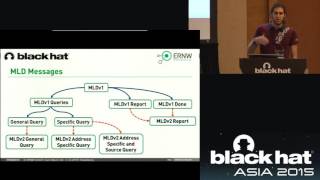
MLD Considered Harmful - Breaking Another IPv6 Subprotocol
Explores security vulnerabilities in IPv6's Multicast Listener Discovery protocol, demonstrating potential exploits and proposing mitigation techniques for safer IPv6 network implementation.
The Nightmare Behind the Cross Platform Mobile Apps Dream
Explore security vulnerabilities in popular cross-platform mobile development frameworks and their implications for app developers and users.
I Know Where You've Been - Geo-Inference Attacks Via The Browser Cache
Explore geo-inference attacks via browser cache, revealing how websites can sniff users' locations. Learn about vulnerabilities in popular sites, impact on various browsers, and potential defenses against these privacy threats.
Relaying EMV Contactless Transactions Using Off-The-Shelf Android Devices
Unveils vulnerabilities in EMV Contactless payments, demonstrating relay attacks using common Android devices. Explores implications for transaction security and public acceptance of contactless payments.
Bypassing Malware Detection Mechanisms in Online Banking
Explore vulnerabilities in online banking malware detection systems, revealing implementation errors and potential improvements for enhanced security.
Hiding Behind Android Runtime - ART
Explore techniques for creating user-mode rootkits in Android using ART mechanisms, including file formats, persistence methods, and limitations, with a live demonstration.