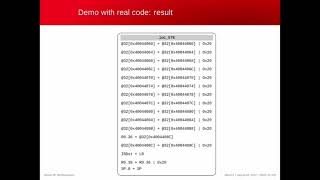
Miasm - Reverse Engineering Framework
Explore Miasm's reverse engineering capabilities, from basic framework to symbolic emulation and malware analysis tools. Learn disassembly, code emulation, and advanced techniques for tackling complex software.
Those Don't Matter! Effective Prioritization Through Exploit Prediction
Discover a machine learning classifier for data-driven vulnerability prioritization, enhancing risk management strategies and improving decision-making in cybersecurity.
iOS Jailbreak Internals - Userland Read-Only Memory Can Be Dangerous
Explora las vulnerabilidades en la memoria de solo lectura de iOS, analizando ataques DMA y explotando fallas en IOSurfaceAccelerator para lograr ejecución de código arbitrario y jailbreak.
A Hacker's Guide to Career Progression
Explore hacking career progression strategies, from risk-taking to problem-solving, mentorship, and giving back. Learn to navigate your journey based on technical preferences and salary aspirations.

Detecting Credential Compromise in AWS
Learn techniques to detect and mitigate credential compromise in AWS, a widespread concern for cloud-based companies. Explore various attacker motives and outcomes.
Qualitative Look at Autonomous Peer Communication's Impact on Organizational Phishing Detection
Explore how autonomous peer communication enhances organizational phishing detection through user education and marketing tools in information security awareness programs.
Why the World Must Take Notice of the Rising Asian Dark Web
Explore the rising Asian dark web markets, their usage patterns, and user motivations. Gain insights into new research findings across various Asian countries' dark web landscapes.
Finding Xori - Malware Analysis Triage with Automated Disassembly
Explore automated malware analysis using Xori, an open-source tool for efficient triage and disassembly. Learn to process high volumes of malware and improve analysis capabilities at scale.
Dissecting Non-Malicious Artifacts - One IP at a Time
Uncover the risks of security product interactions with online scanners, exploring information leaks, zero detection issues, and practical examples for improved cybersecurity.
PeriScope - An Effective Probing and Fuzzing Framework for the Hardware-OS Boundary
Explore PeriScope, a Linux-based framework for analyzing device-driver interactions, enabling passive monitoring and active fuzzing to enhance hardware-OS boundary security.
I'm Unique, Just Like You - Human Side-Channels and Their Implications for Security and Privacy
Explore unintentional human-generated identifiers in digital security, their uses in attack and defense, and countermeasures. Gain insights into "human side-channels" and their privacy implications.
Finding a Needle in an Encrypted Haystack
Discover new techniques to exploit NTLM authentication, including a critical zero-day vulnerability enabling domain-wide machine takeover, even with strict security configurations.
Intel VISA - Through the Rabbit Hole
Explore Intel's internal architecture, PCH devices, and security-sensitive data access. Learn to read signals from internal buses and discover hidden components within Intel chips.
I'm Unique, Just Like You - Human Side-Channels and Their Implications for Security and Privacy
Explore human side-channels: unintentional digital identifiers from human behaviors, their implications for security and privacy, and potential countermeasures.
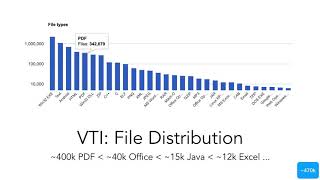
Worm Charming - Harvesting Malware Lures for Fun and Profit
Explore YARA rules for extracting malware samples from VirusTotal, learning techniques to identify attacker infrastructure and analyze real-world threats.
ACSploit - Exploit Algorithmic Complexity Vulnerabilities
Explore techniques to identify and exploit algorithmic complexity vulnerabilities, focusing on inefficient worst-case scenarios and their impact on program performance and security.
Minimum Failure - Stealing Bitcoins with Electromagnetic Fault Injection
Electromagnetic fault injection attack on Trezor Bitcoin wallet revealed, allowing seed extraction without physical tampering. Implications for embedded USB stacks and cryptocurrency security explored.
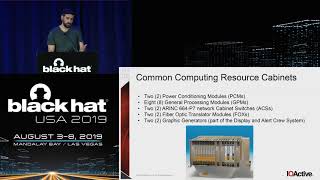
Arm IDA and Cross Check - Reversing the Boeing 787's Core Network
Uncover vulnerabilities in Boeing 787's Core Network through reverse engineering, revealing security flaws and their implications for aircraft systems and passenger safety.
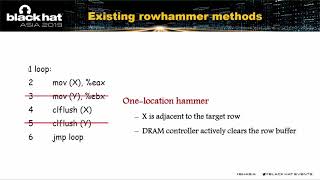
Winter is Coming Back - Defeating the Most Advanced Rowhammer Defenses to Gain Root and Kernel Privileges
A novel exploit breaking advanced rowhammer defenses, allowing unprivileged applications to gain root and kernel privileges. Stealthier and more efficient than existing exploits, this talk presents key steps and implications.
PicoDMA - DMA Attacks at Your Fingertips
Explore PicoDMA, a compact FPGA-based platform for DMA attacks. Learn about its capabilities, hardware, and potential security implications using the affordable PicoEVB board.
A Decade After Bleichenbacher '06, RSA Signature Forgery Still Works
Explores RSA signature forgery vulnerabilities, revealing new CVEs and discussing prevention strategies through dynamic symbolic execution analysis of signature verification implementations.