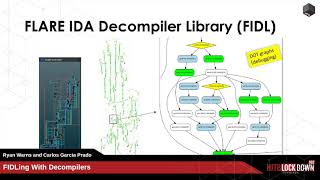
FIDLing with Decompilers
Explore decompilation basics, popular tools, and the Hex-Rays Decompiler. Learn about FIDL, a new library simplifying decompiler API usage, with practical examples and demos.
Zen - A Complex Campaign of Harmful Android Apps
Explore Android malware techniques, from repackaging apps to sophisticated rooting trojans. Learn about click fraud, exploit bundling, and persistence mechanisms used by malicious actors.
Secret Flaws of In-DRAM RowHammer Mitigations
Unveiling secret flaws in DRAM RowHammer mitigations, exploring Target Row Refresh implementation, and introducing TRRespass: a RowHammer fuzzer for creative hammering patterns to bypass protections.
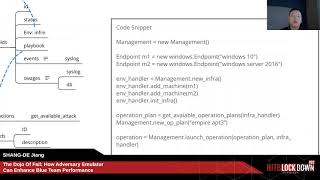
How Adversary Emulation Can Enhance Blue Team Performance
Explore adversary emulation to enhance blue team performance, addressing cybersecurity expert shortages and evolving attack methods. Learn to design attack playbooks and test security products effectively.
Bugrank - A Community Bug Bounty Platform
Introducing Bugrank: an open-source community bug bounty platform. Explore its design, architecture, and functions. Learn how to set up your own bug reporting system for enhanced cybersecurity.
Army of Undead - Tailored Firmware Emulation
Explore automated firmware emulation techniques for embedded systems, covering root filesystem location, architecture identification, and emulation methods using open-source tools and scripts.
Breaking and Securing Cloud Platforms
Comprehensive analysis of cloud security vulnerabilities, real-world attack scenarios, and best practices for securing cloud deployments. Covers data exposure, access control issues, and attacker exploitation techniques.
Fuzzing File System Implementations to Uncover Security Bugs
Explore file system vulnerability research through fuzzing techniques on BSD systems. Learn to identify attack surfaces, automate testing, and uncover security bugs in kernel implementations.
Documents of Doom - Infecting macOS via Office Macros
Explore macOS vulnerabilities through Office macros, analyzing recent attacks and detailing a novel exploit chain that can infect fully-patched systems with minimal user interaction.
Exploiting Directory Permissions on macOS
Explore macOS directory permission vulnerabilities, from arbitrary overwrites to privilege escalation. Learn techniques to control file contents and understand the intricacies of macOS security.
Analyzing Recent Evolutions in Malware Loaders
Análisis detallado de la evolución reciente de los cargadores de malware, sus técnicas de evasión y distribución, y métodos para detectarlos y analizarlos en entornos corporativos.
The Insecurity of Cloudless Smart Door Systems
Explore vulnerabilities in cloudless smart door systems for large buildings, focusing on IP-gateway security risks and potential exploits in intercom-IP integration.
Open Source Security – Vulnerabilities Never Come Alone
Explore open source security challenges, variant analysis techniques, and real-world case studies. Learn about vulnerabilities in popular software and gain insights from industry expert Fermin J. Serna.
RIDL - Rogue In Flight Data Load
Unveiling RIDL attacks: exploiting speculative execution vulnerabilities in modern CPUs to steal in-flight data across security boundaries, bypassing existing mitigations and compromising system security.
LoRaWAN Auditing
Comprehensive guide to LoRaWAN security auditing, covering vulnerabilities, testing methods, and new tools. Provides practical insights for securing IoT deployments in smart cities and industries.
The Road to Building Defendable Systems
Explore challenges faced by CISOs, including threat landscapes, expertise shortages, and compliance burdens. Learn effective strategies for building defendable systems and functioning on the razor's edge of cybersecurity.
Reimplementing Local RPC in .Net
Reimplementing Windows RPC in .NET for privilege escalation, covering ALPC implementation, NDR parsing, and PowerShell integration. Includes bug discovery and tooling demonstration.
The Impact of Blockchain and Cryptocurrencies
Explore blockchain's impact on currency, governance, and global power dynamics. Discover how this technology challenges traditional financial systems and reshapes national sovereignty.
The Sum of All Fears - When ICS - SCADA Are Compromised
Explore ICS/SCADA cybersecurity threats, attack vectors, and protection strategies. Learn to analyze industrial protocols, write exploits, and implement effective defense measures for critical infrastructure.
Vote of No Confidence - Second Factor Correctness
Explora la seguridad y verificabilidad del voto electrónico, proponiendo un innovador protocolo de autenticación de dos factores para garantizar la integridad electoral sin comprometer la privacidad.
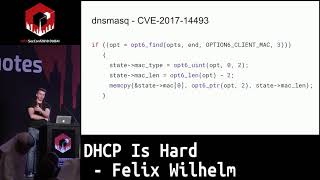
DHCP Is Hard
Explore DHCP vulnerabilities and exploits in popular implementations, including dnsmasq, ISC DHCP, and systemd networkd, with insights on architecture and attack techniques.