The Hunt for Major League IoT-ICS Threats - A Deep Dive into IoT Threat Terrain
Explore IoT security threats, automated threat hunting techniques, and advanced analysis methods to protect against malicious actions targeting millions of connected devices.
Attacking IOBluetoothFamily HCI and Vendor-Specific Commands
Explores vulnerabilities in Bluetooth stacks, focusing on Host-Controller Interface (HCI) and vendor-specific commands. Demonstrates attack techniques and discusses security implications for MacOS and iOS devices.
Bypassing NGAV for Fun and Profit
Explore methodologies to reverse engineer and bypass next-generation anti-virus (NGAV) models, focusing on adversary learning techniques and challenges in cybersecurity.
LadderLeak - Breaking ECDSA with Less than One Bit of Nonce Leakage
Explores ECDSA vulnerabilities, focusing on nonce leakage attacks. Presents LadderLeak, a novel technique breaking ECDSA with minimal nonce exposure, and discusses implications for cryptographic implementations.
POSWorld - Should You Be Afraid of Hands-On Payment Devices
Explore the vulnerabilities of Point of Sale terminals, uncovering security flaws in hardware, software, and file systems that enable cloning and fraud in the dark market.
Hacking Government Cybersecurity
Explore latest cybersecurity developments in government, risk management at scale, and collaboration with industry and hackers. Learn about hacking mindset and cyber volunteering.
How Embedded TCP-IP Stacks Breed Critical Vulnerabilities
Explore critical vulnerabilities in embedded TCP/IP stacks, their impact on system security, and techniques for analysis and mitigation in networked embedded systems.
Cells to Silicon - Your Brain in 2050
Explore cutting-edge brain-machine interactions with leading neuroscientists and experts, discussing advancements in neural technology, consciousness replication, and the future of human-machine integration by 2050.
The Weakest Element of Acquiring Bank Infrastructure
Exploring vulnerabilities in Terminal Management Systems for card payments, revealing potential security risks in acquiring bank infrastructure and POS terminals.
SAP RCE - The Agent Who Spoke Too Much
Explore SAP vulnerabilities: authentication bypass, OS command injection, and privilege escalation. Learn to decrypt sensitive files, manipulate security reports, and implement protective measures.
Hacking the DevOps Butler - From Nothing to Admin
Explore Jenkins vulnerabilities and exploitation techniques, focusing on two critical flaws that allow unauthenticated attackers to gain admin access and control entire infrastructures.
Jackpotting Fortune-500 Treasuries
Unveiling critical vulnerabilities in ERP systems, demonstrating how attackers can manipulate financial processes and exploit Oracle's ERP for unauthorized monetary gains without detection.
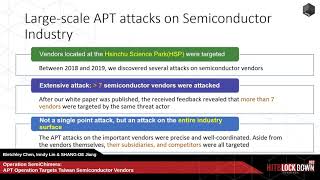
Operation SemiChimera
Análisis detallado de ataques APT a la industria de semiconductores en Taiwán, enfocándose en Operation SemiChimera. Explora técnicas, tácticas y motivaciones de los atacantes, ofreciendo insights para mejorar la ciberseguridad del sector.
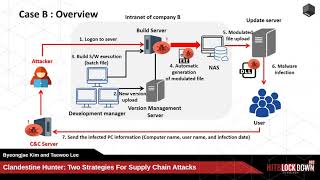
Two Strategies for Supply Chain Attacks
Explore two supply chain attack strategies by BARIUM APT group, analyzing real-world cases and their tactics. Learn defensive measures against these sophisticated cyber threats.
Common Flaws in ICS Network Protocols
Análisis de vulnerabilidades comunes en protocolos de red ICS, incluyendo públicos y privados. Demuestra ataques potenciales como inyección de comandos y sniffing de tráfico sin cifrado en infraestructuras críticas.
DevSecOps, Chaos Security, and Not Being Left Behind
Exploring DevSecOps and Chaos Security Engineering to integrate business, development, and security teams for effective product security and staying ahead of adversaries.
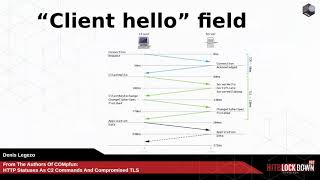
HTTP Statuses as C2 Commands and Compromised TLS
Explore innovative malware techniques using HTTP statuses as C2 commands and compromising TLS encryption. Learn about COMPFun's evolution and its impact on cybersecurity.
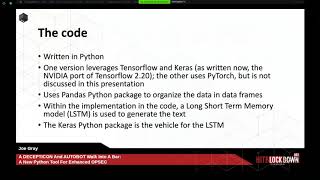
Python for Enhanced OPSEC
Python-based tool for enhancing OPSEC by autonomously posting on social media, using NLP and ML to mimic user behavior. Ideal for those needing to abandon targeted accounts without alerting adversaries.
How to Hack Medical Imaging Applications via DICOM
Explore critical security vulnerabilities in DICOM servers, protocols, and libraries used in medical imaging systems. Learn to identify and fix bugs in the DICOM ecosystem.
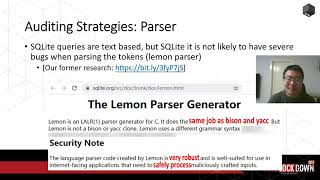
Exploring and Exploiting the SQLite
Explore SQLite vulnerabilities, auditing strategies, and fuzzing techniques. Learn about Magellan 2.0, shadow tables, and bypassing defense mechanisms for remote code execution in Chrome and SQLite binaries.
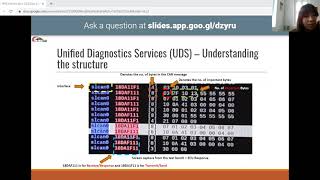
Car Hacking
Explore car hacking essentials: CAN types, UDS, ISO TP, MOST/LIN/Flexray/Automotive Ethernet protocols. Gain insights from industry experts in this virtual lab on automotive cybersecurity.