Analyzing iOS Apps - Road from AppStore to Security Analysis Report
Toolset for detecting vulnerabilities in iOS apps: download and decrypt, decompile, statically analyze, and present results. Focuses on high-level semantics reconstruction and common mobile app security flaws.
Breaking Code Read Protection on the NXP LPC-Family Microcontrollers
Explore bypassing Code Read Protection in NXP LPC microcontrollers through bootloader exploitation and glitch attacks. Learn hardware/software design for a simple glitcher to disable CRP and access FLASH contents.
Hackable Security Modules - Reversing and Exploiting a FIPS 140-2 Lvl 3 HSM Firmware
Exploring vulnerabilities in Hardware Security Modules (HSMs) through firmware analysis and reverse engineering of the TMS320C64x DSP architecture, with focus on the Utimaco SecurityServer.
Recon 2017 Brussels - r2m2 by Guillaume "guedou" Valadon
Presentation on r2m2, a radare2 plugin leveraging miasm2 for reversing rare CPU architectures. Demonstrates integration of powerful reverse engineering tools and simplifies implementation of new architectures.
A Little Less Conversation, A Little More ActionScript
Techniques for in-depth reverse engineering of Flash, mapping ActionScript to undocumented counterparts, and analyzing vulnerabilities in Adobe Flash Player for improved exploit research.
GRAP - Define and Match Graph Patterns Within Binaries
Herramienta para detectar patrones en código binario mediante coincidencia de grafos. Permite definir firmas personalizadas para identificar variantes de malware y extraer información valiosa.
Hacking the Most Popular Cryptocurrency Hardware Wallets
Explore vulnerabilities in popular cryptocurrency hardware wallets with experts Thomas Roth and Dmitry Nedospasov, uncovering potential security risks and attack vectors.
X Ray Reverse Engineering
Explore advanced X-ray reverse engineering techniques with expert George Tarnovsky, uncovering hidden hardware secrets and enhancing your security analysis skills.
Burned in AshesBaseband Fairy Tale Stories
Exploring remote protocols in Baseband, reverse engineering methodologies, and bug discovery in mobile communication systems.
Snow Crashing Virtual Reality - 2019 Edition
Exploring security flaws in VR games leading to remote code execution, highlighting privacy concerns and the need for developers to prevent abuse in online AR/VR communities.
Mining Disputed Territories - Studying Attacker Signatures
Explore attacker dynamics and signatures in cyber conflicts, leveraging insights for proactive defense and enhanced situational awareness in the cybersecurity landscape.
The Unseen Dangers of Bloatware
Explore critical vulnerabilities in pre-installed software on Dell and Lenovo PCs, examining the security risks posed by bloatware and the balance between convenience and user safety.
The Road to Qualcomm Trust Zone Apps Fuzzing
Explore Trusted Execution Environment vulnerabilities in Qualcomm's TEE, reverse engineering techniques, and fuzzing methods for TrustZone apps in mobile device security research.
MINimum Failure - Stealing Bitcoins with Electromagnetic Fault Injection
Electromagnetic fault injection attack on Trezor Bitcoin wallet reveals recovery seed without physical tampering. Explores vulnerability, demonstrates attack method, and discusses countermeasures for hardware wallets.
The Last Generic Win32K KASLR Defeat in Windows
Detailed exploration of Windows kernel security, focusing on KASLR defeats, heap vulnerabilities, and recent changes in RS4. Insights into potential exploits and current Windows KASLR state.
Attacking Hexagon Security Analysis of Qualcomm's ADSP
Explore Qualcomm's Hexagon ADSP security, architecture, and exploitation techniques. Learn reverse engineering methodologies for proprietary systems and mitigations bypass on Android devices.
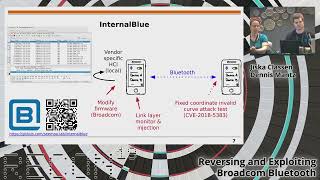
Reversing and Exploiting Broadcom Bluetooth
Insights into reverse engineering Broadcom Bluetooth firmware, including InternalBlue framework, patching techniques, and discovered vulnerabilities CVE-2018-19860 and CVE-2019-6994.
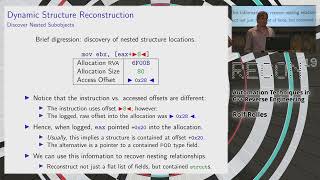
Automation Techniques in C++ Reverse Engineering
Explore automated dynamic analysis techniques for C++ reverse engineering, focusing on structure usage, function argument types, and inheritance relationships through DLL injection.
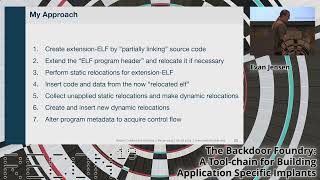
Backdoor Foundry - A Toolchain for Building Application Specific Implants
Explore the creation of application-specific implants using ELF files. Learn about executable containers, software build lifecycle, and advanced techniques for backdoor development in this in-depth technical presentation.
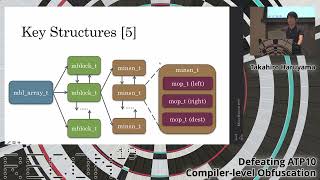
Defeating APT10 Compiler-level Obfuscation
Explore techniques to automatically de-obfuscate APT10's ANEL malware, focusing on opaque predicates and control flow flattening. Learn to modify IDA Pro plugins for effective malware analysis.
The Path to the Payload - Android Edition
Uncover sophisticated Android malware techniques: obfuscation, anti-analysis, encrypted configs, and fake commands. Learn to reverse-engineer and reveal hidden payloads in this advanced security deep-dive.