Analyzing TRISIS - The First Safety Instrumented System Malware
Detailed analysis of TRISIS malware targeting safety systems, blending hardware and software reverse engineering. Explores PowerPC payloads, Triconex firmware, and discusses implications for industrial control security.
Taint-Based Return Oriented Programming
Explore an intermediate approach to return oriented programming using taint-based analysis, balancing speed and query expressiveness for efficient gadget discovery and chaining.
Recovering Software Architecture from Embedded Binaries
Discover techniques for recovering software architecture from large binaries using CodeCut and local function affinity, with applications in automated module-to-module call graphs and section naming.
Sandbagility - Reverse Engineering Framework for Windows Dynamic Analysis
Hybrid framework for Windows malware analysis combining dynamic and sandbox approaches. Offers stealthy, adaptive solution to reduce analysis time, demonstrated with WannaCry case study.
Rattle - An Ethereum EVM Binary Analysis Framework
Explore Rattle, an innovative framework for analyzing Ethereum smart contracts, enhancing auditability and security in blockchain interactions through advanced binary analysis techniques.
Teaching Old Shellcode New Tricks
Explore advanced techniques to bypass security measures and enhance Metasploit x86 shellcode, incorporating automation for improved effectiveness in various deployment scenarios.
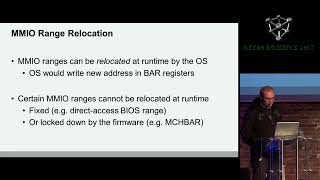
Baring the System - New Vulnerabilities in SMM of Coreboot and UEFI Based Systems
Unveiling new vulnerabilities in SMM of Coreboot and UEFI systems, exploring impacts, and discussing mitigation techniques. Includes release of CHIPSEC module for automatic detection.
Legacy Crypto Never Dies
Explore legacy cryptography vulnerabilities and the crack.sh API for breaking DES-based protocols, with insights from David Hulton's research on widely used services still relying on outdated encryption.
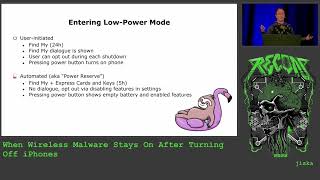
When Wireless Malware Stays on After Turning Off the Phone
Explore iPhone's wireless capabilities after shutdown, including Find My and Digital Car Key. Learn about potential security risks and firmware modifications for low-power Bluetooth malware.
Under the Hood of Wslink Multilayered Virtual Machine
Análisis detallado de la máquina virtual multicapa Wslink, explorando técnicas de ofuscación avanzadas y presentando un enfoque semiautomático para desobfuscar el malware de forma eficiente.
A Dirty Little History
Unveiling "Branch History Injection": A new attack bypassing hardware defenses against Spectre-v2. Explore reverse engineering, exploit development, and the latest mitigations in CPU security.
The Mysterious Life of an Exception
Explore exception handling mechanics, from throw to catch, uncovering runtime interactions, DWARF unwinding, and LSDA. Introduces a Binary Ninja plugin for extracting exception info from binaries.
Under the Hood of Wslink Multilayered Virtual Machine
Detailed analysis of Wslink loader's advanced virtual machine obfuscator, exploring its techniques and demonstrating a semiautomatic deobfuscation approach using symbolic execution and concrete value treatment.
Samsara Metamorphic Engine
Explore Samsara, a viral metamorphic engine for JVM that transforms compiled targets, complicating analysis and enabling supply chain attacks from within IDEs, with added anti-debugging features.
OopsSec - The Bad, the Worst, and the Ugly of APT
Unveiling critical mistakes in APT campaigns across global threat actors, revealing advanced TTPs, and exploring real-time monitoring of sophisticated attacks. Insights on improving organizational defense against evolving threats.
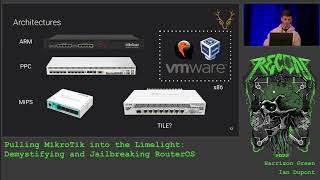
Pulling MikroTik into the Limelight
Explore MikroTik's RouterOS internals, including IPC protocols, message formats, and cryptography. Learn about a new remote jailbreak and gain insights to accelerate RouterOS security research.
Hacking Toshiba Laptops
Unveiling Toshiba laptop vulnerabilities: BIOS password recovery exploitation and EC firmware signing key extraction, enabling stealth rootkit implantation. Implications for newer models discussed.
Neurosurgery for Industrial Routers - Security of Sarian OS
Explore vulnerabilities in industrial routers, focusing on Digi WR21 and Sarian OS. Uncover internal workings, network protocols, and security features of critical infrastructure devices.
Linux Vulnerabilities, Windows Exploits - Escalating Privileges with WSL
Explore WSL vulnerabilities and Windows kernel exploitation techniques. Learn about reverse engineering, syscall manipulation, and bypassing modern anti-exploitation defenses to achieve privilege escalation.
Decompiler Internals - Microcode
Explore the intermediate language used in Hex-Rays Decompiler, its simplicity and power in representing programs, and plans for publication and programmatic access.
When Virtual Hell Freezes Over - Reversing C++ Code
Automated techniques for reversing complex C++ code, focusing on rebuilding inheritance, identifying templates, and tracing program flow to simplify the reverse engineering process.