Secret Management in Kubernetes: Using Secret Store CSI Driver
Explore secure secret management in Kubernetes using Secret Store CSI Driver. Learn its architecture, multi-credential provider support, and see code examples for robust security implementation.
Kubernetes Environments Visualization - Strategies and Solutions at GitLab
Explore GitLab's approach to visualizing Kubernetes environments, managing access, and leveraging the GitLab platform for effective environment management and resource visualization.
Perceptual Hashing: Finding Visual Similarities Between Images - Rust and Tell
Explore perceptual hashing techniques for identifying visual similarities between images, with practical applications and insights shared by Jan Stępień.
L3AF - Complete Lifecycle Management of eBPF Programs
Explore L3AF, an open-source daemon for managing eBPF programs across hosts. Learn about its control plane, configuration capabilities, and integration with Cilium's eBPF library for metrics collection.
Kubernetes Code of Conduct - Working for the Community
Panel discussion on Kubernetes' Code of Conduct, exploring its application, incident response process, and community impact. Learn how it fosters a safe, respectful environment and contributes to the Kubernetes community.
RBAC to the Future: Untangling Authorization in Kubernetes
Explore Kubernetes RBAC essentials, from its inner workings to enterprise-level strategies. Learn to design, automate, and monitor least-privilege configurations for enhanced security and efficiency.
The Hacker's Guide to Kubernetes - Exploiting Vulnerabilities and Best Practices
Interactive demos showcasing live Kubernetes hacking, exploring OWASP Top 10 vulnerabilities and exploits. Learn to identify and mitigate security risks in k8s clusters, containers, and components.
Canals and Bridges: Using Amsterdam's Transit System to Secure Kubernetes Networks
Explore Kubernetes network security through Amsterdam's canal system analogy. Learn threat modeling, monitoring tools, and NetworkPolicies to implement robust security strategies for complex K8s environments.
Cert-Manager for SPIFFE: Solving Multi-Cloud Workload Identity - Lecture
Explore how cert-manager leverages SPIFFE to solve multi-cloud workload identity challenges, enabling secure pod access across different cloud environments.
Compliance at the Point of Change: Security and Developer Independence
Explore innovative platform engineering approaches that enhance security, compliance, and developer autonomy while accelerating business value delivery in cloud-native environments.
Operating Tekton with Secure Defaults
Explore secure approaches for Tekton Pipelines, balancing flexibility with robust safeguards. Learn to implement Trusted Tasks and remote resource resolution for enhanced security in CI/CD workflows.
The Missing Chapter in Your CI Playbook - Database Guardrails
Explore essential database guardrails for CI pipelines, enhancing reliability and efficiency in cloud-native development environments.
Prometheus and Falco: The Swiss Army Knife for SREs - Cloud Native Live
Explore how Prometheus and Falco empower Site Reliability Engineers with robust monitoring, alerting, and security capabilities for cloud-native environments.
Deploying Policy-as-Code with Readable Rego Policies and Open Policy Agent
Learn to implement Policy-as-Code using Open Policy Agent and Rego language. Explore deployment strategies, centralized management, and best practices for writing clear, effective policies in cloud-native environments.

Kubernetes Exposed - One YAML Away from Disaster
Explore real-world Kubernetes security vulnerabilities, common errors, and exploitation techniques. Learn to detect and mitigate risks in internet-connected clusters based on actual cybersecurity experiences.
Unlocking the Power of Collaboration and Troubleshooting in Kubernetes with Botkube
Enhance Kubernetes collaboration and troubleshooting with Botkube, a powerful tool for streamlined cluster management and real-time issue resolution.
Exotic Runtime Targets: Ruby and Wasm on Kubernetes and GitOps Delivery Pipelines
Explore Ruby and WebAssembly deployment on Kubernetes, examining GitOps pipelines and the evolving landscape of runtime environments for developers seeking innovative solutions beyond traditional JavaScript.
Save Your Pipelines with Tekton Results - Improving CI/CD Infrastructure Stability
Explore Tekton Results for archiving and querying pipeline data, improving CI/CD infrastructure stability, performance, and usability in Kubernetes environments.
Flux at the Point of Change - Using Kubernetes Golang SDK and Flux API to Automatically Fix and Deploy CVEs - Lecture
Explore automated CVE remediation in Kubernetes using Client-Go SDK and Flux API. Learn to enhance security across enterprise applications and golden images.
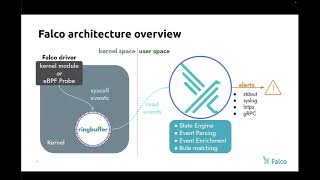
Detecting Five Famous Exploits with Falco
Explore real-world cybersecurity threats and learn to detect them using Falco, enhancing your ability to protect cloud-native environments from sophisticated attacks.
Mastering Kubernetes Access Management
Explore advanced Kubernetes access management techniques, focusing on security best practices and efficient user authorization strategies for cloud-native environments.