DevSecOps: More Than Just Pipelines
Explore DevSecOps beyond pipelines, covering key concepts, application security, and practical strategies for integrating security into the development lifecycle.
The Transformation of DevOps and InfoSec in AIoT
Explore the convergence of AI, IoT, DevOps, and InfoSec in AIoT, examining transformations, challenges, and security implications for modern tech landscapes.
Beyond the Basics: Securing JavaScript Applications
Explore advanced JavaScript application security techniques, from understanding cyber attack chains to implementing network isolation and restrictive IAM permissions.
Incident Response for Developers
Learn essential incident response strategies for developers, focusing on security incidents, your role during crises, and effective communication with AppSec teams.
Synergizing Threat-Informed Defense
Explore threat-informed defense strategies for cloud environments, covering defensive measures, cyber threat intelligence, and testing methodologies to enhance cybersecurity effectiveness.
How to Prove the Safety of Your Software
Explore software safety through SBOMs: Learn to create, analyze, and distribute software bills of materials for enhanced security and transparency in your applications.
Security Chaos Engineering: Fix Things and Make Friends
Explore security chaos engineering to improve defenses, manage chaos, and foster collaboration. Learn to build experiments, measure reliability, and ask better questions for enhanced cybersecurity.
Incident Response: A Scientific Approach to Improving System Reliability
Explore scientific approaches to incident response, challenging traditional methods and emphasizing hypothesis-driven strategies for improved reliability in platform engineering.
Iterative Threat Modelling - Security in Agile Development
Learn iterative threat modeling for agile development. Explore misconceptions, methodologies, and practical examples using OWASP Juice Shop. Discover effective ways to identify, prioritize, and mitigate security risks.
Securing the Software Supply Chain - Beyond SBOM Risk Assessment
Explore advanced software supply chain security strategies, focusing on risk assessment, contributor profiles, project dynamics, and integrating security into deployment pipelines.
Why We Need Security Domains: A Comprehensive Approach to Cybersecurity
Explore essential cybersecurity domains, from compliance to hacking, and understand their importance in developing comprehensive security strategies for modern organizations.
Detecting Known Unknowns in DevSecOps - A Tailored Defensive Approach
Explore TTP-based threat hunting with the Pandora Project. Learn about tailored defensive solutions, methodology workflows, and practical use cases for detecting known unknowns in cybersecurity.
Hacking Demos: Dangerous Lies and Asset Intelligence in IoT Security
Explore hacking demos, asset intelligence, and XIoT vulnerabilities. Learn about common attack types, see live industrial device hacks, and discover remediation strategies for enhanced cybersecurity.
Adding Security for Reliable Continuous Delivery
Enhance security in continuous delivery: Learn containerization challenges, vulnerabilities, misconfigurations, supply chain attacks, and IAM. Explore solutions and see a practical demo.
Supply Chain Attacks: Focusing on NPM Vulnerabilities - DevSecOps 2023
Explore supply chain attacks focusing on NPM, learn defensive strategies, and discover research findings on vulnerabilities in package ecosystems. Gain insights into detection tools and solutions.
Building an LLM Vulnerability Scanner to Secure AI Applications
Develop an LLM vulnerability scanner to audit and secure AI applications. Learn about LLM security risks and build a CLI tool for detecting vulnerabilities in AI systems.
Who Secures Our Code When an Army of Robots Is Writing It? - DevOps Security Challenges in AI-Driven Development
Explore challenges and solutions for securing AI-generated code, including paved roads, runtime protection, and security tool copilots. Learn about CodeModder, an open-source library for modern code modification.
Security Concerns in Every Stage of the Software Supply Chain
Explore security concerns throughout the software supply chain, from development to deployment. Learn strategies to mitigate risks and enhance overall security posture in DevOps practices.
Deep Learning with Differential Privacy
Explore deep learning techniques for privacy-preserving machine learning, focusing on neural networks and differential privacy in crowdsourced, sensitive datasets.
Ending Open Source Security Fatigue - Lessons from Major Vulnerabilities
Explore strategies to streamline open-source security responses, reducing disruption while maintaining resilience. Learn from past incidents to implement effective countermeasures against vulnerabilities in popular packages.
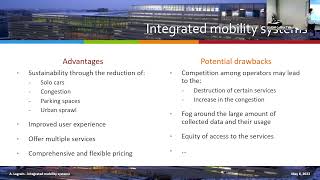
Operational Challenges in Integrated Mobility Systems - DS4DM Coffee Talk
Explore operational challenges in integrated mobility systems, focusing on synchronization, sustainability, and ethical considerations for improved user experience and reduced emissions.