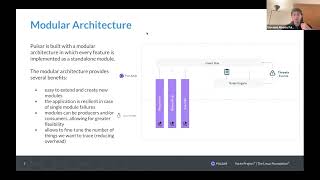
Embedded Runtime Security with Pulsar - YPS 2023.11
Explore Pulsar, an eBPF-powered threat detection system for IoT. Learn its architecture, capabilities, and integration with Yocto Project for enhanced embedded system security.
Yocto Project Security: Now and the Future - YPS 2023.11
Explore Yocto Project's 2023 security updates and upcoming 2024 features, including CVE scanning, SBOM generation, and default options.
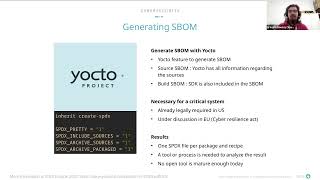
The LF Energy Seapath Project: Yocto Applications in Power Grid Automation
Explore SEAPATH, an open-source platform for power grid substation automation. Learn about its development, transition to virtualization, and the role of Yocto in cybersecurity, SBOM, CI/CD, and licensing.
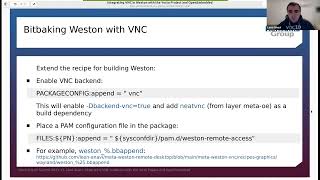
Integrating VNC and Weston with the Yocto Project and OpenEmbedded
Explore VNC support in Weston 12 for remote desktop sharing. Learn to build core-image-weston, set up TLS, and connect remotely using Vinagre in this step-by-step guide.
Updates of Yocto-Based Projects - YPDD 2023
Discover strategies for seamlessly updating Yocto-based projects, addressing security, minimizing debt, and integrating new features with practical examples.
Detecting and Fixing CVE Security Issues in Yocto-Based Embedded Linux Distributions - Mikko Rapeli
Detect and fix CVE security issues in Yocto-based embedded Linux distributions using CVE checker. Learn best practices, common problems, and effective solutions for maintaining high-quality software projects.
Let Devs Be Devs Without Sacrificing Security
Explore flexible, secure CI pipelines using Tekton, Chains, and Enterprise Contract to balance developer innovation with robust security measures for various software targets.
Hitchhikers' Guide to the Vulniverse
Explore key elements of vulnerability disclosure and management, including CVE, CVSS, CWE, and VEX. Gain insights into communication between security teams and researchers.
Enforcing Organization Policies with Enterprise Contract
Learn to enforce organizational policies on container images using Enterprise Contract, leveraging Sigstore signatures and in-toto attestations within the Tekton ecosystem.
Nation-State Threats in the Open-Source Software Supply Chain
Explore North Korean cyber threats targeting software developers through malicious npm packages, focusing on Lazarus Group campaigns and their evolving tactics to steal cryptocurrency.
Exploring a Risk Approach to Software Supply Chain Security
Explore software supply chain security through a risk-based approach, focusing on open source vulnerabilities and process improvements to mitigate supplier risks.
Rules of Engagement for Forking a Dependency
Explore guidelines for forking dependencies when facing security vulnerabilities, balancing community responsibility with timely fixes.
Policy-Driven Supply Chain Security with Enterprise Contract
Explore Enterprise Contract for enforcing software supply chain security and compliance. Learn to verify container images, signatures, and attestations using customizable policies.
SBOMs: Zero to Hero - A Comprehensive Guide
Discover SBOMs: definition, importance, contents, creation methods, and open-source tools. Explore integration challenges and solutions in build processes.

Can LLMs Keep a Secret? Testing Privacy Implications of Language Models
Explore privacy risks of interactive LLMs, examining evaluation frameworks and proposing research directions for improved privacy auditing and mitigation strategies.
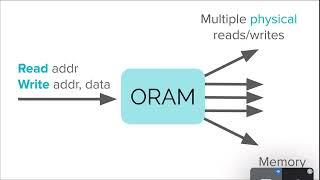
Oblivious RAM: From Theory to Large-scale Real-world Deployment
Explore Oblivious RAM's evolution from theory to real-world deployment. Learn about its applications in blockchain and cloud services, including Signal's implementation and the Oblivious STL library initiative.
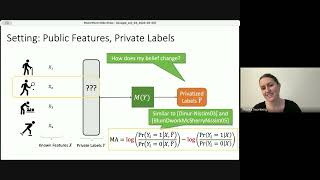
A Unified Analysis of Label Inference Attacks
Explore privacy implications of attribution reporting methods through label inference measures. Gain insights into adversary modeling and risk-accuracy tradeoffs in data privacy.
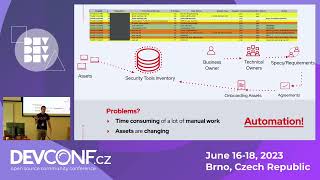
Development of Asset Mapping External Attack Tool
Explore an in-house tool for unified asset visibility, vulnerability mapping, and attack surface analysis in complex multi-cloud environments, tailored for Red Hat standards.
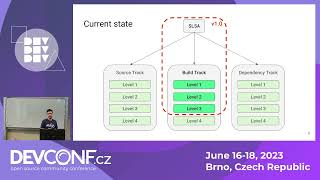
SLSA - A Supply Chain Security Framework
Explore SLSA framework for securing software supply chains, mitigating vulnerabilities, and ensuring code integrity from development to deployment.
Machine Unlearning and Privacy Implications - Differential Privacy for ML
Explore privacy implications of machine unlearning, including threat models, deletion inference, and experimental results in this Google TechTalk on differential privacy for ML.
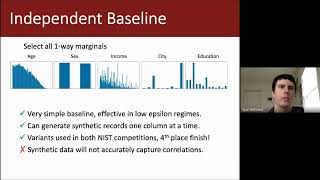
Marginal-based Methods for Differentially Private Synthetic Data - Differential Privacy for ML Series
Explore marginal-based methods for generating differentially private synthetic data, covering mechanisms, selection algorithms, and empirical findings.