Lean Security for Small or Medium-Sized Businesses
Introduces a framework for SMBs to focus security efforts, discussing prevention, limitation, detection, and response capabilities. Provides cost-effective techniques to transform security into a business enabler.
The Future of Incident Response - Network Security Challenges
Bruce Schneier explores the future of incident response in cybersecurity, emphasizing the need for human-centric approaches and systems theory to effectively combat inevitable network attacks.
Security Onion 2.1 - Import Node and so-import-pcap Tutorial
Explore Security Onion 2.1's new Import Node feature and so-import-pcap tool for easy setup and PCAP analysis. Learn how to get started with minimal hardware requirements.

Pcaps Ahoy! Commodity Malware Infections on Windows Hosts - Security Onion Conference 2018
Explore commodity malware infections on Windows hosts through packet capture analysis, enhancing your network security skills and threat detection capabilities.

Save Time with Modern Filtering Techniques - Stop Searching Like It's 1999
Explore modern filtering techniques to enhance security analysis efficiency, moving beyond outdated search methods for faster threat detection and response.

Security Onion - Orchestrating into SO-OODA
Explore orchestration techniques for enhancing Security Onion's capabilities, focusing on the SO-OODA framework to improve threat detection and response in network security environments.

Building Your Security Operations Use Case
Learn to develop effective security operations use cases for enhanced threat detection and response in this insightful talk by industry expert Don Murdoch.
My Use of Security Onion as a Security Researcher
Explore how a security researcher leverages Security Onion for threat detection, network analysis, and malware traffic investigation in this insightful presentation.
Detecting Suspicious Activity on Linux Endpoints Using Security Onion
Learn to identify and analyze suspicious activities on Linux systems using Security Onion's powerful tools and techniques for enhanced endpoint security.

Increasing Your Situational Awareness with SOC Dashboards
Enhance security operations with SOC dashboards for improved situational awareness. Learn effective techniques to monitor and respond to threats in real-time.

Tuning ICS Security Alerts - An Alarm Management Approach
Explore effective strategies for optimizing industrial control system security alerts using alarm management techniques to enhance threat detection and response.
Are We Forever Doomed to Software Supply Chain Security?
Explore software supply chain security challenges, recent incidents, and strategies for mitigating vulnerabilities in open-source ecosystems. Learn about maintainer account security and registry management.
Use AI to Turn Data Into Actionable Information With PagerDuty and AWS
Discover how PagerDuty and AWS leverage AI to transform data into actionable insights, streamline incident response, reduce noise, and improve triage efficiency in real-time.
How to Rob a Bank - Modern Hacking Techniques and Security Defenses
Practical demonstration of modern hacking techniques and defense strategies through a simulated bank robbery, offering insights into targeted attacks and organizational preparedness.
How I've Broken Every Threat Intel Platform and Settled on MISP
Exploring challenges in threat intelligence platforms and advocating for event-based approaches. Discusses experiences with various systems and settling on MISP for effective correlation and analysis of cyber threats.
Randori - A Low Interaction Honeypot with a Vengeance
Explore Randori, an open-source honeypot built behind existing services. Learn about its conception, results, and a new model for addressing global botnet infections as cyber disease control.
MISP New Features and Development Evolution - 2016 Summit
Explore MISP's latest features and development progress in this presentation by Andras Iklody from CIRCL, highlighting advancements in threat intelligence sharing and analysis.
How to Fail Your Cyber Threat Intelligence Usage
Learn strategies to avoid common pitfalls in Cyber Threat Intelligence (CTI) implementation and maximize its effectiveness for your organization's security posture.
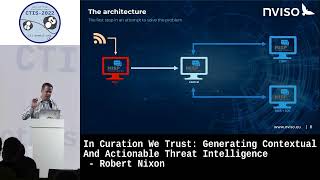
In Curation We Trust - Generating Contextual and Actionable Threat Intelligence
Explore techniques for generating actionable threat intelligence through effective curation, enhancing cybersecurity strategies and decision-making processes.
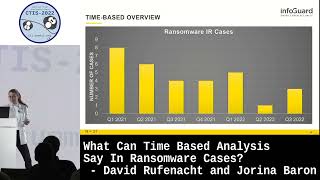
What Can Time-Based Analysis Reveal in Ransomware Cases?
Explore time-based analysis techniques for investigating ransomware incidents, uncovering crucial insights to enhance cybersecurity strategies and incident response.
Beyond Windows Forensics With Built-in Microsoft Tooling
Explore advanced Windows forensics techniques using native Microsoft tools for enhanced digital investigation and threat detection capabilities.