Attacking and Defending Full Disk Encryption
Explore full disk encryption vulnerabilities, attack methods, and defense strategies. Learn practical techniques for securing encrypted systems and balancing usability with security.
Full System Emulation - Achieving Successful Automated Dynamic Analysis of Evasive Malware
Explore full system emulation for dynamic malware analysis, addressing evasion techniques and solutions. Learn to design effective sandboxes and extract valuable intelligence from malicious files.
Investigating PowerShell Attacks
Explore techniques used by attackers to exploit PowerShell for command-and-control, lateral movement, and persistence. Learn to collect and interpret forensic evidence from real-world incidents.
Control-Alt-Hack - White Hat Hacking for Fun & Profit
Explore ethical hacking through a card game that simulates security audits and consulting. Learn about diverse hacking skills, mission challenges, and cybersecurity concepts in an engaging, entertaining format.
Flowers for Automated Malware Analysis
Explore advanced malware obfuscation techniques that bind execution to specific host environments, making automated analysis ineffective. Learn about the arms race between malware authors and security practitioners.
Intrusion Auditing Under Windows NT
Forensic techniques for auditing Windows NT systems post-intrusion, focusing on preserving evidence and using specialized tools to detect and analyze unauthorized access and system modifications.
Building a Forensic Toolkit That Will Protect You From Evil Influences
Explore techniques for secure forensic analysis of compromised systems, focusing on creating a protected environment and essential utilities for Solaris and Windows NT investigations.

The Art of Defiling - Defeating Forensic Analysis
Explore advanced techniques for evading forensic analysis and protecting digital privacy in this comprehensive cybersecurity presentation by The Grugq.
Cisco Router Forensics
Explore Cisco router forensics techniques, uncovering network vulnerabilities and enhancing security measures for robust infrastructure protection.
Forensics With Linux 101
Learn essential Linux forensics techniques for digital investigations, covering evidence collection, analysis tools, and best practices for uncovering digital artifacts.
NT - 2K Incident Response & Mining for Hidden Data - PostMortem of Windows Box
Explore advanced techniques for Windows incident response and data mining, uncovering hidden information in NT/2K systems for effective forensic analysis.
NT - 2K Incident Response & Mining Hidden Data - PostMortem of Windows Box pt2
Explore advanced techniques for Windows incident response and data mining, focusing on hidden information extraction and post-mortem analysis of compromised systems.
Weaponizing Plain Text - ANSI Escape Sequences as a Forensic Nightmare
Explore how ANSI escape sequences can be exploited to inject, vandalize, and weaponize logfiles, combining old terminal injection techniques with modern features to create chaos in cloud CLIs and DevOps environments.
Lurking in the Shadows
Explore shadow copies for malware analysis and recovery with Tim Tomes and Mark Baggett. Learn techniques for Linux and Windows, including manual demos and VSS commands.
Windows Command Line Forensics
Explore Windows command line tools for digital forensics, enhancing investigative skills and uncovering hidden system information without specialized software.

Matriux Leandros - An Open Source Penetration Testing and Forensic Distribution
Explore Matriux Leandros, an open-source distribution for penetration testing and digital forensics, showcasing its features and applications in cybersecurity.
Competitive Hacking - Why You Should Capture the Flag
Explore competitive hacking through Capture The Flag challenges. Learn various styles, techniques, and benefits of CTF competitions while gaining insights from real-world experiences.
Give Me Your Data
Explore data loss prevention strategies and forensic techniques with cybersecurity expert Dave Chronister, covering various digital platforms and storage mediums.
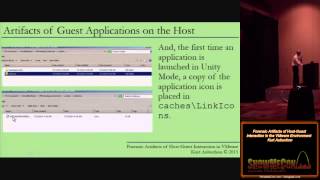
Forensic Artifacts of Host Guest Interaction in the VMware Environment
Explore forensic artifacts resulting from host-guest interactions in VMware, uncovering crucial evidence for digital investigations and virtualization security.
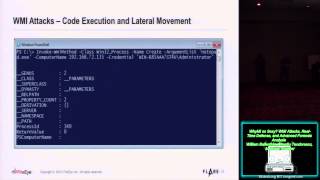
WhyMI so Sexy - WMI Attacks, Real Time Defense and Advanced Forensic Analysis
Explore WMI attacks, real-time defense strategies, and advanced forensic analysis techniques. Learn about PowerShell, event querying, and reverse engineering for enhanced cybersecurity skills.
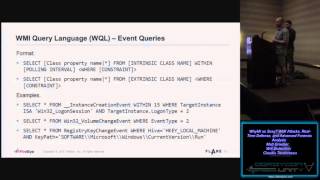
WhyMI so Sexy - WMI Attacks, Real Time Defense, and Advanced Forensic Analysis
Explore WMI attacks, real-time defense strategies, and advanced forensic analysis techniques for cybersecurity professionals seeking to enhance their skills and protect systems.