Zivile Forensik gegen staatliche Überwachung von Journalisten
Überblick zur digitalen Sicherheit im Journalismus weltweit und Einblicke in die Arbeit des Digital Security Labs von Reporter ohne Grenzen zur Unterstützung betroffener Journalist*innen.
The Five Most Dangerous New Attack Techniques and How to Counter Them
Experts discuss the latest dangerous cyber attack techniques, their mechanisms, countermeasures, and future threats, providing insights for cybersecurity professionals to stay ahead of evolving risks.
Developing a Converged IT/OT Threat Model Using MITRE ATT&CK
Develop a converged IT/OT threat model using MITRE ATT&CK framework to map and prioritize defensive capabilities for unified cyber defense strategy across industrial control systems.
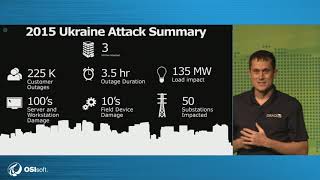
Utilizing Operations Data for Enhanced Cyber Threat Detection
Enhancing industrial control system security by integrating operational data with threat detection platforms for improved situational awareness, faster threat elimination, and better incident response.
Collection Management Framework for ICS Security Operations and Incident Response
Extend asset inventory value with a Collection Management Framework for ICS security operations and incident response. Learn to gather requirements, plan, and implement use cases for efficient threat monitoring and response.
Rise of the Drones - Modern Drone Forensic Opportunities
Explore drone forensics, data extraction techniques, and real-world case studies. Learn how drones impact investigations and uncover insights from "Operation White Lightning" in this comprehensive presentation.
Capture the Flag 101 Workshop
Dive into Capture the Flag challenges with hands-on practice, learning key concepts and problem-solving techniques for beginner and intermediate levels in cybersecurity.
From Small Village to Stock Trading Success: A Young Entrepreneur's Journey
Inspiring journey of a young entrepreneur from rural India to founding a major stock trading platform, showcasing resilience and diverse pursuits as keys to success.
Responding to Threats in AWS Linux and Kubernetes Environments
Explore real-life attack techniques in AWS Linux and Kubernetes environments and learn efficient cloud incident response strategies through automation and enhanced visibility.
Kubernetes Audit Log Best Practices
Discover best practices for Kubernetes audit logging to enhance security and compliance in cloud-native environments.
Introduction to Security and Network Forensics - Encryption Methods
Explore encryption methods, codes, and key-based systems. Learn about cracking techniques, public/private key encryption, hashing, and PGP in this comprehensive security overview.
Exploring Runtime Security and Forensics Using eBPF
Discover how eBPF enhances runtime security and forensic analysis, offering advanced threat detection and system monitoring capabilities for improved cybersecurity.
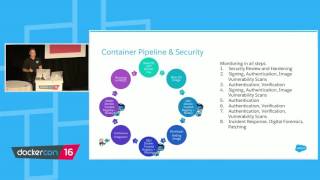
Securing the Container Pipeline at Salesforce - Docker Use Case
Securing Docker containers at Salesforce: infrastructure, pipeline security, monitoring, forensics, and automation for rapid containerization while maintaining data sensitivity and customer trust.
CTF or WTF?
Compara desafíos CTF con pruebas de penetración reales, explorando similitudes y diferencias en habilidades, escenarios y lecciones aprendidas para profesionales de ciberseguridad.
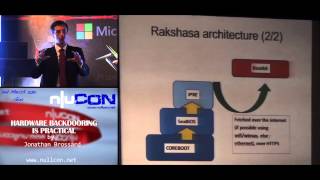
Hardware Backdooring is Possible
Demonstration of permanent hardware backdooring using Rakshasa malware, exploring BIOS vulnerabilities and implications for computer security and forensics practices.
Making Android's Bootable Recovery Work For You
Explore Android's bootable recovery mode to create custom tools for security testing, forensics, and device modification. Learn to build and customize recovery images for various Android devices.
Ingeniería Inversa
Exploración de ingeniería inversa en MAME: análisis forense, hardware y emulación de plataformas. Perspectivas de un desarrollador veterano sobre preservación digital y arqueología tecnológica.
I Know What Your Microsoft Mainframe Did Last Summer
Explore Active Directory forensics, lateral movement, and reconnaissance techniques. Learn to hunt for clues without AD logs using open-source tools in this hands-on session with real-world incident insights.
Using Hadoop for Malware, Network, Forensics and Log Analysis
Explore big data analysis for cybersecurity using Hadoop, tackling malware, network traffic, and log files at scale to overcome processing limitations and enhance threat detection.
Social Forensication: A Multidisciplinary Approach to Successful Social Engineering - J.Gray - Hack in Paris - 2019
Explore innovative social engineering techniques, including memory image analysis and rogue Wi-Fi attacks, along with defensive strategies and ethical considerations for cybersecurity professionals.
Debate- Hackers, the Media, Truth, Trust & Alternative Facts - Hack in Paris - 2017
Debate on hackers, media, truth, and trust. Explores fact-checking, vulnerability disclosure, fake news, and regaining trust in the digital age. Features expert panel discussion and audience participation.