Detecting White-Collar Cybercrime - SAP Forensics
Explore SAP Forensics techniques for detecting and investigating white-collar cybercrime in enterprise systems, enhancing your ability to secure critical business data and processes.
Digital Forensics and Incident Response in G Suite
Learn digital forensics and incident response techniques for G Suite environments, focusing on effective investigation and mitigation strategies for cloud-based security incidents.
What Happened to Your Home - IoT Hacking and Forensic with 0-Days
Explore IoT device vulnerabilities, hacking techniques, and forensic analysis in smart homes. Learn about zero-day exploits and their impact on home security.
Beyond Windows Forensics with Built-in Microsoft Tooling
Explore advanced Windows forensics techniques using native Microsoft tools, enhancing your ability to investigate and analyze digital evidence effectively.
Ingeniería Inversa
Exploración de ingeniería inversa en MAME: análisis forense, hardware y emulación de plataformas. Perspectivas de un desarrollador veterano sobre preservación digital y arqueología tecnológica.
I Know What Your Microsoft Mainframe Did Last Summer
Explore Active Directory forensics, lateral movement, and reconnaissance techniques. Learn to hunt for clues without AD logs using open-source tools in this hands-on session with real-world incident insights.
Möglichkeiten der Enttarnung steganographischer Kommunikation im Medium natürlicher Sprachen
Diskussion über Methoden zur Erkennung versteckter Botschaften in natürlicher Sprache, einschließlich Merkmale, Enttarnungsansätze und Gegenmaßnahmen für klandestine Kommunikation.
Leveraging Osquery for DFIR at Scale
Explore efficient incident response using Osquery for digital forensics, accelerating breach investigations and uncovering attacker breadcrumbs in large-scale environments.
Using Hadoop for Malware, Network, Forensics and Log Analysis
Explore big data analysis for cybersecurity using Hadoop, tackling malware, network traffic, and log files at scale to overcome processing limitations and enhance threat detection.
The Metabrik Platform - Rapid Development of Reusable Security Tools
Explore the Metabrik Platform for rapid security tool development. Learn to create reusable components, improve existing tools, and solve complex security challenges efficiently.
Flash Storage Forensics
Explore flash storage forensics techniques, including spare area analysis, wear leveling, and flash translation layers, to enhance criminal investigation capabilities.
Abusing Bash for Windows
Explore techniques for exploiting Bash on Windows, including remote shells, password extraction, and AppLocker bypasses. Learn about security implications and forensic considerations.
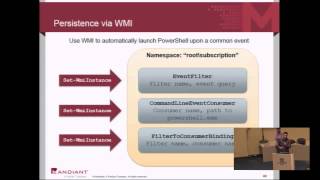
Investigating PowerShell Attacks
Explore PowerShell attack techniques, forensic artifacts, and investigation methods for detecting and mitigating threats in Windows environments.
Social Forensication: A Multidisciplinary Approach to Successful Social Engineering - J.Gray - Hack in Paris - 2019
Explore innovative social engineering techniques, including memory image analysis and rogue Wi-Fi attacks, along with defensive strategies and ethical considerations for cybersecurity professionals.
Debate- Hackers, the Media, Truth, Trust & Alternative Facts - Hack in Paris - 2017
Debate on hackers, media, truth, and trust. Explores fact-checking, vulnerability disclosure, fake news, and regaining trust in the digital age. Features expert panel discussion and audience participation.

The Advanced Threats Evolution- REsearchers Arm Race - Alex Matrosov - Ekoparty Security Conference - 2019
Explore the evolution of advanced threats and defensive software, focusing on persistent methods at hardware and firmware levels. Gain insights into modern security gaps and potential solutions.
Hacked! Run Time Security for Containers
Explore container security challenges, runtime monitoring, policy enforcement, and forensics using system call signals. Learn to detect threats and implement robust security measures for containerized environments.
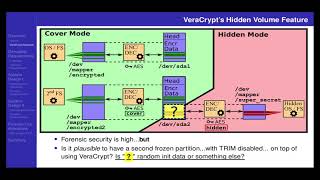
Perfectly Deniable Steganographic Disk Encryption
Explore self-concealing, deniable encryption techniques similar to VeraCrypt's hidden volume feature, covering design, implementation, and forensic analysis considerations.
HackIM CTF - Do's and Don'ts
Explore CTF competitions: learn security through challenges in web, crypto, reverse engineering, and more. Gain insights on dos and don'ts for successful participation in HackIM CTF.
Hacking Exposed - Hacking Macs
Explore advanced MacOS intrusion techniques, TTPs, and countermeasures through real-world case studies. Learn about process visualization, forensics, and effective detection and response strategies.
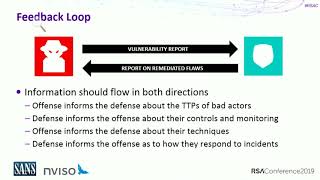
Live Adversary Simulation - Red and Blue Team Tactics
Explore live adversary simulation techniques, enhancing communication between red and blue teams for effective cybersecurity. Learn to perform threat simulations, map APT phases, and implement purple teaming strategies.