Leveraging FPGA-Based Root of Trust for Efficient, Dynamic, and Remote Platform Attestation
Discover how FPGA-based Root of Trust enables secure platform attestation, providing dynamic cryptographic proof of identity and firmware integrity in modern computing systems.
OpenTitan: Open-Source Hardware Root of Trust - Project Update
Discover the latest developments in OpenTitan's open-source hardware root of trust, including its architecture, security features, and applications for firmware protection and secret storage.
Mutual Authentication Vulnerabilities in Physical Access Control Systems
Explore physical access control system vulnerabilities, authentication weaknesses, and practical exploit techniques, featuring live demonstrations with HID readers and security tools.
Compromising Electronic Loggers and Creating Truck-to-Truck Worm - Security Vulnerabilities in ELD Systems
Discover critical security vulnerabilities in Electronic Logging Devices (ELDs) and their implications for truck network security, from reverse engineering to proof-of-concept attacks and industry-wide security reforms.
Trusted Firmware - Building Secure Firmware Collaboratively
Explore collaborative firmware security with Trusted Firmware. Learn about vulnerabilities, applications, and architecture for building robust, secure systems across various platforms.
Breaking Firmware Trust From Pre-EFI - Exploiting Early Boot Phases
Explore recent UEFI firmware security changes, focusing on Intel CPUs. Covers firmware mitigations in SMM/DXE and new attacks on Intel PPAM, offering unique insights from an offensive security perspective.
Device Security in the OCP Supply Chain - Overview of How OCP SAFE Addresses Device Firmware Challenges
Explore how OCP S.A.F.E. framework tackles device firmware security challenges and strengthens supply chain integrity through expert insights and practical solutions.
Exposing Critical Threats in Cellular Modem Security - Telit Vulnerabilities Analysis
Uncover critical security vulnerabilities in Telit cellular modems, including remote code execution flaws, SMS-based attacks, and MIDlet compromise methods that affect millions of connected devices.
Protecting Yourself From Supply Chain Attacks - Trust Is Overrated
Discover practical strategies and tools for validating hardware and software integrity, minimizing supply chain risks, and implementing effective security measures across your technology stack.
Contactless Overflow Code Execution Vulnerabilities in Payment Terminals and ATMs
Uncover critical NFC payment terminal vulnerabilities and their exploitation through contactless attacks, including ATM jackpotting techniques and firmware manipulation across major payment systems worldwide.
Breaking BMC: The Forgotten Key to the Kingdom - Security Vulnerabilities in Baseboard Management Controllers
Dive into the security vulnerabilities of Baseboard Management Controllers (BMC), exploring exploit chains and firmware implants in NVIDIA hardware with AMI MegaRAC BMC implementation.
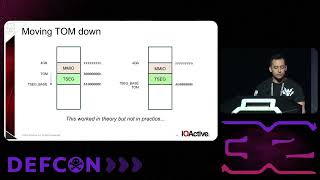
AMD Sinkclose - Universal Ring2 Privilege Escalation in System Management Mode
Delve into AMD processor security vulnerabilities, exploring System Management Mode (SMM), CPU design flaws, and the methodology behind ring-2 privilege escalation exploits.
Breaking the Beam - Exploiting VSAT Modems from Earth
Discover groundbreaking security vulnerabilities in VSAT satellite modems through reverse engineering, exploring software stack exploits and demonstrating wireless signal injection attacks for remote access.
A Dark Side of UEFI: Cross-Silicon Exploitation
Explore cross-silicon exploitation in UEFI, uncovering vulnerabilities and advanced attack techniques. Gain insights into Arm perspective, Windows Development Kit, and TrustZone weaknesses.
Engineering a Backdoored Bitcoin Hardware Wallet - Security Analysis and Implementation
Explore how attackers can secretly extract private seeds from Bitcoin hardware wallets through ECDSA signatures, demonstrating vulnerabilities in wallet security and firmware updates.
Making the Edge Tamper-Proof: Security Challenges and Solutions in Edge Computing
Discover essential security practices for edge computing deployments, focusing on firmware protection, supply chain security, and tamper-proofing strategies using EVE-OS in remote environments.
From Boot to Root: Identifying and Mitigating Security Issues in Bootloaders
Dive into bootloader security vulnerabilities and learn effective mitigation strategies for protecting systems during the critical boot process.

D-LINK NAS Security Bug Analysis and Firmware Vulnerability
Dive into a critical analysis of D-LINK NAS's unpatched firmware vulnerability, exploring security implications and understanding the technical oversight in network storage systems.
3D Printer Firmware Attacks on Fused Filament Fabrication - A Systematic Analysis
Explore firmware attack vulnerabilities in 3D printing systems, examining classification methods, attack vectors, and security implications for fused filament fabrication processes.
A Comprehensive Study on the Security of Arm Cortex-M Systems
Delve into a systematic analysis of Arm Cortex-M systems' security features, examining hardware limitations, software vulnerabilities, and protection mechanisms across 1,797 real-world firmware implementations.

Black Hat Europe 2024
Black Hat Europe 2024