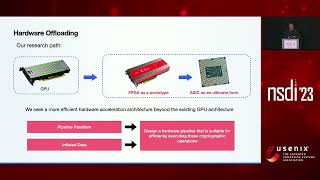
FLASH - Towards a High-performance Hardware Acceleration Architecture for Cross-silo Federated Learning
Innovative hardware acceleration architecture for cross-silo federated learning, enhancing performance and resource utilization of cryptographic operations while preserving data privacy.
RoFL - Robustness of Secure Federated Learning
Explore secure federated learning's robustness with RoFL, examining challenges and solutions for resilient distributed machine learning systems in privacy-sensitive environments.
ELSA - Secure Aggregation for Federated Learning with Malicious Actors
Explore ELSA, a secure aggregation protocol for federated learning that protects against malicious actors while maintaining efficiency and scalability in distributed machine learning environments.
Gradient Obfuscation Gives a False Sense of Security in Federated Learning
Explores vulnerabilities in federated learning, demonstrating how gradient obfuscation techniques may not provide adequate privacy protection. Proposes a new attack framework and challenges existing evaluation methods.
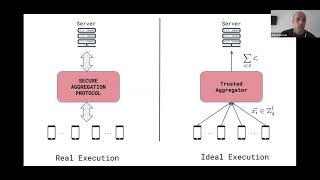
Privacy in Federated Learning at Scale
Explore privacy challenges and solutions in large-scale federated learning systems with experts Gascon, Kairouz, and Bonawitz, discussing cutting-edge techniques for secure collaborative machine learning.
Deep Learning for Mobile Devices
Strategies for implementing efficient convolutional neural networks on mobile devices, covering model optimization, hardware considerations, and on-device training techniques.
Practical Privacy-Preserving Machine Learning in Python
Explore privacy-preserving machine learning techniques in Python, including federated learning and encrypted data algorithms, to build accurate models while protecting user privacy.
Accelerating Drug Discovery by Competitive Cooperation Through Open Source
Explore how Kubernetes enables collaborative machine learning in drug discovery, balancing data privacy and competitive interests among pharmaceutical companies.
Accelerate Federated Learning Model Deployment with KServe - KFServing
探索利用KServe加速联邦学习模型部署的实践。介绍Kubeflow、KFServing和推理服务工作流程,联邦学习基础知识,以及如何从水平训练的联邦学习模型创建服务。
Information Leakage of Neural Networks
Explore information extraction attacks on machine learning models, their potential to compromise sensitive data, and strategies for mitigation. Gain insights into legal aspects and privacy-security-utility tensions.
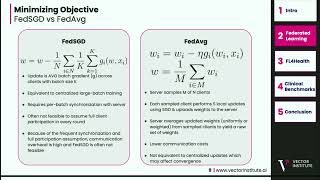
Federated Learning for Healthcare: Private and Personal Clinical Modeling
Explore federated learning's application in healthcare, focusing on training machine learning models across distributed clinical datasets without compromising sensitive data privacy and security.
SUMO Simulations for Privacy-Preserving Federated Learning in Autonomous Vehicles
Explore privacy-preserving federated learning techniques for autonomous vehicles using SUMO simulations, focusing on balancing data protection and predictive model performance.
Scalable and Portable Federated Learning Simulation Engine
Discover a powerful simulation engine for federated learning that enables privacy-focused data analysis, offering scalable and hardware-independent implementation for research and production environments.
Privacy and Security in Vehicular Data Aggregation Using Federated Learning - A Parking Occupancy Case Study
Explore privacy challenges in vehicular federated learning systems, focusing on data protection, route inference attacks, and security implications for intelligent city traffic prediction.
HasTEE: Programming Trusted Execution Environments with Haskell
Explore HasTEE, a Haskell-embedded DSL for programming Trusted Execution Environments. Learn how it simplifies TEE application development with automatic partitioning and enhanced security features.
Advancing Private Federated Learning - Insights and Innovations from Research
Explore private federated learning techniques, challenges, and real-world applications. Gain insights into Apple's implementation and learn how to start research using open-source tools.
OpenFL - A Federated Learning Project to Power and Secure Your Projects
Discover OpenFL: Secure federated learning framework for collaborative model training without sharing sensitive data. Adopt, contribute, and enhance AI projects with privacy-preserving techniques.
Federated Learning in Production: Enabling AI Training with Data Privacy
Explore federated learning's applications, benefits, and implementation requirements for AI training on edge devices with data privacy.
Federated Learning in Production: Enabling AI Training with Data Privacy
Explore federated learning's applications, benefits, and implementation requirements for AI training on edge devices with data privacy.
Flower - An Opensource Federated Learning Framework
Explore Flower, an open-source federated learning framework, and its applications in collaborative machine learning across distributed datasets.
Learning and Unlearning Your Data in Federated Settings
Explore federated learning and unlearning approaches for collaborative AI model training while preserving data privacy. Analyze methods for removing data inputs in distributed settings to comply with regulations.