Generalization and Personalization in Federated Learning - Karan Singhal
Explore generalization and personalization in federated learning, focusing on medical AI applications. Insights on improving model performance across diverse data distributions and healthcare settings.
Federated Learning - Machine Learning on Decentralized Data
Explore federated learning for privacy-preserving machine learning on decentralized data. Learn about its implementation in Google products and simulation using TensorFlow Federated.
Federated Learning with Azure Machine Learning
Explore federated learning with Azure ML, enabling collaborative training across organizations while protecting data privacy. Includes a demo of global FL setup using NVIDIA FLare.
Preserving Data Privacy in Federated Learning - Xiaokui Xiao
Explore privacy-preserving techniques in federated learning, including differential privacy, model privacy, and vertical factory learning, with insights on future developments and challenges.
Rethinking Architecture Design for Data Heterogeneity in FL - Liangqiong Qu
Explores innovative architecture designs for federated learning in medical AI, focusing on Transformers to address data heterogeneity challenges and improve model performance across diverse healthcare institutions.
Beyond Testset Performance - Strategies for Clinical Deployment
Strategies for deploying AI in clinical settings, addressing challenges beyond test performance. Explores model reliability, distribution shifts, and human-AI collaboration for real-world medical applications.

Federated Hyperparameter Tuning - Challenges, Baselines, and Connections
Explores challenges and solutions for hyperparameter tuning in federated learning, introducing FedEx method to accelerate the process. Connects to weight-sharing in neural architecture search and demonstrates improved accuracy on benchmarks.
Federated Learning in Medicine - Breaking Down Silos to Advance Medical Research
Explore federated learning's potential to revolutionize medical research by breaking data silos, enhancing privacy, and fostering collaboration across healthcare institutions.

Stanford Seminar - The Future of Edge Computing from an International Perspective
Explore international perspectives on edge computing, covering 5G integration, federated learning, AI processing, and IoT systems for smart applications across Asia and the U.S.
The Privacy Considerations of Production Machine Learning
Explore state-of-the-art research on privacy in machine learning, including estimating and defending against privacy leakage, secure collaboration, and machine unlearning for GDPR compliance.
Building a Cloud-Native Privacy Computing Platform in Financial Industry
探索上海浦东发展银行如何构建云原生隐私计算平台"波塞冬",实现数据安全与算法性能的平衡,并在多个业务场景中发挥关键作用。
Pediatric Moonshot - Global, Real-Time, Privacy-Preserving Applications for Children's Medicine
Exploring innovative AI applications in pediatric medicine using privacy-preserving, decentralized edge cloud technology to improve global healthcare equity and enable real-time diagnosis and treatment.
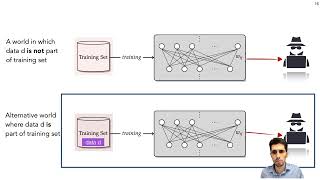
Auditing Data Privacy for Machine Learning
Explores privacy risks in machine learning, including data extraction from models, membership inference attacks, and tools for auditing privacy. Discusses implications for AI regulations and privacy-by-design approaches.
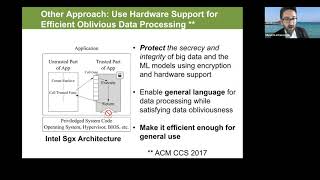
Securing Big Data in the Age of Artificial Intelligence
Explore challenges and solutions for securing big data in AI, including hardware support, federated learning, and privacy-preserving techniques for data science and machine learning.
Privacy-Preserving AI - Andrew Trask, University of Oxford
Explore privacy-preserving AI techniques with Andrew Trask, covering differential privacy, federated learning, and shared governance for ethical and secure AI development.
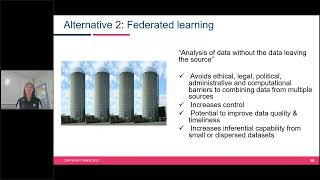
Making Private Data Open and Enhancing Decision-Making Through Digital Atlases
Explore innovative approaches to data sharing, privacy preservation, and decision-making enhancement through digital atlases, focusing on the Australian Cancer Atlas and Bayesian statistical models.
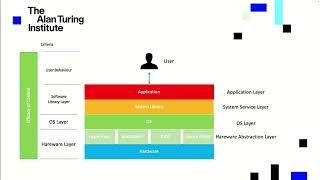
A Novel Federated Learning Method to Model Cybersecurity Risk Estimation for Digital Identity Management Systems
Explore a novel federated learning approach for estimating cybersecurity risks in digital identity management, presented by Po-Chu Chen from the University of Warwick.
Survey on Privacy and Security in Federated Learning
Explore privacy and security challenges in Federated Learning with Google experts Peter Kairouz and Kunal Talwar, discussing key issues and potential solutions.
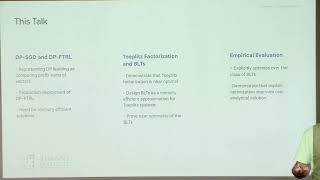
Large Scale Private Learning on Data Streams and the Buffered Linear Toeplitz Operators
Innovative algorithm for privacy-preserving machine learning on data streams, introducing Buffered Linear Toeplitz operators for efficient noise generation in differentially private training.
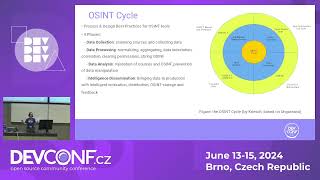
Open Source Intelligence Data in Cyber Threat Intelligence for a Common Purpose - DevConf.CZ 2024
Explore OSINT's role in Cyber Threat Intelligence for Enterprise IoT protection. Learn about Federated Learning, global data exchange, and AI-driven threat detection for enhanced cybersecurity.
Protecting Sensitive Data and Machine Learning Models
Discover techniques for safeguarding sensitive data and ML models, enhancing privacy and security in Python-based AI applications.