Federated and Collaborative Learning - Session 2
Explore cutting-edge research in federated learning, collaborative AI, and privacy-preserving data analysis with expert talks on fast mean estimation and stable covariance techniques.
From Idea to Impact, the Crypto Story - What's Next?
Explore the intersection of cryptography and machine learning, examining challenges, impacts, and future directions in digital privacy, adversarial learning, and quantum resilience.
Back to the Drawing Board - A Critical Evaluation of Poisoning Attacks on Federated Learning
Critical evaluation of poisoning attacks on federated learning, examining threat models, attack types, and robustness across different FL settings. Insights for researchers and practitioners in secure machine learning.
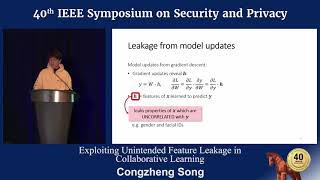
Exploiting Unintended Feature Leakage in Collaborative Learning - Congzheng Song
Explores security vulnerabilities in collaborative machine learning, demonstrating how model updates can leak sensitive information about training data and proposing inference attacks to exploit these weaknesses.
Federated and Collaborative Learning - Session 3
Explore cutting-edge advancements in federated and collaborative learning, including local training methods, online learning with bandit feedback, and insights from leading researchers in the field.
Survey on Optimization in Federated Learning
Explore optimization techniques in Federated Learning, focusing on collaborative approaches and their applications in distributed machine learning environments.
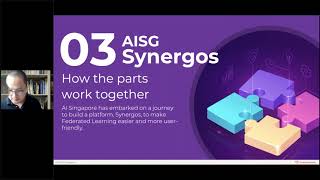
AI Singapore's Journey into the World of Federated Learning
Explore AI Singapore's Synergos system for federated learning, a privacy-preserving technique that trains models across decentralized parties without exchanging data, addressing privacy concerns and regulatory compliance.
Berkeley in the 80s - Silvio Micali Interview on Theoretical Computer Science
Turing Laureate Silvio Micali discusses his groundbreaking research at Berkeley, covering pseudorandomness, multiparty computation, and blockchain technology, while reflecting on the university's influential atmosphere in the 1980s.
Federated Heavy Hitters Discovery with Differential Privacy
Explore federated learning, differential privacy, and heavy hitters discovery in this talk by Peter Kairouz. Learn about multiparty computation, open research, and practical applications in data analysis.
How to Allow Deep Learning on Your Data Without Revealing Your Data
Exploring secure deep learning on private data without revealing it, discussing InstaHide and TextHide methods, their applications in Federated Learning, and addressing potential security concerns.
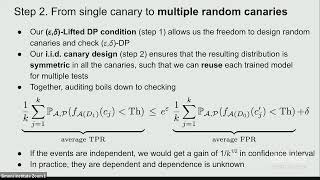
Fundamental Trade-Offs in FL-FA - Sparsity - DP - Communication Constraints
Explore trade-offs in federated learning, focusing on sparsity, differential privacy, and communication constraints. Gain insights into balancing these factors for effective machine learning.
Enabling On-Device Learning at Scale
Explore on-device learning techniques for AI personalization, including few-shot learning, continuous learning, and federated learning, addressing privacy and efficiency challenges in edge computing.
Airborne Sound Maintenance in Remote Sites Using Low Power Federated Learning
Explore low-power federated learning for remote site maintenance using airborne sound, minimizing downtime and costs while adhering to GDPR regulations.
Modern Medical Image Segmentation, AutoML, and Beyond
Explore advanced medical image segmentation techniques, including AutoML and deep learning, for improved disease understanding and clinical diagnosis.
Federated Learning All-in-One Box
Explore federated learning architecture, deployment workflows, and practical demonstrations using Microshift for decentralized machine learning applications.
Federated Learning - Unlocking the Value of Discrete Data for Enterprise
Explore federated learning's potential for enterprise collaboration, data privacy, and value extraction. Learn about FATE and OpenFL frameworks, and discover FedLCM for multi-cloud orchestration.
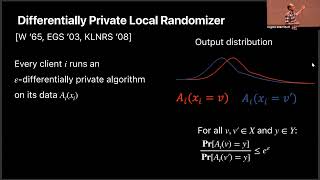
Low-Communication Algorithms for Private Federated Data Analysis - Invited Talk
Low-communication algorithms for private federated data analysis, offering optimal accuracy guarantees while preserving privacy in distributed settings.
Federated Learning with Formal User-Level Differential Privacy Guarantees
Explore federated learning with differential privacy guarantees, covering key concepts, challenges, and algorithms like DP-SGD and DP-FTRL, with insights on privacy-utility trade-offs and future directions.
Decentralized Data Science Made Easy
Explore decentralized data science techniques and applications in this comprehensive talk, focusing on simplifying complex concepts for practical implementation.
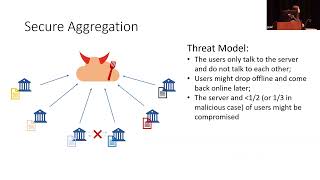
MicroFedML: Privacy Preserving Federated Learning for Small Weights
Privacy-preserving federated learning techniques for small weights, focusing on MicroFedML. Explores innovative approaches to enhance data privacy in machine learning collaborations.
Privacy Preserving AI in Cryptography - Round Table Discussion
Explore privacy-preserving AI techniques in this roundtable discussion from the Glowing Hot Topics in Cryptography workshop, focusing on the intersection of cryptography and artificial intelligence.