Finding and Exploiting Novel Flaws in Java Software
Explore techniques for discovering and exploiting vulnerabilities in Java applications, focusing on novel flaws and advanced security research methodologies.
QARK: Android App Exploit and Static Code Analysis Tool
Explore QARK, a comprehensive tool for Android app security analysis and exploitation. Learn how it combines static code analysis, vulnerability detection, and automatic exploit generation for developers and pentesters.
Exploiting Web Messaging Implementations
Uncover vulnerabilities in cross-document messaging, learn common developer mistakes, and explore open-source tools for identifying post messaging security issues in web applications.
Racing for Hidden Treasures in Public GitHub Repositories - Exploiting Build Artifacts
Explore a novel attack vector in GitHub Actions, uncovering hidden access tokens in build artifacts and racing against time to exploit ephemeral credentials for swift attacks on open-source projects.
Exploiting Bluetooth Vulnerabilities: From Vehicle Systems to Bank Account Access
Discover how to identify and exploit Bluetooth vulnerabilities in modern vehicle systems using BlueToolkit, exploring real-world security implications and practical attack vectors in automotive and aviation contexts.

Stegosploit - Hacking with Pictures
Explore innovative hacking techniques using steganography to hide exploits within images, blending cybersecurity with digital art for covert attacks and data exfiltration.
Spectre Attacks Exploiting Speculative Execution
Explore speculative execution vulnerabilities in modern processors, their impact on system security, and potential countermeasures to protect against Spectre attacks.
The Tragedy of Bluetooth Low Energy - Security Risks and Attacks
Exploring Bluetooth Low Energy vulnerabilities: QR code payment risks, smart device unlocking flaws, and car hacking demonstrations. Introduces a BLE security detection tool for researchers and manufacturers.
How Crypto Can Be Broken By You - Workshop Day 1
Explore practical techniques to break cryptographic systems, enhancing your understanding of vulnerabilities and strengthening cybersecurity skills.
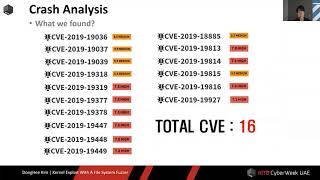
Kernel Exploitation with a File System Fuzzer
Explore kernel exploitation using a filesystem fuzzer, uncovering vulnerabilities and demonstrating R/W primitive attacks and control flow hijacking in Linux systems.
MIPS-X - The Next IoT Frontier
Explore MIPS-based IoT device research with a framework for efficient emulation, vulnerability analysis, and exploit development. Gain insights into CPU architectures, virtualization, and cross-compilation techniques.
ROP with a 2nd Stack, or This Exploit is a Recursive Fibonacci Sequence Generator
Explore advanced ROP techniques using a second stack, delving into recursive Fibonacci sequence generation as an exploit method. Gain insights into innovative cybersecurity approaches.
The Sednit Group, Cyber Espionage in Eastern Europe
Explore the Sednit group's cyber espionage tools, recent campaigns, and exploitation techniques targeting Eastern Europe, with a focus on Ukraine-related topics and custom exploit-kits.
Hacking K-12 School Software in a Time of Remote Learning
Análisis de vulnerabilidades en software educativo durante la pandemia, explorando ataques potenciales y sus implicaciones para la seguridad de dispositivos escolares y domésticos.
Breaking the Glass Sandbox
Discover techniques to find exploitable Linux kernel bugs in sandboxed environments, learn to identify valuable vulnerabilities, and explore methods for both offensive and defensive security.
A Dirty Little History
Unveiling "Branch History Injection": A new attack bypassing hardware defenses against Spectre-v2. Explore reverse engineering, exploit development, and the latest mitigations in CPU security.
Hackable Security Modules - Reversing and Exploiting a FIPS 140-2 Lvl 3 HSM Firmware
Exploring vulnerabilities in Hardware Security Modules (HSMs) through firmware analysis and reverse engineering of the TMS320C64x DSP architecture, with focus on the Utimaco SecurityServer.
A Little Less Conversation, A Little More ActionScript
Techniques for in-depth reverse engineering of Flash, mapping ActionScript to undocumented counterparts, and analyzing vulnerabilities in Adobe Flash Player for improved exploit research.
The Last Generic Win32K KASLR Defeat in Windows
Detailed exploration of Windows kernel security, focusing on KASLR defeats, heap vulnerabilities, and recent changes in RS4. Insights into potential exploits and current Windows KASLR state.
PwdLess - Exploitation Tales from RouterLand
Explore IoT device security through an attacker's perspective, covering fuzzing, reverse engineering, and exploit development. Learn about vulnerabilities, remote execution techniques, and challenges in IoT security.
Expanding Exploitation Beyond X86 and ARM
Comparative study of Xtensa architecture for IoT devices, exploring differences from ARM for security researchers. Covers assembly instructions, security mechanisms, gadget searching, and post-boot persistence techniques.