Exploiting NFC Vulnerabilities in Indian Metro Systems
Exploiting vulnerabilities in Indian metro systems' NFC technology for free travel. Insights into hacking MiFare cards, challenges faced, and potential solutions.
Deep Dive Into DLL Hijacking - Discovery, Automation and Impact
Explore DLL hijacking techniques, including discovery methods, automation processes, and potential impacts in this cybersecurity presentation from DefCamp 2023.
Penetration Testing Interview Questions and Answers - Master Scenario Based Prep
Master scenario-based interview prep for penetration testers. Covers vulnerability assessments, exploit development, and real-world scenarios to boost confidence and skills for landing dream jobs in cybersecurity.
Thread-Level Attack-Surface Reduction for Enhanced Security
Explore thread-level attack-surface reduction, a dynamic approach to eliminate unused code on a thread level, significantly reducing ROP gadgets and enhancing security in multi-threaded applications.
The Hunt for CVE-2023-0286 - Replicating OpenSSL's Latest Vulnerability
Replicate CVE-2023-0286 in OpenSSL, learn to write a libfuzzer harness, and explore vulnerability research techniques for enhanced security awareness and threat prevention.
SLUB Internals for Exploit Developers
Explore SLUB allocator internals and slab memory shaping strategies for Linux kernel exploit development. Gain insights into controlling memory corruption and implementing effective exploit techniques.
Finding and Exploiting Critical Vulnerabilities in RPC Services - NorthSec 2023
Comprehensive walkthrough of finding, exploiting, and reporting critical vulnerabilities in an RPC service, covering reverse engineering, authentication bypass, and coordinated disclosure.
SystemUI as EvilPiP - Hijacking Attacks on Modern Mobile Devices
Reveals new Android attack surface 'PiP', exploiting vulnerabilities to bypass security measures and perform stealthy hijacking attacks on modern devices without permissions or user awareness.
From ASCII to UTF-16: Leveraging Encodings to Break Software
Explore how character encodings can be exploited to compromise software security, from basic ASCII to complex UTF-16, in this technical IT security talk.
CIAPO - Code Injection via Arbitrary Pointer Overwrite
Explore code injection via arbitrary pointer overwrite in this cybersecurity presentation. Learn about vulnerabilities, hacking techniques, and defensive strategies from a Bitdefender security researcher.
Blasting Past WebP - Exploring Image Format Vulnerabilities
Explore advanced techniques for bypassing WebP image format security measures, uncovering vulnerabilities and potential exploits in web applications.
Escaping the Safari Sandbox: A Tour of Webkit IPC
Explore Webkit IPC vulnerabilities and techniques for escaping the Safari sandbox, gaining insights into browser security and exploitation.
Attacking the Samsung Galaxy A Boot Chain
Explore Samsung Galaxy A* boot chain vulnerabilities and attack techniques for enhanced mobile security understanding.
Booting with Caution: Dissecting Secure Boot's Third-Party Attack Surface
Dissect Secure Boot's third-party attack surface, exploring vulnerabilities and potential exploits in boot processes.
Beyond Android MTE: Navigating OEM's Logic Labyrinths
Explore advanced Android security, focusing on Memory Tagging Extension (MTE) and OEM-specific implementations. Gain insights into exploiting vulnerabilities in custom logic.
Open Sesame: Stack Smashing Your Way into Opening Doors
Explore stack smashing techniques to bypass security measures in electronic door locks, uncovering vulnerabilities and potential exploits in physical access control systems.
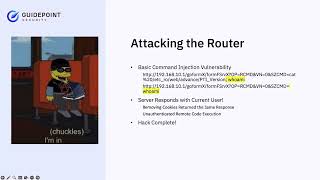
The Route to Success: Hacking a Router to Its End of Life
Explore the process of hacking a Trendnet travel router, from vulnerability hunting to exploit development. Learn methodologies and tools for both newcomers and veterans in IoT security.
Unexpected Intrusion Testing Results in SAP Systems - Critical Vulnerabilities and Exploits
Unveiling critical vulnerabilities in SAP Start Service, from local to remote exploits. Explores memory corruption and OS command injection leading to root-level RCE, with live demo and recommendations.
Privilege Escalation from Medium to High Integrity Level in Windows
Unveiling a Windows design flaw allowing privilege escalation from Medium to High integrity level, demonstrating a 100% reliable exploit on the latest Windows versions.
What's in a Name? Exploring MojoBlob Registry and Service Side Dispatch
Explore MojoBlob Registry's code structure, service-side dispatch, and potential security vulnerabilities in Windows naming conventions.

Timeless Debugging - A New Paradigm for Exploit Development
George Hotz introduces QIRA, an open-source tool for timeless debugging, showcasing its potential to revolutionize exploit development and significantly speed up the debugging process.