Non-Intrusive Vulnerability Localization and Hotpatching for Industrial Control Systems
Explore non-intrusive techniques for identifying and patching vulnerabilities in Industrial Control Systems, focusing on specialized requirements of devices like PLCs.
Uncovering Planned Obsolescence Practices in Robotics and What This Means for Cybersecurity
Explore systematic "robot teardown" to understand and repair robots, uncovering planned obsolescence practices and their implications for cybersecurity in robotics.
Your Software IS - NOT Vulnerable - CSAF, VEX, and the Future of Advisories
Explore the future of software security advisories, focusing on CSAF and VEX, and learn how to manage the increasing volume of vulnerability information effectively.
The NSA Playset - A Year of Toys and Tools
Explore NSA-inspired gadgets for USB, PCI Express, I2C, GSM, Bluetooth, and RF retroreflectors. Learn about tools mimicking intelligence agency capabilities for electronic device eavesdropping and surveillance.
Cloning 3G - 4G SIM Cards With A PC And An Oscilloscope - Lessons Learned In Physical Security
Reveals vulnerabilities in 3G/4G SIM cards, demonstrating how to clone them using differential power analysis. Discusses implications for mobile network security and showcases practical experiments.
Adventures in Femtoland - 350 Yuan for Invaluable Fun
Explore vulnerabilities in 3G/4G networks using femtocells. Learn to intercept data and exploit weaknesses in UMTS infrastructure, from unboxing to proof-of-concept demonstrations.
When IoT Attacks - Hacking a Linux-Powered Rifle
Explore the security vulnerabilities of a Linux-powered precision rifle, including reverse engineering, attack surfaces, and implications of network-connected firearms.
ThunderStrike 2 - Sith Strike
Explore firmware vulnerabilities in Mac systems, demonstrating software-only attacks and showcasing the potential of Mac firmware malware. Learn about shared vulnerabilities and case studies.
Firmware.RE - Firmware Unpacking, Analysis and Vulnerability-Discovery as a Service
Large-scale analysis of firmware images reveals vulnerabilities across embedded systems, highlighting security challenges and the need for improved tools and techniques in firmware analysis.
DTM Components - Shadow Keys to the ICS Kingdom
Explore vulnerabilities in industrial control system components, focusing on DTM technology used in critical industries. Learn about security flaws and their implications for field devices.

Hacking the Wireless World with Software Defined Radio - 2.0
Explore RF spectrum analysis, reverse engineering wireless systems, and hacking techniques using software-defined radio. Learn to decode satellite communications, track aircraft, and monitor ACARS.
Secure Digital Communications for Our Modern Dystopia
Secure communication system for hostile environments, leveraging NASA's Disruption-Tolerant Networking for activists, refugees, and trolls. Embraces high-throughput physical data transfer methods.
Computrace Backdoor Revisited
Exposición de vulnerabilidades en software antirrobo Computrace, demostrando fallos de seguridad y posibles ataques. Incluye análisis del protocolo, comportamiento sospechoso y métodos de detección/desactivación.
Why Control System Cyber-Security Sucks
Explores challenges in industrial control system cybersecurity, critiquing current approaches and advocating for a paradigm shift towards standardized IT practices and people-centric solutions.
Miniaturization
Exploring advanced SCADA hacking techniques, focusing on miniaturization challenges in embedded devices and novel algorithms for stealthy attacks on industrial control systems.
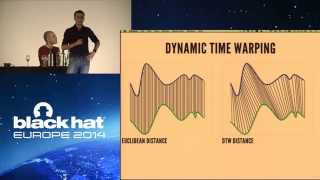
Gyrophone - Eavesdropping Using a Gyroscope
Explore how smartphone gyroscopes can be exploited to eavesdrop on nearby speech, bypassing microphone permissions and posing privacy risks. Learn about potential attacks and defenses.
Industrial Control Systems - Pentesting PLCs 101
Hands-on workshop exploring ICS security, focusing on PLC vulnerabilities. Learn to assess and exploit industrial control systems using real-world examples and practical techniques.
Industrial Control Systems - Pentesting PLCs 101
Hands-on workshop exploring penetration testing techniques for industrial control systems, focusing on PLCs. Learn to identify vulnerabilities and attack Siemens and Schneider devices.
LTE & IMSI Catcher Myths
Explore LTE security vulnerabilities and IMSI catcher techniques. Learn how popular phones can be exploited on 4G networks, with live demonstrations and in-depth analysis of baseband software weaknesses.
Spread Spectrum Satcom Hacking - Attacking The Globalstar Simplex Data Service
Explore reverse engineering and exploitation of GlobalStar's simplex satcom protocol, uncovering vulnerabilities in satellite communications and demonstrating interception and spoofing capabilities.
Broadcasting Your Attack - Security Testing DAB Radio in Cars
Explore vulnerabilities in DAB radio systems in cars, potential security risks, and implications for automotive cybersecurity using Software Defined Radio and custom testing tools.