Zero-Configuration Runtime Software Component Detection
Discover how to detect vulnerable software components in running systems using eBPF, focusing on Java applications and container images without initial configuration.
Verifiable eBPF Traces for Supply Chain Artifacts with Witness and Tetragon
Explore how Cillium Tetragon and Witness integration simplifies build environment validation and detects tampered tooling, enhancing supply chain security through eBPF traces and build policies.
Fileless Attack - Detecting the Undetectable
Explore fileless attacks in Linux containers, their detection using eBPF tools like Falco, Tracee, and Tetragon, and learn to identify unexpected activities in cloud-native environments.
Fun with Continuous Compliance
Explore continuous compliance strategies, including OSCAL for automated assessments and OSS tools like Falco and Voucher for scalable implementation, to streamline and modernize your DevSecOps compliance approach.
Vanquishing Vulnerabilities - Preparing for Critical CVEs
Prepare for critical vulnerabilities with tools and practices for container image scanning, policy enforcement, network control, runtime configurations, and behavior monitoring.
Securing Shopify's Software Supply Chain - Mitigating Supply Chain Attacks
Explore techniques for securing software supply chains, including cloud-based defenses, trust establishment, and malicious behavior detection, drawing from Shopify's experiences.
Evolution of Application Visibility for Telcos: From Programmable Switches to Cloud Native
Explore the evolution of application visibility for telcos, from programmable switches to cloud-native solutions, focusing on scalability, affordability, and tackling encryption challenges in complex modern applications.
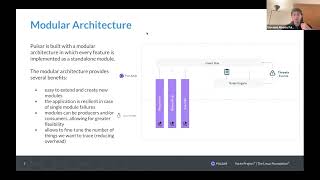
Embedded Runtime Security with Pulsar - YPS 2023.11
Explore Pulsar, an eBPF-powered threat detection system for IoT. Learn its architecture, capabilities, and integration with Yocto Project for enhanced embedded system security.
DevSecOps by Default: Lessons from Log4Shell - What We Have, Can, and Must Learn
Explore DevSecOps strategies post-Log4Shell, focusing on strengthening software supply chains, vulnerability detection, and implementing "Secure by Default" policies using open-source tools.
Relational Observability for Cloud-Native Security and Data Science
Explore SysFlow, a runtime observability framework for cloud-native security. Learn about its telemetry format, behavioral graphs, and tools for collecting and processing data in Kubernetes environments.
Tetragon Auditing and Enforcement
Explore Tetragon's auditing and enforcement capabilities with John Fastabend, gaining insights into advanced Linux security and monitoring techniques.
Tetragon: eBPF-Based Security Observability and Runtime Enforcement Tool
Explore Cilium's Tetragon: a powerful eBPF-based tool for real-time security observability and runtime enforcement in Linux systems. Learn its design and practical applications.
Kepler Deep Dive: Measuring Pod Energy Consumption - CNCF Minutes 26
Explore Kepler, a Prometheus exporter using eBPF to estimate Pod energy consumption. Learn its architecture, installation, and functionality for efficient Kubernetes monitoring.
Kepler - Powering Up the Efficiency of Your Cluster
Explore Kepler, a Kubernetes-based tool for measuring container energy consumption, enabling sustainable cluster management and optimized energy use through metrics and observability.
Cilium Overview - Introduction to Cloud-Native Networking with eBPF
Discover how Cilium leverages eBPF technology for cloud-native networking and security, exploring key features and implementation strategies for modern infrastructure.
Developing and Managing eBPF Programs with Rust
Explore eBPF programming with Rust, covering network programs, eBPF maps, container security, and LSM support for enhanced system observability and performance.
The Future of Service Mesh: eBPF as Silver Lining or Silver Bullet - Panel Discussion
Experts discuss service mesh evolution, comparing eBPF and sidecar approaches, exploring their impact on performance, debugging, and adoption challenges in cloud-native environments.
Setting Up Monitoring for Calico's eBPF Data Plane
Learn to set up and optimize monitoring for Calico's eBPF Data Plane, enhancing network visibility and performance in cloud-native environments.
Composability in Cloud Native Ecosystems - Compounding Value Through Modular Design
Explore how composability in cloud-native ecosystems drives innovation, accelerates development, and creates compounding business value across various industries.
Cilium: Introduction, Vision, and Updates
Explore Cilium's vision, updates, and applications in cloud-native networking. Learn about its service mesh capabilities, end-user perspectives, and upcoming features from industry experts.
Cloud Native: Using Calico for eBPF, Linux, and Windows on Azure and AKS
Explore Calico's advanced networking features for Azure AKS, including eBPF, source IP preservation, and efficient pod migration, enhancing Kubernetes performance and security.