TTP-based Threat Hunting with Security Analytics and Falco Alerts
Explore attacker techniques and defender strategies using Unguard. Learn to conduct reconnaissance, gain access, and achieve persistence. Discover how to detect compromises with Dynatrace and Falco for real-time monitoring and forensic analysis.
What's Really Happening Inside My Containers? - Exploring with Falco
Explorando segurança em containers com Falco: detecte atividades suspeitas, previna ameaças e proteja seus recursos contra acessos não autorizados e malwares.
Fun with Continuous Compliance
Explore continuous compliance strategies, including OSCAL for automated assessments and OSS tools like Falco and Voucher for scalable implementation, to streamline and modernize your DevSecOps compliance approach.
Vanquishing Vulnerabilities - Preparing for Critical CVEs
Prepare for critical vulnerabilities with tools and practices for container image scanning, policy enforcement, network control, runtime configurations, and behavior monitoring.
Securing Shopify's Software Supply Chain - Mitigating Supply Chain Attacks
Explore techniques for securing software supply chains, including cloud-based defenses, trust establishment, and malicious behavior detection, drawing from Shopify's experiences.
DevSecOps by Default: Lessons from Log4Shell - What We Have, Can, and Must Learn
Explore DevSecOps strategies post-Log4Shell, focusing on strengthening software supply chains, vulnerability detection, and implementing "Secure by Default" policies using open-source tools.
Security in the Cloud with Falco - Overview and Project Updates
Discover Falco, the Cloud-Native Runtime Security project for Kubernetes threat detection. Learn about recent developments, upcoming roadmap, and new features like ARM support, eBPF probe, and Cloud Security use cases.
Falco and Atomic Red Team - Real-time Threat Detection in Cloud-Native Systems
Explore real-time threat detection in cloud-native systems using Falco and Atomic Red Team, enhancing security practices for modern infrastructure.
A Wind of Change for Threat Detection
Explore advanced cloud native security threat detection using eBPF and Falco, focusing on innovative approaches to create high-value kernel signals and leverage data analytics for behavior-based detection.
Falco and Atomic Red Team - Real-Time Threat Detection in Cloud Native Systems
Explore real-time threat detection in cloud-native systems using Falco and Atomic Red Team. Learn effective strategies for enhancing security and identifying potential vulnerabilities in modern infrastructures.
Falco and eBPF: Optimizing Large-Scale Tracing Tools
Explore eBPF's potential in high-throughput scenarios, focusing on Falco's syscall tracing. Learn about challenges, mitigations, and future enhancements for large-scale tracing tools.
Klustered: eBPF Edition - Debugging Kubernetes with Advanced Tools
Experts discuss eBPF challenges in Kubernetes, showcasing debugging, networking, and security tools. Learn how eBPF revolutionizes cluster management through practical demonstrations and insights.
Bypassing Falco - How to Compromise a Cluster without Tripping the SOC
Explore techniques to bypass Falco's default ruleset, enabling stealthy cluster compromise. Learn 9 bypass classes for target enumeration, privilege escalation, and lateral movement without alerting security teams.
Threat Hunting at Scale - Auditing Thousands of Clusters With Falco and Fluent
Explore large-scale threat hunting using Falco and Fluent for auditing thousands of Kubernetes clusters, covering data pipelines, monitoring, log processing, and challenges.
Extend Falco with Plugins - Trigger Alerts with Any Stream of Events
Learn to extend Falco's capabilities with plugins, enabling custom event streams and alerts. Explore architecture, plugin types, SDK usage, and real-world applications for enhanced cloud-native security monitoring.
PolicyReport CRD - Managing Admission Control, Runtime, and Scan Reports
Explore PolicyReport CRD for standardized Kubernetes policy management. Learn about adapters for various engines and discover Policy Reporter's integration capabilities.
Falco to Pluginfinity and Beyond - Cloud-Native Runtime Security
Explore Falco's evolution as a cloud-native runtime security project, including its new plugin system for enhanced cloud security and threat detection in Kubernetes environments.
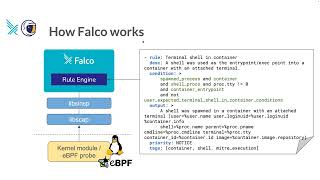
gVisor and Falco - Strengthening Kubernetes and Container Security with Visibility
Explore container sandboxing with gVisor and enhance security monitoring using Falco, improving Kubernetes protection without compromising visibility.
Using Falco and eBPF to Protect Your Applications
Explore Falco and eBPF for application protection. Learn about runtime security, syscalls, and Falco's architecture. Discover how to implement, connect, and contribute to this powerful security tool.
Runtime Kubernetes Security: Threat Detection with Falcosidekick
Explore runtime Kubernetes security and threat detection using Falcosidekick. Learn practical scenarios, UI demonstrations, and testing techniques for enhanced cluster protection.
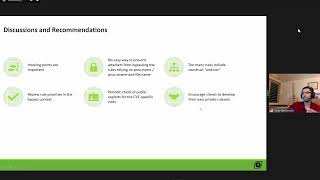
Bypassing Falco - Cluster Compromise Without Tripping the SOC
Explore techniques for evading Falco detection in Kubernetes clusters, learning how to compromise systems without alerting security operations centers.