Improving eBPF Complexity with a Hardware-backed Isolation Environment
Explore hardware-backed isolation for eBPF, enhancing complexity management and security in Linux kernel development.
Modernizing bpftrace with libbpf
Explore advancements in bpftrace modernization using libbpf, enhancing system observability and performance analysis capabilities for Linux kernel developers.
Chaos Engineering in the Fast Lane: Accelerating Resilience with eBPF
Explore chaos engineering with eBPF, enhancing resilience in Kubernetes. Learn advanced techniques, AI integration, and practical experiments for robust system design and security.
Zero-Instrumentation Observability Based on eBPF - Conf42 SRE 2024
Explore zero-instrumentation observability using eBPF for modern systems. Learn about collecting telemetry data, leveraging eBPF, and implementing metrics, traces, and CPU profiling without code changes.
Let's Go Triple Active with Three Clouds and Cilium
Explore triple-active architecture across three clouds using Cilium for seamless connectivity and enhanced reliability in distributed systems.
eBPF: Enhancing Kubernetes with Powerful Linux Kernel Technology
Explore eBPF's power in Kubernetes: enhance observability, security, and performance. Gain expert insights on optimizing your cluster with this versatile Linux kernel technology.
Kubernetes Observability with eBPF
Explore Kubernetes observability using eBPF technology, enhancing security and performance monitoring in cloud-native environments.
eBPF Superpowers - Platform Engineering
Explore eBPF's powerful capabilities for enhancing Linux kernel functionality and revolutionizing networking, security, and observability in modern systems.
eBPF Superpowers: A Dynamic Kernel Revolution
Explore eBPF's revolutionary impact on cloud native applications, with focus on observability, networking, and security advantages through concrete examples.
Intro to eBPF: Write a Simple eBPF Program - Lecture 1
Learn to write simple eBPF programs, exploring their potential in Linux kernel observability, networking, and security. Gain hands-on experience with this powerful technology.
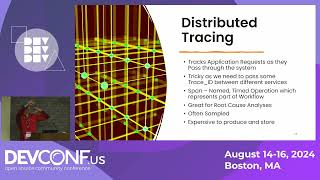
Zero-Instrumentation Observability Based on eBPF
Explore eBPF-based telemetry data collection for enhanced system observability, covering metrics, logs, traces, and container activities for efficient troubleshooting.
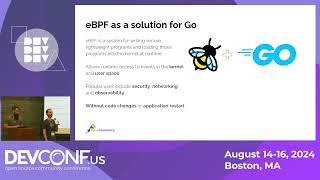
Auto-Instrumenting Go Libraries for Tracing with eBPF and OpenTelemetry - Lecture 1
Explore auto-instrumentation for Go using eBPF and OpenTelemetry, enabling context propagation and tracing without code changes or restarts. Learn technical details, challenges, and future plans.
Tracing the Linux Kernel with eBPF and Rust
Explore eBPF for Linux kernel instrumentation, learn to write eBPF code in Rust, and discover Exein Pulsar, an eBPF-based security observability tool for Linux.
Enhancing Rust with BTF Debug Format Support
Explore recent advancements in BTF debug format support for Aya and bpf-linker. Learn about BTF generation, LLVM's role, and implementing BTF information for Rust programs in eBPF technology.
Modernizing Falco with Go - A Story of Love and Betrayal
Explore the challenges and solutions of integrating Go with complex C++ codebases, focusing on Falco's adoption of CGO for performance-critical runtime security in cloud-native environments.

eBPF for Go Developers: Use Cases and Implementation
Explore EBPF's potential in Go development, covering use cases, implementation strategies, and popular open-source projects. Gain insights to effectively integrate EBPF into your Go projects.
Handling Complex Guest Exits with eBPF
Explore eBPF programs for efficient handling of complex KVM guest exits, reducing latency and improving virtualization performance.
Fast by Friday: Why Kernel Superpowers are Essential
Explore efficient computing methodologies using kernel technologies like eBPF to solve performance issues quickly, saving cycles and carbon while improving user experience and reducing costs.
Kubernetes CKS Certification Guide 2023 - Exam Preparation and Falco Demo
Explore Kubernetes CKS certification essentials, including exam tips, cloud-native concepts, and Falco security tool. Gain insights and practical knowledge to become a certified Kubernetes security specialist.
All-in-One Kubernetes Observability Using Groundcover
Explore Kubernetes observability with groundcover, an eBPF-based monitoring solution. Learn to quickly identify and resolve issues through five failure scenarios, without instrumentation.
A New Choice for Istio Data Plane: Architectural Innovation for Brand-New Performance
Explore innovative Istio data plane solution using eBPF and kernel enhancements for native traffic governance, reducing latency by 60%+ and simplifying mesh architecture. Discuss future service mesh evolution.