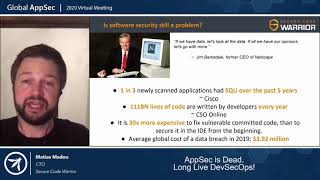
AppSec is Dead - Long Live DevSecOps
Explore the shift from AppSec to DevSecOps, focusing on creating secure code, working smarter, and implementing key pillars for effective security integration in software development.
Virtual AppSec Days Lightning Conference
Explore cutting-edge application security topics with industry experts in this fast-paced, informative conference session from OWASP Foundation.
Leave It to the Machines - AI and ML in Container Security
Explore how AI and ML empower security teams to proactively secure container-based applications, shifting left security capabilities and streamlining the development process.
Changed Responsibilities in Modern Development Practices
Explore how modern development practices like CI/CD and DevOps impact application security. Learn strategies for integrating security early in the development lifecycle and empowering developers with essential security skills.
Making Continuous Security a Reality with OWASP's AppSec Pipeline
Learn to implement continuous security testing using OWASP's AppSec Pipeline tool. Discover field-tested methods, Docker containers for automation, and integration with OWASP Defect Dojo for issue management.
Scaling Security in Leading Companies - DevOps and CI/CD Best Practices
Discover pro-tips and actionable lessons from mature security teams on scaling security in modern software development. Learn effective strategies for buy-in, engineering projects, analysis integration, and production monitoring.
Threat Modeling of Containerized Applications - Three Levels of Complexity
Optimize threat modeling for containerized applications, focusing on efficiency, new dimensions, and real-world impact. Learn to measure success and implement incremental improvements in application security.
Looking Towards the Future of Open Source Vulnerability Management
Explore the evolving landscape of open source security, focusing on vulnerability management strategies, industry trends, and best practices for effective remediation and continuous security integration.
DevSecOps in 2031: How Robots and Humans Will Secure Apps Together
Explore the future of DevSecOps in 2031, where humans and robots collaborate to secure applications. Learn about AI pair programming and innovative approaches to tackle evolving cybersecurity challenges.
Topics of Interest: Developers Struggle with Application Security and How to Make It Better
Explore challenges in application security for developers and learn strategies to improve DevSecOps practices, drawing from real-world experiences at major tech companies.
OWASP Serverless Top 10 - Understanding Security Risks in Serverless Applications
Explore the top 10 security risks in serverless architectures, understanding vulnerabilities and best practices for securing cloud-native applications.
Flipping the Script on Application Security
Explore innovative approaches to application security, challenging traditional methods and introducing fresh perspectives for more effective protection strategies.
Software Supply Chain Security
Explore software supply chain security with expert Vandana Verma, covering key concepts, best practices, and strategies to protect your development pipeline from vulnerabilities and attacks.
Using IAC to Accelerate Threat Modeling
Explore innovative techniques for accelerating threat modeling using Infrastructure as Code (IAC), enhancing security practices in software development and deployment.
Security as Code: A DevSecOps Approach
Explore DevSecOps principles and practices for integrating security into the software development lifecycle, emphasizing automation and collaboration for robust application security.
Shifting Security Everywhere
Explore strategies for integrating security throughout the software development lifecycle, emphasizing proactive measures and collaboration between development and security teams.
Developer Driven Security in High-Growth Environments
Explore strategies for implementing developer-driven security practices in rapidly expanding tech environments, focusing on scalable and efficient approaches.
How to Have Visibility and Security of a CI/CD Pipeline
Discover strategies for enhancing visibility and security in CI/CD pipelines, focusing on best practices and tools to safeguard your software development lifecycle.
The Power of DevSecOps in Web3 and Blockchain
Explore DevSecOps principles in Web3 and blockchain, focusing on security integration for decentralized applications and smart contracts development.

Hacking and Defending APIs - Red and Blue Make Purple
Learn techniques for both attacking and defending APIs, combining offensive and defensive security perspectives to enhance overall API protection.
Shift Left Security with the Security Test Pyramid
Explore the concept of shifting security testing left in the development process using the Security Test Pyramid, enhancing software security from the early stages.