Leveraging DevSecOps to Escape the Hamster Wheel of Never Ending Security Failures
Explore DevSecOps strategies to break free from recurring security failures, focusing on integration, collaboration, and proactive measures in software development.
Stable 26 - Are You Ready to Leverage DevSecOps - Get Ready and Use It for Good
Leverage DevSecOps effectively: Learn about software lifecycle, integration, training, and security best practices for developers and teams.
Extensible DevSecOps Pipelines with Jenkins, Docker, Terraform, and a Kitchen Sink Full of Scanners
Learn to build robust DevSecOps pipelines using Jenkins, Docker, Terraform, and various scanning tools for enhanced security and efficiency in software development.
A DevSecOps Approach to Bringing Security Beyond the Security Team
Explore DevSecOps strategies to integrate security across teams, enhancing collaboration and improving overall system protection beyond traditional security boundaries.
DevSecOps Pipeline Design Patterns That Can Save the Day
Explore essential DevSecOps pipeline design patterns, from DDD application to architectural insights, enhancing continuous delivery and pipeline efficiency for developers.
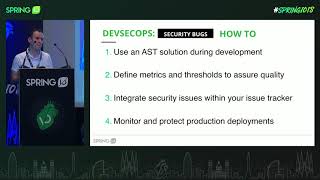
Making DevSecOps a Reality in Your Spring Applications
Integrating security into DevOps for Spring applications: automating testing, improving quality, and enhancing release processes through CI/CD pipeline integration with Jenkins.
DevSecOps - By Any Other Name
Explore DevSecOps origins, challenges, and implementation pitfalls. Uncover the gap between DevSecOps label and intent, and learn from past software development transformations.
The Common Configuration Scoring System for Kubernetes Security
Explore KCCSS, an open-source framework for assessing Kubernetes workload risks. Learn how it calculates scores, its implementation in kube-scan, and best practices for securing K8s applications.
Everything You Should Be Doing, But Aren’t - DevSecOps for K8s Workflows
Comprehensive guide to implementing DevSecOps in Kubernetes workflows, covering application security, threat detection, and governance as code with live demonstrations using CNCF projects.
Protecting Ourselves from CNCFgate - Software Supply Chain Security at CNCF - Practices, and Tools
Explore cloud-native software supply chain security practices, challenges, and tools. Learn strategies to protect against vulnerabilities and attacks in complex software systems.
Modern Least Privilege with DevSecOps
Explore modern least privilege principles in DevSecOps, focusing on platform teams, continuous delivery, and scaling to zero for enhanced security and efficiency in cloud-native environments.
Deja Vu - Let's Think About Security Again
Explore cloud-native security transformations, DevSecOps, and Zero Trust in Crossplane. Discuss potential gaps, new tools, and best practices for developers and security experts in cloud infrastructure management.
Strengthening Your Kubernetes Security - Cloud Native Way
Explore Kubernetes security threats, misconfigurations, and defense mechanisms. Learn to detect vulnerabilities, prevent attacks, and secure cloud environments using tools like Kubestriker.
Supply Chain Security with the Jenkins Templating Engine
Comprehensive introduction to DevSecOps, exploring software security scanning and scaling principles using Jenkins Templating Engine for shared, tool-agnostic pipelines across teams.
Value Stream Management Platforms for DevSecOps for 5G Smart City Enablement
Explore value stream management platforms for DevSecOps in 5G smart city enablement, covering industry leaders, lifecycle management, end-to-end solutions, and key insights from experts.
Using IAST to Unlock the Benefits of DevSecOps
Explore how Interactive Application Security Testing (IAST) revolutionizes DevSecOps, enabling real-time vulnerability detection, streamlined security processes, and faster delivery of secure code.
Implement DevSecOps in Azure
Comprehensive guide to implementing DevSecOps in Azure, covering security controls, governance, and best practices for secure development and deployment across the entire application lifecycle.
Implement DevSecOps in Azure
Learn to implement comprehensive security and compliance in Azure, from subscription-level controls to secure development and deployment, with practical tools and techniques for efficient DevSecOps.
DevSecOps for Developers - How To Start
Explore integrating security into DevOps, leveraging existing processes and tools to improve your security posture efficiently, even with limited resources.
Measuring DevSecOps - Building Metrics to Understand Effectiveness and Success
Explore essential DevSecOps KPIs, learn to track and visualize security metrics, and gain insights to improve your team's effectiveness using Azure DevOps and supportive tools.
The Future of AppSec is Cloud-Native
Explore cloud-native technologies' impact on application security, transforming DevSecOps from blocker to enabler. Learn tools and processes for enhanced visibility, vulnerability discovery, and feedback loops.