Security While Scaling Agile - Lessons Learned
Integrating software security practices into scaled Agile frameworks: strategies, challenges, and lessons learned for maintaining security without impeding product delivery.
Threat Modeling Kubernetes - A Lightspeed Introduction
Discover threat modeling for Kubernetes: Learn to identify risks, understand adversarial techniques, and implement preventive measures to enhance cloud-native system security and delivery velocity.
A 10-Step Guide for Integrating Security Metrics Into Your Observability Stack
Discover a 10-step approach to integrate security metrics into your observability stack, enhancing application robustness and decision-making by correlating metrics from different services using the Prometheus ecosystem.
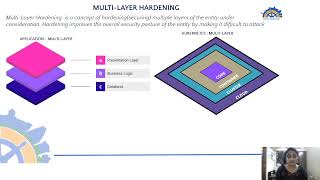
Multi-Layer Hardening in Kubernetes - DevSecOps Practices and Tools
Explore DevSecOps practices and tools for enhancing Kubernetes security, including multi-layer hardening techniques, industry standards, and a unified DevSecOps pipeline approach.
A New Way to Roll - Supply Chain Choreography for Enterprise Grade Kubernetes
Explore enterprise-grade Kubernetes deployment using supply chain choreography. Learn DevSecOps practices, CI/CD pipeline integration, and secure software supply chain management for cloud-native applications.
Who's Verifying Your Signatures? Approaching Private Container Image Signing
Explore container image signing for private use, comparing open-source and internal challenges. Learn about leading frameworks and their scalability for secure software delivery.
Reducing the Sticker Price of Kubernetes Security
Hands-on techniques and open-source tools for enhancing Kubernetes security, including image verification, Pod Security Standards, and SecComp profiles to prevent vulnerability exploits.
A 10-Step Guide for Integrating Security Metrics Into Your Observability Stack
Discover a 10-step approach to enhance your observability stack with security metrics, focusing on integrating Trivy with Prometheus for robust application monitoring and protection.
Securing the IaC Supply Chain
Explore securing Infrastructure as Code supply chains, applying software security principles to IaC pipelines. Learn about Crossplane's integration with Sigstore for enhanced provenance and attestations.
Guardians of the Runtime - Leveraging Behavioral Analysis and Policies for Kubernetes Security
Explore innovative Kubernetes security using behavioral analysis in CI testing and native policies. Learn hands-on practices for implementation and enforcement to protect against latest threats.
Malicious Compliance: Reflections on Trusting Container Scanners
Explore creative ways to bypass container image analysis and admission control detection, revealing limitations of validation tools and improving security policy creation.
IDP Security for Platform Engineers Using Backstage and Kubescape
Explore how Backstage and Kubescape integrate to provide comprehensive Kubernetes security coverage, enabling visualization and management of security posture across your pipeline.
Kubernetes Security Response Committee: Introduction and Deep Dive
Explore the Kubernetes Security Response Committee's role, vulnerability lifecycle, and key findings from the 2022 security audit. Learn about reporting processes and community impact.
Prevent Embarrassing Cluster Takeovers - Detecting and Mitigating Configuration Risks
Discover how to secure Kubernetes clusters against common misconfigurations and vulnerabilities using Kubeaudit, an open-source scanner that detects and mitigates risks without hindering developer productivity.
Falco: Cloud-Native Runtime Security for Kubernetes - Recent Developments and Roadmap
Discover Falco: Cloud-Native Runtime Security for Kubernetes. Learn about recent developments, improved eBPF support, security enhancements, ecosystem integrations, and the project's roadmap from experienced contributors.
Kubernetes Security Implementation Landscape
Explore Kubernetes security implementation strategies and best practices with expert Zhang Jintao, gaining insights to enhance your cloud-native infrastructure protection.
Hands-on Hacking Kubernetes and Ways to Prevent It
Hands-on workshop exploring Kubernetes vulnerabilities and prevention strategies. Demonstrates remote code execution exploit and teaches mitigation techniques for enhanced container security.
Unpacking Open Source Security in Public Repositories and Registries
Explore security risks in popular open-source projects and public registries. Learn about common misconfigurations, vulnerabilities, and best practices to safeguard your systems when using public resources.
Securing Kubernetes
Explore Kubernetes security strategies and best practices to protect your containerized applications and infrastructure in this informative session.
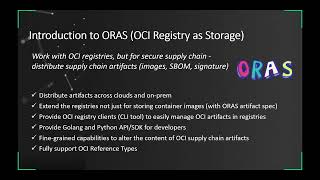
Secure Container Supply Chain with Notation, ORAS, and Ratify
Explore tools for securing container supply chains: Notation for signing artifacts, ORAS for distributing OCI artifacts, and Ratify for verifying container images.
Creating Security Policies and Controls for Kubernetes Using ChatGPT
Explore how to leverage ChatGPT for creating robust security policies and controls in Kubernetes environments, enhancing your cloud-native security practices.