Attacking Microservice Systems: Methods and Practical Tips
Discover methods and practical tips for attacking microservice systems, exploring new security architecture patterns and vulnerabilities specific to this increasingly popular design approach.
A Look Under the Hood of CNCF Security Audits
Insights into CNCF security audits: process, expectations, outcomes, and common vulnerabilities. Explores experiences from auditing six major projects and the value of audit reports for contributors and researchers.
Securing Your Cloud Native Stack with Policy-as-Code and OPA
Explore policy-as-code and OPA for securing cloud-native stacks. Learn implementation strategies and best practices for robust security in modern infrastructure.
Zero Privilege Architectures - Modern IT Security Approach
Explore modern IT architecture for enhanced security, using CI/CD, data services, events, and IAM. Learn how ING implements this approach and address common concerns about adoption and compatibility.
Security Does Not Need to Be Fun - Ignoring OWASP to Have a Terrible Time
Explore OWASP's free tools and resources for designing and implementing secure web applications, addressing common security challenges in the software development lifecycle.
Falco and Atomic Red Team - Real-time Threat Detection in Cloud-Native Systems
Explore real-time threat detection in cloud-native systems using Falco and Atomic Red Team, enhancing security practices for modern infrastructure.
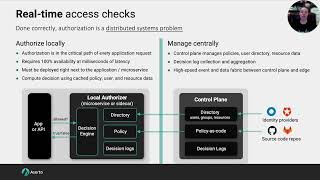
The Current State of Cloud-Native Authorization
Explore the latest developments in cloud-native authorization, examining key trends, challenges, and best practices for securing modern distributed systems.
Azure Vulnerability Testbed (AzGOAT) - Understanding and Hardening Azure Security
Explore Azure security vulnerabilities and defenses with AzGOAT, a lab environment for understanding attack surfaces, designing secure solutions, and minimizing threats in Azure environments.
Cloud Native Security Landscape - Myths, Dragons, and Real Talk
Explore cloud-native security across the software lifecycle, from open-source creation to runtime threat detection. Learn about key projects, developer-security team collaboration, and separating real risks from myths.
Cloud Native Security 101 - Building Blocks, Patterns and Best Practices
Explore cloud native security fundamentals, attack vectors, and best practices for implementing continuous security in cloud applications without compromising innovation.
Security Does Not Need to Be Fun - Ignoring OWASP to Have a Terrible Time
Explore OWASP's free tools for web application security testing and implementation. Learn to identify issues early and integrate security best practices throughout the software development lifecycle.
Securing the Cloud with Canonical Kubernetes and Kubescape
Learn to secure cloud environments using Canonical Kubernetes and Kubescape, exploring key strategies and tools for robust protection in modern containerized infrastructures.
GitHub Lesser Known Vulnerabilities You Should Be Aware Of
Explore lesser-known GitHub vulnerabilities to enhance your security awareness and protect your projects from potential threats.
Past, Present, and Future of Tetragon - First Production Use Cases and Future Trajectory
Explore Tetragon's journey from inception to v1.0, including production use cases, security challenges, and future goals. Learn how BPF-based security pitfalls were avoided and performance issues solved.
Security Safari: A Journey Through the Wilderness of Securing Budding Opensource Projects
Explore essential security guidelines for open-source projects, distilled from CNCF and OpenSSF resources. Learn actionable steps to implement fundamental security measures from day one.
Using Static Analysis to Catch Configuration Vulnerabilities
Learn to secure containers and IaC using static analysis. Discover how to identify misconfigurations, prevent vulnerabilities, and implement early detection in your development workflow for improved application security.
Securing Multi-Cluster Cassandra and GenAI Deployments
Explore top cloud threats, risk detection strategies, and best practices for securing Cassandra and GenAI deployments. Includes practical demonstrations on live clusters and AI applications.
Developers Are Taking Security Seriously - Evolution in Cloud-Native Security
Explore the evolution of security in cloud-native environments with insights from Linux Foundation's Director of Open Source Supply Chain Security.
Cloud Native Application Security with Open Source
Explore cloud native app security risks, identification methods, and open-source tools for risk mitigation in developer-friendly environments. Learn to integrate security into workflows.
Diving into Java Ecosystem Security with DevOps and Open Source
Explore Java ecosystem security through DevOps and OpenSource, addressing challenges and opportunities in software supply chain security with real-world scenarios and DevSecOps principles.
Building Secured Container Images with Wolfi - Zero CVE Container Development
Discover how to achieve zero CVE container security using Wolfi OS, a modern alternative to traditional distroless solutions, with practical insights from VPBank's successful implementation.