How to Prove the Safety of Your Software
Explore software safety through SBOMs: Learn to create, analyze, and distribute software bills of materials for enhanced security and transparency in your applications.
Iterative Threat Modelling - Security in Agile Development
Learn iterative threat modeling for agile development. Explore misconceptions, methodologies, and practical examples using OWASP Juice Shop. Discover effective ways to identify, prioritize, and mitigate security risks.
Securing the Software Supply Chain - Beyond SBOM Risk Assessment
Explore advanced software supply chain security strategies, focusing on risk assessment, contributor profiles, project dynamics, and integrating security into deployment pipelines.
Why We Need Security Domains: A Comprehensive Approach to Cybersecurity
Explore essential cybersecurity domains, from compliance to hacking, and understand their importance in developing comprehensive security strategies for modern organizations.
Detecting Known Unknowns in DevSecOps - A Tailored Defensive Approach
Explore TTP-based threat hunting with the Pandora Project. Learn about tailored defensive solutions, methodology workflows, and practical use cases for detecting known unknowns in cybersecurity.
Adding Security for Reliable Continuous Delivery
Enhance security in continuous delivery: Learn containerization challenges, vulnerabilities, misconfigurations, supply chain attacks, and IAM. Explore solutions and see a practical demo.
Supply Chain Attacks: Focusing on NPM Vulnerabilities - DevSecOps 2023
Explore supply chain attacks focusing on NPM, learn defensive strategies, and discover research findings on vulnerabilities in package ecosystems. Gain insights into detection tools and solutions.
OSS Supply Chain Security: Drowning in Information, While Starving for Wisdom?
Explore challenges and opportunities in open source software supply chain security, focusing on actionable knowledge for developers and operators amid increasing information availability.
Securing Your Software Supply Chain with SBOMs
Explore software supply chain security through SBOMs, focusing on artifact provenance and package identification for enhanced protection.
DevSecOps Adoption: Lessons from the Past - Cloud Native Summit
Explore DevSecOps adoption strategies, drawing parallels from past digital transformations. Gain insights on integrating security seamlessly into development processes and overcoming organizational challenges.
Open Automation and the Future of DevSecOps
Explore the future of DevSecOps through open automation, AI/ML, and integrated workflows. Learn to implement event-driven architecture and optimize flow metrics for enhanced security and compliance.
DevSecOps: A Love Triangle
Explore the dynamic interplay between Dev, Sec, and Ops in enterprise IT through live demos and hacking of Kubernetes and CNCF ecosystem capabilities.
Forging a Secure and Observable DevOps Frontier
Explore AI-driven observability and ML-enhanced security in DevOps. Learn best practices for integrating AI into the DevSecOps lifecycle to balance speed and safety in digital transformation.
Security Observability 101 - Thinking Inside the Box
Explore runtime instrumentation for software security using Java Observability Toolkit. Learn to analyze defenses, identify vulnerabilities, create sandboxes, and enforce policies for harmonious Dev, Sec, and Ops collaboration.
Reliability, Everyone’s Responsibility - Intro to Site Reliability Engineering Practices
Explore the fundamentals of Site Reliability Engineering, including SLAs, SLOs, and SLIs. Learn to establish a culture of reliability and navigate complex systems for robust platform maintenance.
Security Project Management: How to Be Agile - AppSecEU 2016
Learn effective security project management techniques for Agile environments, focusing on integrating security practices into fast-paced development cycles.
An Open Source Architecture for Modernizing Market Risk Management
Modernizing market risk management with open-source architecture: scaling calculations, accelerating model deployment, and improving risk management through hybrid cloud, DevSecOps, and event-driven architecture.
How Security Can Keep Pace with Continuously Evolving Cloud-Native Applications
Explore dynamic security approaches for cloud-native apps, aligning with modern development lifecycles and infrastructure-as-code to ensure security evolves alongside rapid architectural changes.
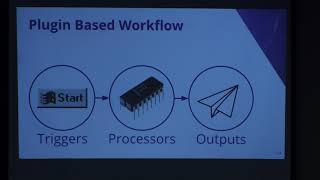
Orchestrating Security Tools with AWS Step Functions - 2018
Automate security reviews in CI/CD pipelines using AWS Step Functions. Learn to deploy serverless systems for integrating security tools like static analysis and container scanning into developer workflows.
Serverless Security: A Pragmatic Primer for Builders and Defenders - 2017
Explore serverless security challenges and practical approaches in software supply chain, delivery pipeline, data flow, and attack detection. Learn serverless basics and adoption patterns.
Architecting for Security in the Cloud - 2017
Discover strategies to identify and close security gaps in cloud applications, building robust architectures that can withstand Internet attacks while maintaining scalability and agility.