OWASP Flagship Projects - OWASP DefectDojo
Learn about OWASP DefectDojo, an open-source application security management tool. Explore its features, automation capabilities, deployment options, and community-driven development.
OWASP Cloud-Native Application Security Top 10 Flagship Project
Explore key security challenges and best practices for cloud-native applications, focusing on OWASP's top 10 vulnerabilities and mitigation strategies.
Human Factors That Influence Secure Software Development
Explores human factors influencing secure software development, including environmental conditions, developer characteristics, and team dynamics. Discusses strategies to identify and mitigate vulnerability-prone code before issues arise.
Flying Above the Clouds - Securing Kubernetes
Explore Kubernetes security, from container isolation to authentication and authorization. Learn to build resilient cloud-native systems and deploy secure services in a distributed environment.
A New Framework to Automate MSTG and MASVS in Your CI/CD Pipeline
Automate mobile app security testing using BDD and UI automation frameworks. Integrate OWASP MASVS/MSTG into CI/CD pipelines for faster, repeatable security checks at DevOps speed.
Open Source Security Tools for Kubernetes Applications
Explore open-source tools for securing Kubernetes applications, covering image scanning, runtime security, and anomaly detection. Learn practical strategies for maintaining a secure cloud-native environment.
Lessons from Integrating Third Party Library Scanning in DevOps Workflow
Integrating third-party library scanning in DevOps: automation strategies, architectural choices, and best practices for secure development at scale. Tips for seamless implementation and measuring success.
Making Security Approachable for Developers and Operators
Explore strategies to make security more accessible for developers and operators through APIs, secure-by-default platforms, and policy as code, enhancing overall security posture.
SecDevOps - Current Research and Best Practices
Explore current research and best practices in SecDevOps, covering static and dynamic analysis, security scaling, and infrastructure best practices for improved application security.
We Come Bearing Gifts - Enabling Product Security with Culture and Cloud
Explore innovative approaches to product security, emphasizing automation, cloud deployment, and engineering enablement. Learn how Netflix balances security impact with developer productivity.
Building a Secure DevOps Pipeline
Learn strategies to integrate security into DevOps, automate testing, and scale AppSec programs. Discover real-world examples of successful implementation across various companies, improving software development speed and security.
Practical Dynamic Application Security Testing within an Enterprise
Practical implementation of dynamic application security testing in enterprise DevOps, showcasing CI/CD pipeline integration and large-scale scanning methods for enhanced security coverage.
How to Stop Worrying About Application Container Security
Learn how to embrace container security for sensitive workloads, exploring challenges, benefits, and best practices. Gain insights from a real-world journey of adopting containers in production environments.
Test Driven Security in the DevOps Pipeline
Learn to implement Test Driven Security in DevOps, focusing on baseline controls, continuous testing, and preventing common vulnerabilities through specific, actionable security practices.
This Old App - A Guide to Renovating Apps for the Cloud
Explore strategies for migrating legacy applications to the cloud, considering various approaches, security implications, and organizational capabilities needed for successful cloud transitions.
Controlled Mayhem With Cloud Native Security Pipelines
Explore cloud-native security pipelines, comparing traditional and modern approaches, while addressing challenges in container orchestration, access control, and CI/CD processes.
Can We Automate Security?
Explore Microsoft's CI/CD pipeline security tools and lessons learned, focusing on automation strategies to enhance product and service security in the development process.
Bringing Rapid Prototyping to the Threat Model Process
Discover rapid threat modeling for Agile/DevOps environments, enhancing software security design tenfold through efficient risk analysis and automated workflows.
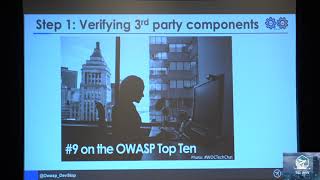
DevSecOps with OWASP DevSlop
Learn DevSecOps through hands-on examples with OWASP DevSlop. Explore secure component management, secret handling, testing techniques, and open-source tools to enhance your pipeline security.
Temporal - Security As Code - The New Model Of Achieving Security At Scale
Explore the concept of Security-as-Code, a scalable approach to implementing security controls through codification, automation, and software engineering practices.
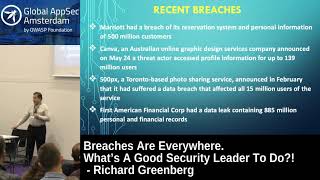
Breaches Are Everywhere - What’s A Good Security Leader To Do?
Explore strategies for security leaders to combat increasing breaches, from IoT vulnerabilities to phishing attacks. Learn essential skills and best practices for effective cybersecurity management.