BeyondProd- The Origin of Cloud-Native Security at Google - Brandon Baker - USENIX Enigma - 2020
Exploring Google's BeyondProd: A cloud-native security model emphasizing service trust, workload isolation, and automated vulnerability management for microservices-based architectures.
A Practical Guide to Fuzz Testing Embedded Software in a CI Pipeline - Dennis Kengo Oka - Ekoparty 2021: Hardware Hacking Space
Practical guide to implementing automated fuzz testing in CI pipelines for embedded software, using Zephyr RTOS as an example. Learn strategies, execution, and vulnerability detection.
Blue Team - Generando Visibilidad y Respondiendo Ante Ciberamenazas Desde un SOC
Metodología para detectar y responder ante ciberamenazas en organizaciones, abordando visibilidad, priorización y automatización desde un SOC. Incluye servicios, componentes y herramientas para una gestión eficaz.
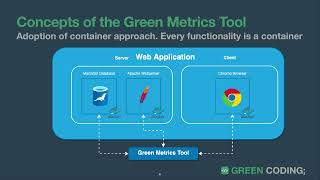
Green Coding - Measuring Energy Use of Arbitrary Applications and Software Stacks
Explore energy measurement and optimization for software applications using the Green Coding Metrics tool, enabling developers to create more sustainable and efficient digital solutions.
Making Invisible Things Visible - Tracking Down Known Vulnerabilities
Insights on software supply chain practices, revealing vulnerabilities in open source components and strategies for improving application security in high-performance development organizations.
Interact Differently - Get More from Your Tools Through Exposed APIs
Explore how to leverage exposed APIs and plugin interfaces in software tools to enhance functionality, streamline workflows, and create custom solutions for improved efficiency and effectiveness.
Skating on Thin Ice - A Crash Course in Kubernetes and Security
Explore Kubernetes fundamentals, security challenges, and best practices for container orchestration in this crash course, covering clusters, data management, and potential pitfalls.
Monitoring Attack Surface and Integrating Security into DevOps Pipelines
Explore strategies for integrating security into DevOps pipelines, focusing on attack surface monitoring, automated testing, and merging static and dynamic results.
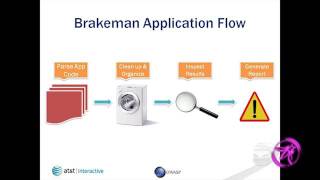
Brakeman & Jenkins - The Duo Detects Defects in Ruby on Rails Code
Explore static analysis tools for Ruby on Rails, focusing on Brakeman and Jenkins integration. Learn about security warnings, code updates, and best practices for detecting defects.
A DevOps View of AppSec
Explore DevOps history and its impact on AppSec, charting a path for DevSecOps success through standardization, automation, and Agile principles.
Micro-services Challenges - Istio to the Rescue
Explore Istio's solutions for micro-services challenges, including traffic management, policy enforcement, and security, to enhance scalability and operational efficiency.
Secure Configuration in the Cloud
Explore secure configuration management in cloud environments, focusing on protecting sensitive assets, managing configuration secrets, and implementing best practices for DevOps security.
AppSec Pipelines and Event-based Security - Moving Beyond a Traditional Security Test
Strategies for scaling AppSec programs using automation, continuous health checks, and event-based security to keep pace with rapid software development and delivery in large organizations.
Your Security Tools Are Just a Stop-Gap to Secure DevOps
Secure DevOps: Beyond tools, focus on risk assessment, threat modeling, and custom security controls. Learn to integrate security effectively in CI/CD pipelines for robust application protection.
Cloud Ops MasterClass - Lessons Learned from Cloud Automation
Explore cloud operations at scale, multi-account models, and automated guardrails for security and compliance. Learn to leverage automation tools for efficient cloud management and collaboration.
Be Mean to Your Code - Rugged Development & You
Pragmatic approaches and tools for ruggedizing your development lifecycle, from code commit to running system. Learn solutions for secure, resilient applications in fast-paced environments.
Breach Assessments - Are You Owned? You Can Find Out!
Discover techniques to detect ongoing network breaches, analyze anomalous behavior, and eradicate threats from Red Team experts turned Blue Team specialists.
Rugged Software Engineering
Practical strategies for rapid and secure software development, addressing challenges in modern engineering organizations and emphasizing rugged software practices.
Security Automation in the Agile SDLC - Real World Cases
Explore real-world examples of implementing successful security automation in fast-paced Agile development environments, focusing on practical strategies and processes.
Getting Security Up to Speed with CI - CD
Automating security in CI/CD: Learn about Threadfix-Centric Application Security Architecture, challenges in AppSec testing, and leveraging QA regression for enhanced coverage.
A Wander Through the World of Container Security
Explore container security, from Docker to Kubernetes, covering breakout vulnerabilities, networking challenges, and RBAC. Gain insights into potential threats and future attack vectors in containerized environments.