Cloud Native Governance, Risk, and Compliance - Policy-as-Code Applications
Explore policy-as-code's role in security, admission control, and automated compliance auditing. Learn how to implement governance across diverse environments for comprehensive risk management.
The Zen of Python Exemplars - Tying Metrics and Traces Together
Explore various methods to link metrics and traces using exemplars in Python, covering OpenTelemetry and Prometheus approaches for comprehensive observability in cloud-native environments.
Secure Multi-Mode Container Orchestration with Mirantis Kubernetes Engine
Explore Mirantis Kubernetes Engine for secure container orchestration in multi-mode environments, covering DISA STIG compliance, security controls, and hardening measures for both Kubernetes and Swarm workloads.
Malicious Compliance Automated: Building Secure Containers and Obfuscating Content
Explore container image compression techniques, secure image building, and obfuscation methods to reduce attack surfaces and disrupt vulnerability scanners. Learn automation and Linux kernel interfaces for enhanced security.
How OpenTelemetry Helps Generative AI
Explore how OpenTelemetry enhances Generative AI debugging and performance. Learn about observability's role in understanding AI behavior, improving outcomes, and leveraging OpenTelemetry for effective AI development.
Demystify Modern Signing: Keys, Certificates, and Envelopes
Explore practical aspects of cryptographic signing tools, covering key algorithms, signing envelopes, certificates, and verification, with a focus on identity-based signing using short-lived keys.
Kubernetes Deep Dive - Elevating ML Workload Monitoring to Art
Explore strategies for optimizing AI/ML workloads in Kubernetes, combining node health assurance with advanced monitoring techniques. Learn to implement robust detection, recovery, and performance analytics for resilient environments.
From Risks to Resilience: Leveraging CNCF Projects Against Kubernetes' OWASP Top 10
Explore strategies to mitigate OWASP Kubernetes Top Ten security risks using CNCF projects. Learn actionable insights to enhance the security of your Kubernetes deployments.
Security-Focused Chaos Engineering - The Lasso for AI Security Threats
Explore proactive AI security testing using Secops-Chaos, an open-source framework for encoding threat tactics as chaos experiments in Kubernetes environments.
Container Images and Security 101: 5 Need to Know Facts
Explore 5 essential facts about container image formats, security tools, and best practices for confident application deployment in cloud and Kubernetes environments.
Threat Modelling: How to Improve Your Kubernetes Security Posture
Learn to enhance Kubernetes security through innovative threat modeling techniques, focusing on identifying risks in complex environments and improving overall security posture for development and SRE teams.
Drawing Lines in the Sand - Running Unprivileged eBPF in Kubernetes
Explore eBPF capabilities in Kubernetes, focusing on security permissions, Linux capabilities, and avoiding 'privileged:true'. Learn about fine-grained control and necessary privileges for different eBPF features.
Using Native OpenTelemetry Instrumentation to Make Client Libraries Better
Discover how native OpenTelemetry instrumentation enhances Azure client libraries, optimizing performance and reliability through stress testing and observability insights.
Implementing Auto Instrumentation for OTel Java Agent with GraalVM Static Compilation
Explore GraalVM static compilation for OTel Java Agent, focusing on auto instrumentation implementation and its impact on startup speed and memory usage in cloud-native environments.
OpenTelemetry for Mobile Apps - Challenges and Opportunities in Data Modeling and API Design
Explore challenges and solutions in implementing OpenTelemetry for mobile apps, focusing on data modeling, API design, and capturing dynamic client-side environments.
Monitor Docker Containers with cAdvisor, Prometheus, and Grafana
Learn to monitor Docker containers using cAdvisor, Prometheus, and Grafana. Set up a comprehensive monitoring system to track container resources and performance in real-time.
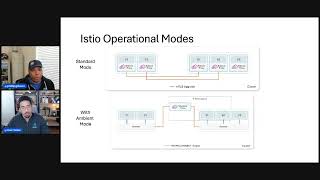
Istio Ambient - Inside a Contributor's Journey
Explore the journey of an Istio Ambient contributor, gaining insights into the development process and challenges faced in advancing cloud native computing technologies.
Thinking Like a Threat Actor in Kubernetes Environments
Explore threat actor mindsets to enhance Kubernetes security. Learn proactive defense strategies and vulnerability assessment techniques for robust cloud-native environments.
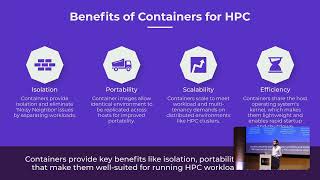
HPC with Containers on Ubuntu - Enroot and Pyxis Implementation
Learn to install and configure Enroot and Pyxis for running containerized applications on Slurm clusters, simplifying HPC workflows and enabling Ubuntu-based containers across diverse infrastructures.
Things You Always Wanted to Know About Building Platforms
Explore common pitfalls, patterns, and lessons learned in platform engineering. Discover effective strategies and Docker's role in building robust platforms, with insights on YAML, testing, infrastructure, and GitOps.
Kubernetes Insider - Docker Desktop Extension for Elevating Kubernetes Productivity
Explore a Docker Desktop Extension that automates port-forwarding and simplifies access to web services in Kubernetes, enhancing productivity for developers and learners alike.