Navigating a Secure Clean Energy Transition - Cybersecurity Challenges and Solutions
Explore the cybersecurity challenges and policy implications of clean energy adoption, focusing on supply chain vulnerabilities, security strategies, and balancing economic pressures with sustainability goals.
SQL Injection Isn't Dead: Smuggling Queries at the Protocol Level
Explore advanced SQL injection techniques through protocol-level query smuggling, revealing how attackers can bypass security measures and exploit database connections for authentication breaches and data theft.

The Darkest Side of Bug Bounty - Understanding Problems and Solutions in Bug Bounty Programs
Uncover the hidden challenges, secrets, and realities of bug bounty programs through expert insights on navigating relationships between hunters, clients, and platforms.
Practical Exploitation of DoS in Bug Bounty Programs
Discover practical techniques for identifying and exploiting DoS vulnerabilities in bug bounty programs, covering N+1 errors, GraphQL crashing, and Cache Poisoning with real-world examples and responsible reporting practices.
Splitting the Email Atom: Exploiting Parsers to Bypass Access Controls
Discover techniques for exploiting email address parsing vulnerabilities to bypass security controls, spoof domains, and access protected systems through RFC-compliant manipulation.
The Hack, the Crash and Two Smoking Barrels - Automotive Cybersecurity Challenges
Dive into automotive cybersecurity challenges through real-world stories and demonstrations, exploring vehicle architecture vulnerabilities and industry practices while witnessing live ECU hacking and security testing scenarios.
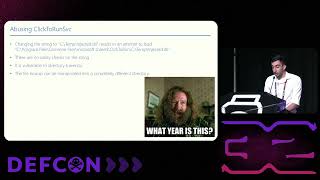
Manipulating Shim and Office Infrastructure for Code Injection and Privilege Escalation
Delve into advanced Windows exploitation techniques, focusing on stealthy shim manipulation and Office infrastructure vulnerabilities for code injection and privilege escalation attacks.
Spies and Bytes: Victory in the Digital Age
Delve into modern cyber warfare insights from General Nakasone's leadership at NSA and U.S. Cyber Command, exploring national security strategies, threat responses, and the future of digital conflict.
Reflections on a Decade in Bug Bounties - From Novice to Seasoned Hunter
Gain insights into the evolution of bug bounty hunting through a decade-long journey, from basic vulnerability reporting to crafting critical impact chains, with perspectives from both hunter and triage sides.
QuickShell: Remote Code Execution Attack Chain Analysis in Quick Share
Uncover critical security vulnerabilities in Google's Quick Share protocol, including an RCE attack chain, HTTPS MITM techniques, and protocol analysis for both Windows and Android platforms.
Signature-Based Detection Using Network Timing - Malware Traffic Analysis
Explore advanced malware detection techniques using network timing patterns and Python, learning to identify malicious behavior through transaction intervals rather than traditional code signatures.

Outlook Unleashing RCE Chaos: Understanding CVE-2024-30103
Dive into the critical Outlook security vulnerabilities, exploring RCE exploits through COM objects, NTLM leaks, and essential mitigation strategies for enterprise protection.
Detecting Persistent Threats on Draytek Devices - Security Assessment and Mitigation Tools
Discover how to detect and mitigate persistent threats on Draytek devices through firmware analysis, reverse engineering, and custom security module development for enhanced network protection.
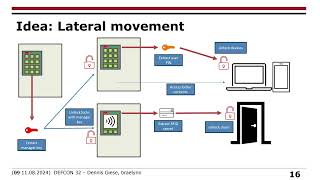
Open Sesame - Vulnerabilities in Electronic Smart Lockers and Cabinets
Explore physical and side-channel vulnerabilities in electronic smart locks, focusing on PIN and RFID security risks in organizational locker systems and shared spaces.
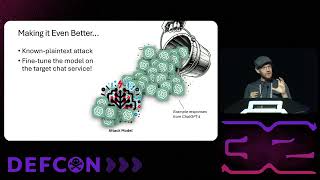
A New Side Channel Attack on AI Assistants - Exploiting Vulnerabilities in Encrypted Messages
Uncover a critical side-channel vulnerability affecting AI assistants like ChatGPT, exploring how encrypted conversations can be intercepted and the broader implications for privacy and security.
Xiaomi Mobile Security Vulnerabilities - Regional Exploit Analysis and Pwn2Own Competition
Delve into the behind-the-scenes journey of exploiting Xiaomi 13 Pro at Pwn2Own Toronto 2023, exploring regional security variations and the challenges of mobile device exploitation.
Abusing OIDC Authentication for Cloud Security Vulnerabilities
Dive into OIDC security vulnerabilities, exploring authentication mechanisms, potential misconfigurations, and real-world attack vectors in cloud environments through CI/CD workflows and identity providers.
Defeating ATM Disk Encryption - Security Vulnerabilities in Vynamic Security Suite
Delve into critical ATM security vulnerabilities, focusing on Diebold Nixdorf's VSS encryption weaknesses, exploitation methods, and essential defense strategies for financial systems protection.
Windows Downdate: Downgrade Attacks Using Windows Updates
Discover how to exploit Windows Update vulnerabilities to craft downgrade attacks, bypass security features, and compromise system integrity - from kernel to virtualization stack.
Security Vulnerabilities in Video Surveillance Systems and Supply Chain Analysis
Explore security vulnerabilities in surveillance systems, focusing on NVR devices from major vendors like Hikvision and Dahua, while examining supply chain risks and exploitation scenarios.
MaLDAPtive: LDAP Query Obfuscation and De-Obfuscation Techniques
Dive into advanced LDAP query obfuscation techniques and defense strategies, exploring a comprehensive framework for detecting and preventing directory services attacks through custom tokenization and parsing.