Breaking BMC: The Forgotten Key to the Kingdom - Security Vulnerabilities in Baseboard Management Controllers
Dive into the security vulnerabilities of Baseboard Management Controllers (BMC), exploring exploit chains and firmware implants in NVIDIA hardware with AMI MegaRAC BMC implementation.
What Is a GRC Hacker - Understanding Governance, Risk, and Compliance Security
Discover the role and mindset of GRC (Governance, Risk, and Compliance) hackers in cybersecurity through expert insights and practical perspectives from DEF CON 31.
Bootsquad: Introduction to Secure Boot Exploitation and Defense
Dive into the world of cybersecurity and virtual reality as Joe Mast presents Bootsquad, exploring innovative security concepts and challenges in the DCGVR Village at DEF CON 31.
Taking Down Applications with Logic - DEF CON 31
Dive into advanced application security techniques and learn how logical vulnerabilities can be exploited to compromise web applications, demonstrated through real-world examples.
Social Engineering and Security Awareness in Virtual Reality
Dive into a thought-provoking keynote address from renowned security expert Jayson Street at DEF CON 31's DCGVR Village, exploring cutting-edge cybersecurity insights and industry perspectives.
NTLM Authentication Vulnerabilities and Exploits - A Final Analysis
Dive into critical NTLM authentication vulnerabilities, exploring new bugs, bypass techniques, and security control gaps in Windows systems before Microsoft phases out this protocol.
Grand Theft Actions - Abusing Self-Hosted GitHub Runners for Supply Chain Attacks
Dive into critical security vulnerabilities in GitHub Actions, exploring real-world attacks on self-hosted runners and learning how to prevent supply chain compromises in major open-source projects.
Finding and Exploiting Local Security Vulnerabilities in 1Password for MacOS
Explore critical security vulnerabilities in 1Password's MacOS app, including local vault exploitation, IPC weaknesses, and Chrome extension flaws that could compromise password security.
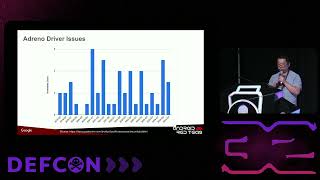
The Way to Android Root: Exploiting Smartphone GPU
Dive into advanced Android security research exploring Qualcomm Adreno GPU vulnerabilities, exploitation techniques, and kernel-level attacks to achieve root access, with practical mitigation strategies.
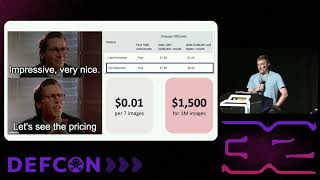
Secret Life of Rogue Devices: Lost IT Assets on the Public Marketplace
Uncover the alarming journey of lost corporate devices in public markets through data scraping, OCR clusters, reverse engineering, and conversations with underground collectors.
What History's Greatest Heist Can Teach Us About Defense in Depth
Explore the fascinating Antwerp Diamond Heist to understand defense-in-depth security principles through analysis of history's greatest vault breach and its modern cybersecurity implications.
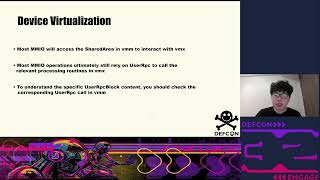
Bug Hunting in VMware Device Virtualization - Security Vulnerabilities and Attack Surfaces
Delve into VMware device virtualization security, exploring USB system vulnerabilities, SCSI device emulation, and VMKernel design flaws through real-world bug hunting experiences and discoveries.
Abusing Legacy Railroad Signaling Systems - Security Vulnerabilities and Threats
Uncover critical vulnerabilities in railway signaling systems through an analysis of accessible hardware tools and their potential impact on train operations, with focus on Spanish infrastructure.
BOLABuster - Harnessing LLMs for Automating BOLA Detection
Discover how to leverage LLMs for automated BOLA vulnerability detection in APIs and web applications, exploring BOLABuster's innovative approach to identifying critical security risks at scale.
HookChain: A New Perspective for Bypassing EDR Solutions
Discover a sophisticated EDR bypass technique combining IAT Hooking, dynamic SSN resolution, and indirect system calls to redirect Windows subsystem execution flow while remaining undetected by traditional security measures.

Beginner's Guide to Hacking IoT Devices - Building Your First IoT Security Testing Lab
Discover practical IoT hacking techniques, from selecting beginner-friendly devices to building an affordable toolkit under $100. Learn common vulnerabilities and methods to gain device access using simple tools and tactics.
Incubated ML Exploits: Backdooring Machine Learning Pipelines with Input Handling Bugs
Explore machine learning pipeline vulnerabilities and learn to identify, exploit, and defend against model backdoors through input handling bugs and systematic security approaches.
Hacker vs AI Perspectives in National Security and Cyber Warfare
Explore AI's role in national security through an ex-spy's lens, blending pop culture references with real-world cybersecurity insights and interactive demonstrations of AI systems.
Behind Enemy Lines: Engaging and Disrupting Ransomware Web Panels
Dive into advanced strategies for infiltrating and disrupting ransomware operations by targeting their web panels, APIs, and command centers while gathering vital intelligence on threat actors.
The XZ Backdoor Story: How a Supply Chain Attack Nearly Compromised SSH Servers
Uncover the gripping investigation of the XZ backdoor incident, exploring the mysterious maintainer Jia Tan, technical analysis of the compromise, and crucial lessons for open-source security.
Top War Stories from Bug Bounty Hunting - High-Severity Exploits and Discoveries
Dive into real-world bug bounty hunting experiences, exploring high-severity vulnerabilities worth $10k-$60k, from simple RCE exploits to complex PII leakages, with detailed technical insights and lessons learned.