Mastering Automotive Language Models and Edge Deployment in 2024
Explore how Small Language Models revolutionize automotive AI through edge computing, focusing on optimization techniques, deployment strategies, and real-world applications in vehicles.
Preventing DoS Attacks in Node.js Applications - Security Best Practices
Master essential security techniques for protecting Node.js applications from DoS attacks, covering JSON parsing, XML bombs, regex vulnerabilities, and storage operations optimization.
Machine Unlearning - Addressing Bias, Privacy, and Regulation in LLMs and Multimodal Models
Explore techniques for machine unlearning in AI models, focusing on bias removal, data privacy, and regulatory compliance while maintaining model performance and fostering responsible AI development.
Privacy Risks and Protections in Machine Learning Systems
Explore privacy vulnerabilities in ML systems and learn robust protection strategies to safeguard sensitive training data while maintaining system effectiveness and user trust.
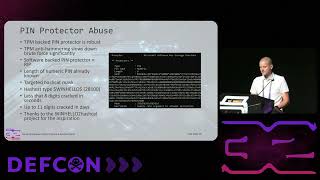
Abusing Windows Hello Authentication Without Biometric Data
Delve into Windows Hello's security vulnerabilities and authentication mechanisms, exploring attack vectors and hardware protection bypasses for biometric authentication without physical compromise.
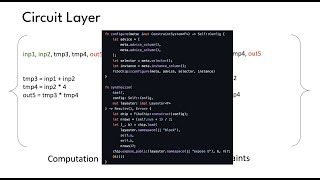
Security Vulnerabilities in ZK-SNARKs and Their Application in ZK-Rollups
Explore critical security vulnerabilities in zk SNARK systems and their implications for zk rollups, focusing on systematic analysis and potential mitigation strategies in blockchain scaling solutions.
What Is Going On In Your Source Code? Understanding Software Component Analysis in Plain Language
Gain insights into software supply chain security concepts like SBOM, VEX, and SLSA, understanding their importance in protecting organizations from emerging security threats.
Scorecard at Scale: Old and New Possibilities for Lifting Security on All Repositories
Discover strategies for implementing OpenSSF Scorecard at scale, exploring various tools and methods to assess, monitor, and enhance repository security across large organizations.
Navigating the Quantum Readiness Journey: Hands-on Guidance for Starting Your Migration
Explore quantum computing's impact on cybersecurity and learn practical steps for implementing quantum-resistant cryptography, focusing on crypto agility, standardization efforts, and migration strategies.
Supply-Chain Security: What Helping 200 Projects Improve Their Security Looks Like
Discover how Google's Open Source Security Team helped 200+ projects improve their supply-chain security, with insights on maintainer collaboration and practical security implementation strategies.
Save the Elephants - Secure Your PostgreSQL Databases with TDE
Discover essential PostgreSQL database security through Transparent Data Encryption (TDE), protecting sensitive data from unauthorized access and malicious attacks while maintaining performance.
Open Source Software Transparency for Acquisition - Making Security Trade-off Decisions
Explore software security measurement strategies and trade-off decisions for organizations using open-source components, focusing on vulnerability assessment, process metrics, and cybersecurity analysis.
Assessing Open Source Software Projects in the Software Supply Chain Security
Discover techniques for evaluating open source software trustworthiness through process assessment, risk analysis, and supply chain practices, with insights from DoD's Unified Platform project.
Role-Based Access Is So Yesterday: Revolutionizing Authorization with Open FGA
Discover how Open FGA revolutionizes authorization systems by implementing relationship-based access control, offering enhanced security and flexibility beyond traditional RBAC limitations.
Novel Sandboxing Techniques for Open Source Libraries Using eBPF and KRSI
Discover how to implement advanced sandboxing techniques for open source libraries using eBPF and KRSI technologies to enhance security and protect against vulnerabilities and exploits.
Artificial Intelligence Cyber Challenge - Overview and Releasing Research as Open Source Software
Discover how AI systems can secure critical code through the AIxCC competition, focusing on vulnerability detection, fixes, and open-source research implementation strategies.
The Simple Yet Lethal Anatomy of an AI Attack
Dive into the anatomy of AI security threats through live demonstrations, exploring attack strategies from reconnaissance to LLM poisoning, and learn to defend against emerging vulnerabilities in AI systems.
A Glimpse Into Open Source Software Vulnerability Disclosure Practices
Explore current challenges and solutions in open-source software vulnerability disclosure, examining security advisories, bug bounty reports, and maintainer perspectives for improved OSS security practices.
PEP 740 and PyPI - Bootstrapping Provenance for the Python Ecosystem
Explore how PEP 740 enhances PyPI's security through digital attestations, integrating with Sigstore and SLSA to provide robust package provenance without complex key management.
Secure Numerical Computing is Hard: Lessons from 10 Years of Open Data Science and the Long Road Ahead
Explore key security challenges and lessons learned from a decade of open data science, focusing on enterprise adoption of ML/AI technologies and emerging threats in numerical computing.
The Simple Yet Lethal Anatomy of a Software Supply Chain Attack
Explore software supply chain vulnerabilities through an attacker's lens, examining open-source security flaws and defense strategies with practical demonstrations and countermeasures.