Why Having a Security Reference Architecture Matters
Explore the importance of security reference architecture in adhering to frameworks, achieving Zero Trust and SASE, and enhancing Security Operations for effective threat management.
Managing the Mobile Endpoint Attack Surface
Explore risk management for enterprise mobility, focusing on mobile threats and mitigation strategies. Learn from NCCoE's analysis of common mobile device security threats.
Do Attackers Use Algorithms to Evade ML - An In-the-Wild Phishing Case Study
Explore phishing evasion tactics and trends, including 11 current techniques and potential use of automated adversarial attacks. Gain insights from a 5-year study on ML phish evasion competitions and real-world evasive phishing sites.
The Art of Metawar - Hacking & Weaponizing the Metaverse to Redefine Reality
Explore the metaverse as the 6th domain of warfare, examining how tech giants can manipulate reality, control thoughts, and influence behavior. Uncover mind-boggling privacy and security threats in immersive simulations.
Credential Sharing as a Service - The Dark Side of No Code
Explore attack techniques exploiting low-code apps in enterprises, revealing vulnerabilities throughout the cyber kill chain and highlighting the security risks of non-IT app development.
FAA - More Than Just a Regulator
Explore how the FAA balances regulation with collaboration to maintain aviation cybersecurity, addressing growing digital vulnerabilities in the world's safest aerospace system.
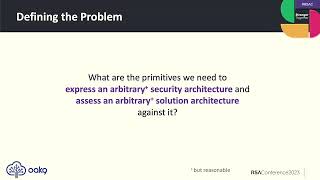
A Journey in Building an Open Source Security-as-Code Framework
Explore the development of an open-source security-as-code framework, its benefits, and real-world applications in securing complex infrastructures at scale.
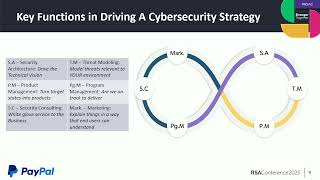
Connecting the Dots - An Effective Cybersecurity Strategy
Explore a novel cybersecurity approach combining threat modeling, architecture, and product management to implement secure systems efficiently and adapt to evolving threats.
From Public-Private Partnerships to Operational Collaboration
Explore the evolution of public-private cybersecurity partnerships into operational collaboration, featuring insights from key U.S. government agencies on lessons learned, successes, and future scaling plans.
Regulation and Risk When Your Customer's Browser Leaks Data
Explore data protection challenges in browsers, regulatory expectations, and strategies to manage risks associated with customer data leaks in web and mobile environments.
The Digital Trust Gap - How Cyber Pros Break Silos to Advance Digital Trust
Explore how cybersecurity professionals can collaborate across IT functions to strengthen digital trust, leveraging privacy, quality, risk management, and governance for enhanced enterprise and consumer confidence.
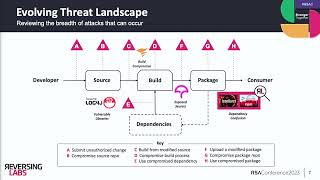
The Rise of Malware Within the Software Supply Chain
Explore malicious injections in open source software, their impact on the supply chain, and strategies to protect, detect, and respond to these evolving threats.
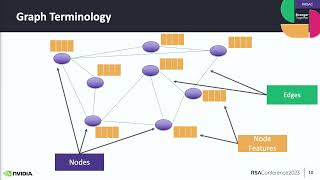
How to Map Networked Devices Using Graph-Based AI to Preempt Cyber Threats
Explore graph-based AI techniques for mapping enterprise networks, identifying vulnerabilities, and preempting cyber threats using passive data and open-source tools.
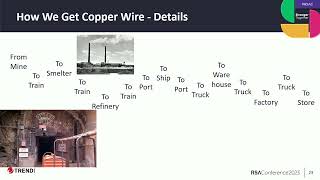
Responding to Supply Chain Vulnerabilities – A Maritime Perspective
Explore cybersecurity risks in ports and shipping, analyzing vulnerabilities and discussing potential solutions for improved detection and response in maritime infrastructure.
DevSecOps Worst Practices
Explore failed DevSecOps methods to avoid common pitfalls. Learn why certain practices fail and how to implement effective strategies for secure software development.
Protecting the Attack Surface and Data Silos of an EV Charging Network
Explore cybersecurity challenges in EV charging networks, focusing on protecting IoT devices, critical infrastructure, and operational data. Learn about attack surfaces and data silo protection in this emerging field.
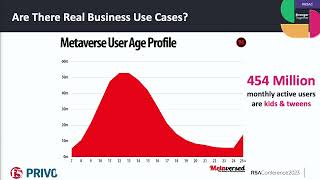
Metaspace Race - Securing Minors in the Metaverse - from the Start
Explore the unique challenges of protecting children's identities and privacy in the metaverse. Learn about risks, vulnerabilities, and strategies for ensuring security in this emerging virtual environment.
Aikido - Turning EDRs to Malicious Wipers Using 0-day Exploits
Discover how EDRs can be exploited to create undetectable wipers, deleting system files with unprivileged user permissions. Learn about this next-gen security threat and its implications.
Investigation and Incident Response Challenges for the Hybrid Enterprise
Industry experts discuss key trends in cyber investigations and incident response, exploring challenges and solutions for modern enterprises in a hybrid work environment.
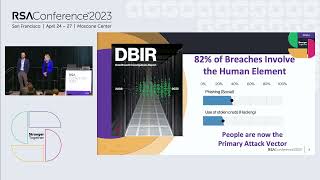
Employees Are the New Perimeter - How the Pandemic Shaped Workforce Risk
Explore how COVID-19 changed user risk in cybersecurity. Learn from 6M real user actions, understand work-from-home impacts, and discover strategies to identify and secure high-risk users in organizations.
The Five Most Dangerous New Attack Techniques
Expert panel discusses the most dangerous new attack techniques, their potential impact, and strategies for organizations to prepare and defend against emerging cyber threats.