Stranger Danger - Your Java Attack Surface Just Got Bigger
Explore cloud-native Java security risks, vulnerabilities, and best practices through live-hacking demonstrations, focusing on open-source dependencies and Docker images.
Wargames - Java Vulnerabilities and Why You Should Care
Explore Java vulnerabilities, security tools, and best practices to protect applications. Learn about CVEs, software supply chain risks, and DevSecOps strategies for robust Java development.
How to Implement DDoS Protection in GCP
Implementación práctica de protección DDoS en GCP: arquitectura, herramientas y demostración en vivo de ataques y defensa para aplicaciones web modernas.
Everything in Spring Security 6 Baked with a Spring Boot 3 Recipe
Explore Spring Security 6 updates with Spring Boot 3, covering new features, changes, and the authorization server project. Learn why upgrading matters and how to implement these enhancements.
Wasmer Things - An Upside-Down Guide to WebAssembly
Explore WebAssembly from a compiler's perspective, uncovering its inner workings and discovering why it's becoming a popular choice for sandboxed, memory-safe runtime environments.
Why Building Your Ship with Raw Materials is a Bad Idea
Explore software bill of materials (SBOMs), open source compliance, and best practices for secure, robust application development in the face of new regulations and vulnerabilities.
Keep Your Dependencies in Check
Explore tools and strategies for efficiently managing and updating dependencies in software projects, balancing security needs with continuous delivery of business value.
Wasmer Things - An Upside-Down Guide to WebAssembly
Explore WebAssembly from a lower-level perspective, uncovering its inner workings and discovering why it's becoming a popular choice for sandboxed, memory-safe runtime environments.
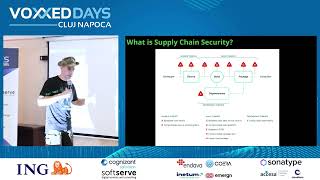
Supply Chain Security for OpenSource Projects
Explore supply chain security for open-source projects, covering potential threats, attack points, free tools, and strategies to protect against cyber attacks in software development.
Assume Compromise - Think Like a Hacker to Build Resilience
Explore hacker strategies to enhance cyber resilience. Learn why breaches escalate and how adopting an attacker's mindset can improve defense planning and preparedness for inevitable compromises.
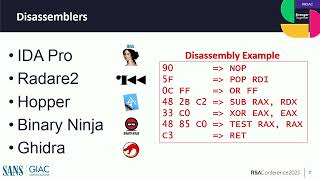
Finding Vulnerabilities through Static Analysis and Scripting
Discover critical vulnerabilities through reverse engineering and static analysis. Learn to set up a build environment and explore real-world examples in this inspiring session on bug hunting techniques.
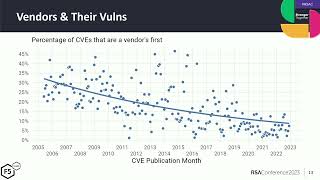
The Evolution of CVEs, Vulnerability Management, and Hybrid Architectures
Explore new research on vulnerabilities, including CVE trends, severity, and exploit code sharing. Learn about implications for vulnerability management in hybrid and multicloud architectures.
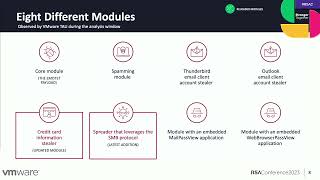
Emotet Exposed - Insider the Cybercriminal's Supply Chain
Uncover Emotet botnet's inner workings, including malware delivery, execution chains, and development lifecycle. Gain insights from VMware researchers who bypassed anti-analysis techniques to map its dynamic infrastructure.
Building International Coalitions to Scale Defense
Explore how international partnerships enhance global cybersecurity, focusing on combating ransomware and leveraging shared democratic values to achieve large-scale defense outcomes.
Cloud Security Made for the EU - Securing Data & Applications
Explore confidential computing and real-time compliance for ultimate data security in EU cloud transitions. Learn key strategies to satisfy data protection regulations and address CISO concerns.
Preparing for Quantum - A Pragmatic Approach towards Readiness
Explore quantum computing's impact on cybersecurity and learn practical strategies for achieving quantum readiness in your organization. Gain insights from industry experts on future-proofing security measures.
Forensics Skillset - Techniques for Extraction and Analysis of the Evidence
Intense technical session on evaluating infrastructure and recovering evidence left by hackers. Learn advanced forensic techniques to trace and analyze cyberattacks in corporate environments.
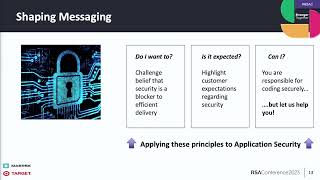
The Psychology of DevSecOps
Explore how DevSecOps teams apply psychological concepts to foster security-minded development cultures, increase collaboration, and cultivate buy-in from development partners.
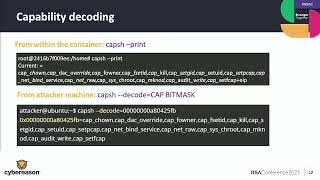
Container Escape - All You Need Is Cap - Capabilities
Explore container capabilities, their role in container escapes, and strategies to mitigate risks in this insightful session on container security internals.
Anatomy of the Attack - The Rise and Fall of MFA
Explore the vulnerabilities in multi-factor authentication through analysis of major 2022 attacks. Learn essential strategies to prevent breaches and strengthen your organization's security posture.
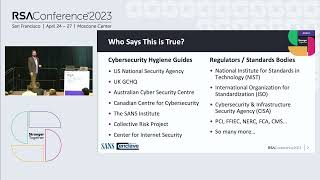
Crucial Cyber Hygiene Defenses for 2023
Learn essential cyber hygiene principles and technical defenses to protect against advanced attacks in 2023, as defined by leading security experts and organizations.