IAM The One Who Knocks
Exposing hidden risks in multi-cloud IAM, detailing access flaws, misconfigurations, and inconsistencies that can lead to unintended access and privilege escalation across cloud providers.
I Am Whoever I Say I Am - Infiltrating Identity Providers Using a 0-Click Exploit
Explore unauthenticated remote code execution in popular IAM solutions, covering past attacks, audit approaches, and vulnerability chaining for infiltrating identity providers.
Leveraging the Apple ESF for Behavioral Detections
Explore Apple's Endpoint Security Framework for macOS threat detection. Learn to utilize ESF data for basic and advanced behavioral-based detections, comparing old and new detection methods.
Let's Dance in the Cache - Destabilizing Hash Table on Microsoft IIS
Explore Microsoft IIS's Dynamic Hashing algorithm and its vulnerabilities. Learn about potential collision attacks on hash tables in web server architecture and their implications for cybersecurity.
Invisible Finger - Practical Electromagnetic Interference Attack on Touchscreen-based Devices
Uncover vulnerabilities in touchscreen devices through electromagnetic interference attacks, exploring practical methods to compromise security and user interaction on smartphones and tablets.
Kubernetes Privilege Escalation - Container Escape Equals Cluster Admin
Explore Kubernetes security vulnerabilities, privilege escalation techniques, and container escape risks. Learn to identify powerful system pods and implement mitigations to protect your cluster from potential attacks.
Internal Server Error - Exploiting Inter-Process Communication in SAP's HTTP Server
Explore SAP's HTTP server vulnerabilities and learn advanced exploitation techniques for memory corruption in the Internet Communication Manager, with real-world examples and demonstrations.
Industroyer2 - Sandworm's Cyberwarfare Targets Ukraine's Power Grid Again
Detailed analysis of Industroyer2 malware targeting Ukraine's power grid, comparing it to the original Industroyer and exploring its communication with ICS hardware using industrial protocols.
Cautious - A New Exploitation Method! No Pipe but as Nasty as Dirty Pipe
Unveils a novel exploitation technique surpassing Dirty Pipe, enabling arbitrary file overwriting and privilege escalation through double-free vulnerabilities, applicable across affected kernel versions.
Controlling the Source - Abusing Source Code Management Systems
Explore vulnerabilities in Source Code Management systems, including reconnaissance, user role manipulation, and repository takeover. Learn attack scenarios and defensive strategies for GitHub, GitLab, and Bitbucket.
Go With the Flow - Enforcing Program Behavior Through Syscall Sequences and Origins
Explore syscall-flow-integrity protection (SFIP) to enhance application security by limiting control flow across user-to-kernel transfers, addressing vulnerabilities in complex software systems.
Breaking Firmware Trust From Pre-EFI - Exploiting Early Boot Phases
Explore recent UEFI firmware security changes, focusing on Intel CPUs. Covers firmware mitigations in SMM/DXE and new attacks on Intel PPAM, offering unique insights from an offensive security perspective.
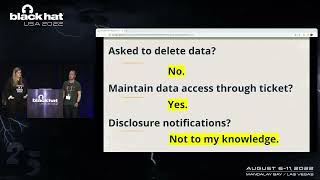
Bug Hunters Dump User Data - Can They Keep It? Well They're Keeping It Anyway
Explores legal and ethical implications of security researchers handling sensitive user data during bug bounty disclosures, examining responsibilities and potential consequences for all parties involved.
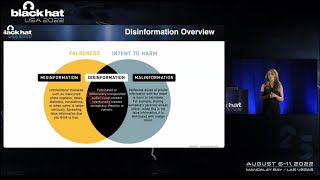
The Growth of Global Election Disinformation - The Role and Methodology of Government-Linked Cyber Actors
Explore how government-linked cyber actors influence elections through disinformation campaigns, focusing on a case study from Colombia's 2022 elections and strategies for detecting such operations.
The Journey of Hunting In-the-Wild Windows LPE 0day
Explore techniques for detecting and capturing in-the-wild Windows Local Privilege Escalation vulnerabilities, including methodology development and continuous improvement strategies.
Scaling the Security Researcher to Eliminate OSS Vulnerabilities Once and For All
Explore automated security vulnerability detection and fixing in open-source software, including techniques like OpenRewrite and control flow analysis for efficient, large-scale remediation.
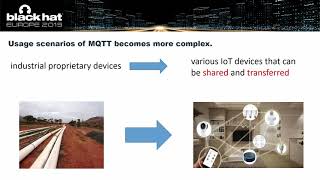
Security Holes in the Integration and Management of Messaging Protocols on Commercial IoT Clouds
Systematic study reveals vulnerabilities in IoT cloud platforms' MQTT integration, exposing risks of device control, DoS attacks, data theft, and status manipulation.
Hackers, Journalists and the Ethical Swamp
Investigative journalist analyzes five high-profile hacking incidents, exploring trends and tactics in media manipulation and collaboration between hackers and reporters.
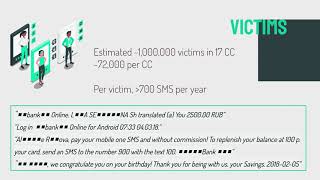
Money Doesn't Stink - Cybercriminal Business Insight of a New Android Botnet
Explore the inner workings of a cybercriminal group operating an Android botnet, including their hierarchy, challenges, and impact on victims' security.
Ghidra - Journey from Classified NSA Tool to Open Source
Explore NSA's journey in developing and open-sourcing Ghidra, a powerful software reverse engineering framework. Learn about its features, impact, and future developments.
The Future of ATO
Exploring the evolving landscape of Account Takeover (ATO) attacks, focusing on emerging threats, sophisticated techniques, and strategies to protect user accounts in the digital age.