There's No Place Like Production - Lessons from Incident Management
Explore production challenges, incident management, and structured logging. Learn from real-world experiences and gain insights into effective incident response and review processes.
Cracking the Code of Cloud Security - DevSecOps and Container Security
Explore cloud security challenges, container vulnerabilities, and DevSecOps strategies. Learn automated vulnerability management, configuration best practices, and network segmentation for enhanced protection.
Modernizing Authorization: From Basic Roles to Decoupled ABAC
Explore the evolution of authorization systems, from basic roles to decoupled attribute-based access control (ABAC), addressing scalability and compliance challenges in modern software development.
Mapping the Minefield of Open Source Software Risks - DevOps 2024
Explore open source software risks, vulnerabilities, and remediation strategies. Learn about software composition analysis, reachability, and semantic versioning for effective dependency management.
Set Up Reliable Monitoring and Alerts for Cloud Apps
Establish robust cloud app monitoring and alerting systems. Learn to create intuitive dashboards, set up effective alerts, and leverage failures for continuous improvement.
Building a Modern Enterprise Data Ecosystem on Cloud - Conf42 Cloud Native 2024
Explore modern enterprise data ecosystems on cloud platforms, covering storage, organization, consumption, pipelines, and machine learning. Learn key components and AWS challenges.
Bridging the Security Tool Gap for Go
Explore automated security fixing for Go, focusing on ICR's precision tools that address vulnerabilities efficiently and save development time.
Praemonitus Praemunitus - Using Actionable Alerts to Fix Problems
Optimize alert systems for efficient problem-solving. Learn when to alert, what to capture, and how to automate responses. Explore actionable alerts in Google Cloud for improved observability.
LLM SecOps - Securing Large Language Model Applications
Explore LLM SecOps: from understanding and building LLM applications to addressing security challenges and implementing practical safeguards for robust AI-driven systems.
Using Cloud Native Approach to Organize Data Protection
Explore cloud-native data protection strategies for Kubernetes, debunk myths, and learn about Canister for efficient backups. Includes practical demo and implementation insights.
Securing the Cloud: Multi-Layered Protection for Enterprises
Explore multi-layered cloud security strategies for enterprises, covering network, application, data encryption, access management, and advanced threat detection. Gain insights on best practices and future trends.
Sustaining Passion and Preventing Burnout in High-Stakes Software Development
Discover strategies to manage high-stakes workloads, prioritize effectively, and maintain team passion while preventing burnout in mission-driven software development.
Substrate Engineering - Foundations for AI-Assisted Development
Explore the importance of substrate engineering in LLM-based tools, focusing on improving programming languages and frameworks for enhanced code reliability and safety.
Dynamic Policy Enforcement for Privacy Techniques in Microservice Architectures
Implement advanced privacy techniques in microservice architectures using dynamic policy enforcement, ensuring compliance with regulations like GDPR and CCPA.
Fortifying gRPC Microservices - Beyond JWT with mTLS and SPIFFE
Explore secure gRPC microservices setup using mTLS and SPIFFE. Learn certificate management, key distribution, and modern alternatives to JWT for robust service-to-service authentication.
Fighting AI with AI: Securing Kubernetes for the Next Decade
Explore how GenAI is reshaping Kubernetes security and learn strategies to leverage AI for protecting deployments against evolving threats in the cloud-native landscape.
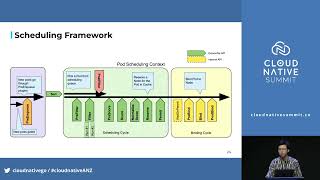
Safely Extending the Kubernetes Scheduler with WebAssembly - A Tale of Two Plugins
Explore WebAssembly as an alternative for extending Kubernetes Scheduler, understanding its benefits, challenges, and implementation details compared to the Scheduling Framework.
How Bumble Inc's Open Source Private Detector Is Helping Make the Internet Safer for Women
Explore Bumble's AI-powered Private Detector™: an open-source tool combating cyberflashing by detecting and blurring lewd images, making the internet safer for women.
Scaling Analytical Capabilities for Increasing Client Demand
Explore how NatWest Boxed leverages LLMs to create a text-to-SQL product, democratizing data access and scaling analytical capabilities to meet growing client demands.
The Government and the Art of Infrastructure Maintenance
Explore how Germany's Sovereign Tech Fund strengthens the open source ecosystem, addressing funding, career prospects, and contributor growth for sustainable digital infrastructure.
Elevating Cloud Forensics - Hypervisor-Level Methods for Evidence Unveiling
Explore innovative hypervisor-level methods for cloud forensics using AI and machine learning to detect and preserve potential evidence in cloud platforms.