Defense in Depth: Isolating Mesa From the Kernel
Explore advanced security techniques for isolating graphics drivers from kernel access, using virtualization and helper processes to protect against potential exploits in browser environments.
Kerberos and Authentication Updates in Samba - 2022
Discover the latest Kerberos authentication updates in Samba, including Heimdal integration, password management improvements, and Windows server compatibility features for enhanced domain controller operations.
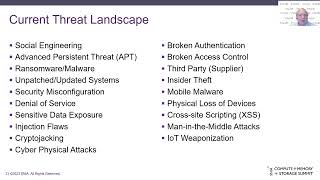
2023 Cybersecurity and Privacy Landscape
Explore the evolving cybersecurity and privacy landscape of 2023, examining key trends, challenges, and strategic approaches for protecting digital assets and maintaining data privacy in modern computing environments.
Computational Storage: Detecting Ransomware Using Flash Control Modules
Discover how computational storage in SSDs can detect ransomware attacks through IBM's Flash Control Modules, exploring key statistical indicators and security implementation across different system layers.
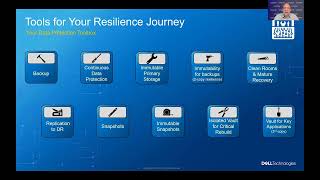
Cyber Recovery and Resilience: Understanding NIST Standards and Implementation
Discover essential strategies for cyber recovery and ransomware defense, exploring NIST guidelines and effective solutions for protecting critical data and ensuring rapid recovery across organizations of all sizes.
Fine Grain Encryption Using Key Per I/O
Explore advanced data security through fine-grain encryption techniques and key-per-I/O implementation in storage devices, focusing on system architecture and practical applications.
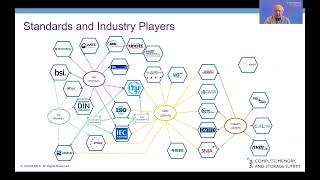
Storage Security Developments and Industry Trends 2023
Explore recent developments in storage security, including industry standards and defense mechanisms against data breaches and ransomware, with insights from Samsung's security expert.
Adopting the Zero Trust Paradigm - Security Framework Implementation
Discover how Zero Trust security frameworks eliminate implicit trust through continuous authentication and authorization, exploring international standards and government initiatives for enhanced cybersecurity.
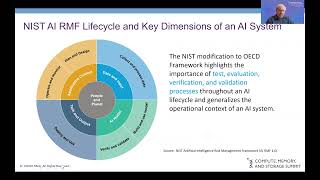
Security and Privacy Concerns in Artificial Intelligence Systems
Explore the dual impact of AI on security and privacy, examining defense strategies, unique threats, and emerging regulations shaping the technological landscape.
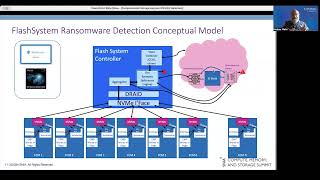
Breakthrough in Cyber Security Detection Using Computational Storage
Discover how IBM's FlashCore Module leverages AI-based detection within storage arrays to identify and combat ransomware attacks, offering innovative approaches to cybersecurity protection.
DevSecOps - Real Life Security Incidents and Lessons in Software Development
Explore real-world cybersecurity incidents and discover crucial lessons about integrating security measures throughout the software development lifecycle to prevent vulnerabilities and attacks.
Integrating AI Safely - Automating AI Failure Mode Testing in DevSecOps Pipelines
Discover how to automate AI failure mode testing in DevSecOps pipelines, ensuring secure AI integration through targeted strategies, metrics generation, and automated gates for enhanced application security.
From Novice to Catalyst - Scaling Security Tools with Metrics
Discover how to implement and scale security metrics effectively, from data extraction to visualization, while learning to leverage the Multivac framework for enhanced threat management and risk reduction.
Understanding Software Component Analysis (SCA) in Plain Language
Gain insights into software supply chain security concepts like SBOM, VEX, and SLSA, demystifying their importance for protecting organizational assets and code integrity.
NeuroCTI - A Custom Large Language Model for Cyber Threat Intelligence: Benchmarking, Successes, Failures and Lessons Learned
Explore the development journey of a specialized LLM for Cyber Threat Intelligence, including key benchmarks, outcomes, and critical insights from real-world implementation.
Automating Dark Web CTI Reports with RAG Insight for MISP Sharing
Discover how to automate Cyber Threat Intelligence reports from the dark web using RAG Insight, enabling efficient MISP sharing and enhanced threat detection capabilities.
Nothing To See Here - On Cloaking Malicious Web Content Delivery
Uncover sophisticated techniques used by cybercriminals to hide malicious web content delivery through cloaking mechanisms and learn effective detection and prevention strategies.
You Just Got a CTI Program Funded - Now What?
Discover essential strategies and practical steps for successfully implementing a newly funded Cyber Threat Intelligence (CTI) program, from resource allocation to measuring effectiveness.
Malware and Hunting for Persistence - How Adversaries Exploit Windows
Discover how adversaries exploit Windows systems through malware and persistence techniques, enhancing your cybersecurity defense capabilities and threat detection skills.
Unmasking Privacy: A Reproduction and Evaluation Study of Perturbation Techniques for Collaborative Filtering
Explore privacy-preserving techniques in collaborative filtering systems through a comprehensive reproduction study evaluating obfuscation methods and their effectiveness in data protection.
Tales of Program Crashes and Vulnerabilities - Software Security Research and Mitigation
Explore software security through vulnerability discovery, exploitation prevention, and compartmentalization strategies to enhance system protection and mitigate potential threats.