Building a Secure CI/CD Pipeline - Beyond Security Tools Integration
Discover effective strategies for optimizing security tools in CI/CD pipelines, moving beyond basic implementation to achieve meaningful security improvements and practical outcomes.
Security By Design
Discover essential principles and practices of integrating security throughout the software development lifecycle with guidance from security expert Ana Oprea.
Shielding Europe: DNS4EU's Pan-European Protective DNS Service
Discover how DNS4EU's protective DNS service enhances cybersecurity across Europe, exploring its implementation, benefits, and role in safeguarding digital infrastructure.
Indirect Syscalls: A Journey From High to Low
Dive into the mechanics of system calls, exploring both direct and indirect implementations while understanding their journey from high-level to low-level programming concepts and security implications.
The Current State of Ransomware
Explore the evolving landscape of ransomware threats, attack patterns, and defense strategies through expert analysis of current trends and real-world cases.
What We've Learned From Exposing Atlassian on the Internet
Discover key insights and lessons learned from exposing Atlassian's infrastructure to the internet, exploring security implications and best practices for protecting enterprise systems.
Fuzzing USB With Raw Gadget
Discover how to effectively fuzz USB drivers using Raw Gadget, exploring techniques for finding and exploiting vulnerabilities in USB device drivers through practical demonstrations.
Christmas Hancitor Malware Campaign Analysis
Dive into a detailed analysis of the Christmas Hancitor malware campaign, exploring its infection chain, delivery methods, and technical characteristics.
Breaking the Ransomware Tool Set - When an OPSEC Failure Became an Intel Goldmine
Dive into a revealing analysis of ransomware operations through a critical OPSEC failure, uncovering valuable intelligence insights and defensive strategies against cybercrime toolsets.
Exploring IPFS Threats
Explore potential security vulnerabilities and threat landscapes within the InterPlanetary File System (IPFS) protocol through expert analysis and real-world examples.
Bio-Lock - The Future and Ethics Around DNA Cryptography
Explore the emerging field of DNA cryptography, its future implications, and ethical considerations in data security and biological encryption systems.
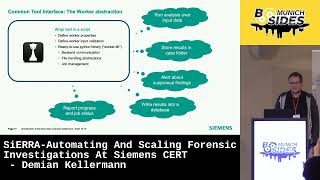
SIERRA - Automating and Scaling Forensic Investigations at Siemens CERT
Discover how Siemens CERT automates and scales digital forensic investigations through SiERRA, exploring practical approaches to handling large-scale security incidents efficiently.
Better Breach Detection With Deception Inception - Using Honeypots
Discover advanced breach detection techniques through deceptive honeypot strategies and learn how to implement effective security measures for enhanced threat identification.
Let Me Do It For You: Automating OSINT and Recon
Discover effective strategies for automating OSINT and reconnaissance processes to streamline cybersecurity investigations and threat intelligence gathering.
SOC Analyst's Arsenal - Essential Tools, Tips and Tricks for Effective Investigations
Master essential tools and investigative techniques for SOC analysis, featuring proven tips and tricks to enhance security incident response and threat detection capabilities.
Cracking The Chaos Ransomware Family
Dive into the technical analysis and decryption methods of the Chaos ransomware family, exploring its characteristics, vulnerabilities, and countermeasures.
Getting Ahead of the Bad Guys with Internet Scanning Data
Discover how to leverage internet scanning services like Shodan and BinaryEdge to identify adversarial infrastructure, detect threats early, and enhance defensive capabilities through practical hunting techniques and real-world examples.
Crushing Crumbs of Information: Using OSINT to Build Complete Target Profiles
Discover how to leverage seemingly insignificant data leaks from public websites to build comprehensive OSINT profiles, with practical examples and tools demonstrated through Brazilian case studies.
Creating Personal Disinformation Campaigns for Digital Safety and Privacy
Discover innovative strategies for personal security by creating deliberate digital noise and misinformation to protect yourself from stalkers while maintaining an active online presence.
Azure AD Reconnaissance Using OSINT Tools
Discover how to gather intelligence on Azure AD environments using OSINT tools, including domain enumeration, authentication methods, and user information for security assessment purposes.
Easy EASM - The Zero-Dollar Attack Surface Management Tool
Discover how to implement Easy EASM, a zero-cost tool for automated external asset discovery and monitoring, featuring daily Slack/Discord alerts and comprehensive asset tracking capabilities.