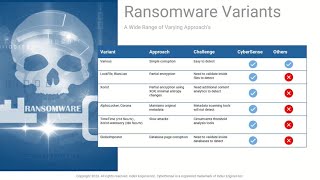
Ransomware Challenges and Last Line Defense with CyberSense
Discover modern ransomware attack strategies and defense mechanisms, focusing on content-based analytics and protective measures for organizational data security.
Homophonic Collisions - Hold Me Closer Tony Danza
Explore homophonic collisions in IT security with Justin Ibarra and Reagan Short. Gain insights into this unique aspect of cybersecurity from experts at a leading conference.
Bridging the Digital Generational Gap
Cybercrime expert Ritesh Bhatia offers practical guidance on protecting older generations from digital threats, addressing the technology knowledge gap and providing simple solutions for enhanced online safety.
Curiosity Killed the Hack
Explore ethical hacking tools and techniques, including insights on vehicle hacking, security issue detection, and corporate protection strategies from an experienced security analyst.
CyberCIEGE Scenario Design and Implementation
Explore CyberCIEGE's network security simulation game, its Scenario Development Kit, and techniques for creating customized scenarios to teach cybersecurity concepts through interactive storytelling.
Elevation of Privilege - Drawing Developers into Threat Modeling
Explore a game-based approach to engage developers in threat modeling, enhancing software security through interactive and non-threatening techniques.
An Argument for Game Balance - Improving Student Engagement by Matching Difficulty Level
Explore how balancing difficulty in cybersecurity competitions can improve student engagement and retention, addressing the decline in novice participation and promoting career interest.
SecurityEmpire - Development and Evaluation of a Digital Game to Promote Cybersecurity
Explore SecurityEmpire, a multiplayer game teaching cybersecurity to high school students. Learn about its design, implementation, and effectiveness in promoting information assurance practices through engaging gameplay.
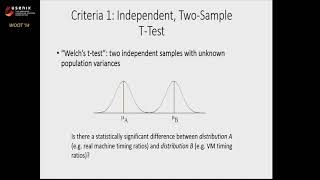
Tick Tock - Building Browser Red Pills from Timing Side Channels
Exploring browser-based red pills to detect virtual environments, their impact on web malware scanners, and potential mitigations for enhanced cybersecurity.
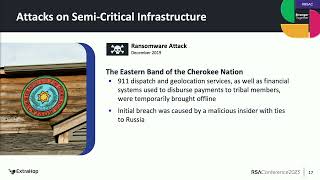
Semi-Advanced Threats vs the Semi-Critical Infrastructure
Explore how skilled hackers target vulnerable supply-chain dependencies, potentially affecting millions. Learn budget-friendly strategies to protect semi-critical infrastructure from disruptions.
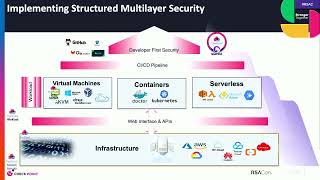
Building a DevOps Supply Chain on Zero Trust Principles
Discover how to implement Zero-Trust principles in DevOps supply chains, enhancing security from code to cloud and protecting against vulnerabilities that could compromise entire ecosystems.
Zero Trust Security for Your APIs
Explore Zero Trust Security for APIs: Learn the model, architecture, and implementation steps to protect your API ecosystem from attacks and abuse.
Let Me Show You How React Applications Get Hacked in the Real-World
Explore real-world React application vulnerabilities and learn how to prevent cross-site scripting attacks through secure coding practices and proper API usage.
Yomi - A Real-Life Sandbox Architecture and Implementation
Explore Yomi Sandbox's architecture and implementation for malware protection. Learn about its components, functionality, and advantages over commercial antivirus solutions.
Chaos Engineering for People - How We Resilienced Our Incident Response Team
Explore innovative chaos engineering techniques for strengthening incident response teams, enhancing readiness through simulated scenarios and practical drills.
How We Hacked LinkedIn and What Happened Next
Explore an advanced XSS attack on LinkedIn, dissecting its mechanics and aftermath. Gain insights into web security vulnerabilities and learn from a hacker's perspective.
How to Effect Change in the Epistemological Wasteland of App Security
Explore modern approaches to application security, moving beyond developer training to integrate security testing into agile development and DevOps practices for more effective and sustainable results.
Implementing Zero Trust Security in MLOps for Intelligent Energy Storage Systems
Discover how to implement Zero Trust security within MLOps for Energy Storage Systems, integrating Kubernetes and OpenStack environments for enhanced cybersecurity in critical energy infrastructure.
CI/CD Secret Management with Secret Zero - Managing Secure Pipelines
Explore effective secret management strategies for CI/CD pipelines, addressing challenges of token security, rotation processes, and permission controls in modern development workflows.
Does Your LLM Truly Unlearn? - A Simple Approach to Recover Unlearned Knowledge
Explore the effectiveness of LLM unlearning methods and discover how supposedly "forgotten" knowledge can be recovered through simple approaches in AI model training.
Inspect and Protect Distributed Environments with HCP Vault Radar
Discover how HCP Vault Radar enables security risk inspection and remediation in distributed environments, ensuring robust protection and ongoing security maintenance.